
News Archive
1920 stories · page 76 of 80Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Can Clothes Make You Invisible to Facial Recognition?
Does life feel Orwellian sometimes? One researcher has a solution for you: graphic tees that confuse the neural networks in surveillance cameras.
Iran, Russia, China Target Water Systems for Sabotage
Nation-state attackers breach water systems through weak passwords, exposed PLCs, and poor segmentation — not sophisticated malware.
Factoring RSA Keys with Many Zeros
Interesting research on a new class of weak RSA keys: keys with lots of zeros. It turns out that these keys are out in the wild. The badkeys project is an open-source service that checks public keys for known vulnerabilities. While developi
29th June – Threat Intelligence Report
Several organizations have reported significant cyber incidents. Polymarket experienced a supply chain attack resulting in the theft of $3 million in cryptocurrency. Japanese telecom KDDI disclosed a breach affecting up to 14.22 million email accounts. Tata Electronics, a supplier to major tech firms, suffered a data breach. Brazil's National Civil Defense platform was targeted with a fake alert, and the US National Association of Insurance Commissioners confirmed a data theft via a zero-day vulnerability. Additionally, a new AI-powered phishing service called EvilTokens has been identified, exploiting authentication methods to steal Microsoft 365 tokens.
From Bing Search to Ransomware: Bumblebee and AdaptixC2 Deliver Akira
A sophisticated cyberattack campaign, identified in July 2025, leveraged SEO poisoning to trick users searching for ManageEngine OpManager into downloading a trojanized installer. This led to the deployment of Bumblebee malware, which then established a command-and-control channel using AdaptixC2. The attackers exploited this access for credential harvesting, lateral movement, and ultimately deployed Akira ransomware across the victim's network.
Modernizing Global Vulnerability Standards For The Age Of AI
The rapid advancement of AI in discovering software vulnerabilities is outpacing current cybersecurity standards and processes. Traditional systems, designed for human-speed discovery and manual validation, are struggling to cope with the speed and scale at which AI can identify and chain weaknesses. This necessitates a modernization of global vulnerability standards, disclosure methods, and prioritization frameworks to effectively manage the evolving threat landscape.
Amazon Q VS Extension Flaw Leads to Cloud Credential Theft
Adversaries could plant a malicious repository that can execute arbitrary code and steal cloud credentials by exploiting the vulnerability, which showcases growing MCP risk.
Robot Police Officers
We’ve taken one small step towards robot police officers: a drone capable of disarming a suspect: In a June 22 video posted on the Sacramento County Sheriff’s Office’s Instagram page, an officer wearing goggles can be seen operating a drone
Cybercriminals Target Email Inboxes for Identity Theft
Cybercriminals are increasingly targeting email inboxes because they serve as a central hub for personal information and online accounts. Gaining access to an inbox can allow attackers to control other digital identities and access sensitive data.
Third-Party Breaches Teach Education Sector a Costly Lesson in Vendor Risk
Rising threats from third-party actors are forcing institutions to play defense to protect student data from ransomware and other attacks.
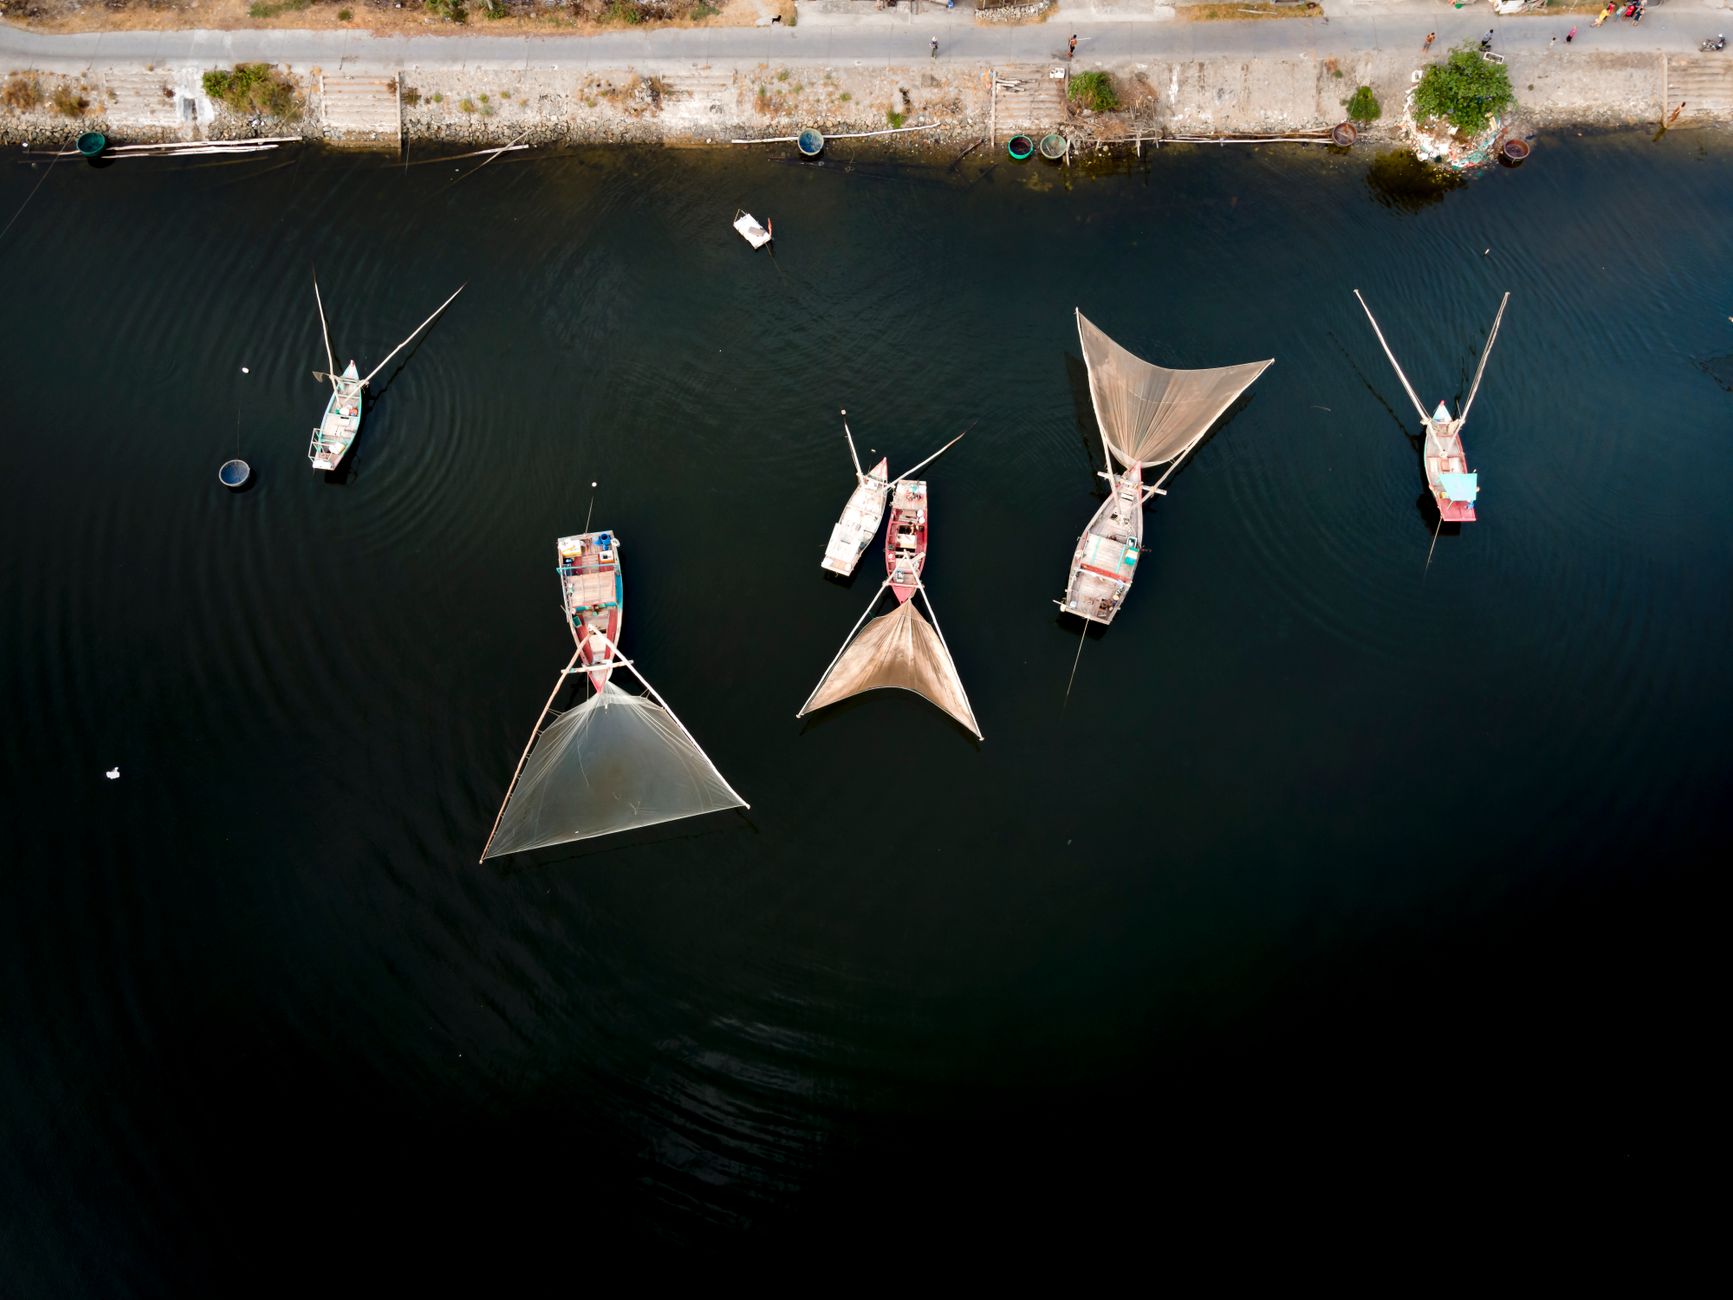
The Chinese Control the Majority of Argentina’s Squid Fleet
Chinese companies control nearly two-thirds of Argentina’s own squid fleet.
AI Decline? Confidence in Autonomous Penetration Testing Falls
Companies are still experimenting with automated AI systems to find security weaknesses, but fewer are relying on the technology.
Cisco Adds NHI to Security Stack With Astrix, WideField Acquisitions
Cisco joins a growing list of security platform providers that are betting that securing the agentic workforce means turning identity into the primary control plane.
Meta Is Testing Facial Recognition for Police and Military
We know that ICE wants to deploy eyeglasses with facial recognition that can identify people in real time. Turns out Meta is prototyping the feature with a Pentagon supplier. (Alternate news story.)
New Initiative Tackles Security for End-of-Life Open Source Software
A new program, the Open Source Sustainability Initiative, has been launched to address the security challenges associated with end-of-life open source software. Its primary aim is to assist organizations in effectively managing and securing these older projects, ensuring they remain compliant with relevant regulations.
AI Won't Wipe Out Entry-Level Cybersecurity Jobs
Artificial intelligence is not anticipated to eliminate entry-level positions within the cybersecurity sector. Instead, it is expected to create new job opportunities, especially for individuals who demonstrate strong human decision-making skills.
Meeting Trump's 2030 Quantum Deadline Will be Expensive, Complex
Meeting the 2030 quantum computing deadline, as proposed by former President Trump, is anticipated to be both costly and intricate. Key challenges include gaining clear visibility across diverse IT and operational technology systems, managing multiple vendor environments, and addressing discrepancies in update schedules and interoperability.
From CI/CD to Cloud Data: How Shai Hulud Persistence Leads to Redshift Breach
A security incident involving Shai Hulud has been detailed, starting with a compromise in the CI/CD pipeline that led to the exposure of Jenkins credentials. This initial breach allowed for privilege escalation within AWS, ultimately resulting in unauthorized access to Redshift data.
Thanks for Crushing the Submissions Inbox. We're Trying to Keep Up
The publication is currently experiencing a high volume of submissions, which is causing delays in their response times. They are actively working to process the incoming material and appreciate the community's understanding as they manage the increased workload.
Small Businesses Need Cyber Readiness for Resilience
Small businesses often have a larger attack surface than their size suggests. Achieving cyber readiness is presented as the initial and crucial step toward building resilience against potential threats.
Robinhood Cuts Access Approval Time to Support High-Velocity Development
Robinhood's application security team has streamlined the process for granting system access to its developers. This re-engineering aims to support faster development cycles while simultaneously enhancing security measures. The fintech company focused on making access both easier and more secure for its engineering teams.
In Less Than 24 Hours, Attackers Weaponize Cisco CUCM Flaw
A critical vulnerability affecting Cisco Unified CM and Unified CM SME deployments, which allows for server-side request forgery (SSRF) and root privilege escalation, was rapidly exploited by attackers. Threat actors weaponized the flaw within 24 hours of its public disclosure.
Russian APT 'Gamaredon' Upgrades Its Arsenal, Requiring New Defenses
The FSB state-sponsored operation has gotten a lot better at loading its malware and hiding its servers.
Beyond IOCs: AI-enabled threat intelligence
This week's newsletter explores how artificial intelligence can enhance threat intelligence capabilities. AI is expected to facilitate the creation of easily searchable data sources derived from intelligence reports, thereby improving access and utility of information for security professionals.