LIVE · cybersecurity feed
Live wire
How Cloudflare WAF helps protect against phpAfterShell and other critical PHP flawsCVE-2026-114938 · A Technical Guide to Mitigate Java4Shell with TruRisk EliminateCVE-2026-104995 · Dontdream BP Profile Search Vulnerability Listed As Exploited In VulnCheck KEVCVE-2026-54836 · YMC Filter SQL Injection Vulnerability Added to VulnCheck KEVCVE-2026-7542 · Slider Revolution Sensitive Information Exposure Added To VulnCheck KEVCVE-2024-8517 · SPIP External Control Vulnerability CVE-2024-8517 Added To VulnCheck KEVSean Cairncross out as national cyber directorVMware patches vCenter zero-day exploited in attacks since SeptemberASUS warns of critical hard-coded key flaw in Control Center ExpressCVE-2026-123890 · CVE-2026-123890: Critical Authentication Bypass in VMware vCenter
CVE-2026-86360critical

Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access

Dell has issued an urgent advisory to customers, recommending they patch a critical vulnerability in its System Update (DSU) tool that could allow attackers to gain root access on affected PowerEdge servers. The flaw, identified as CVE-2026-86360, carries a CVSS score of 9.6, indicating its severe potential impact.

ZeroDay News ·

Source: Security Affairs

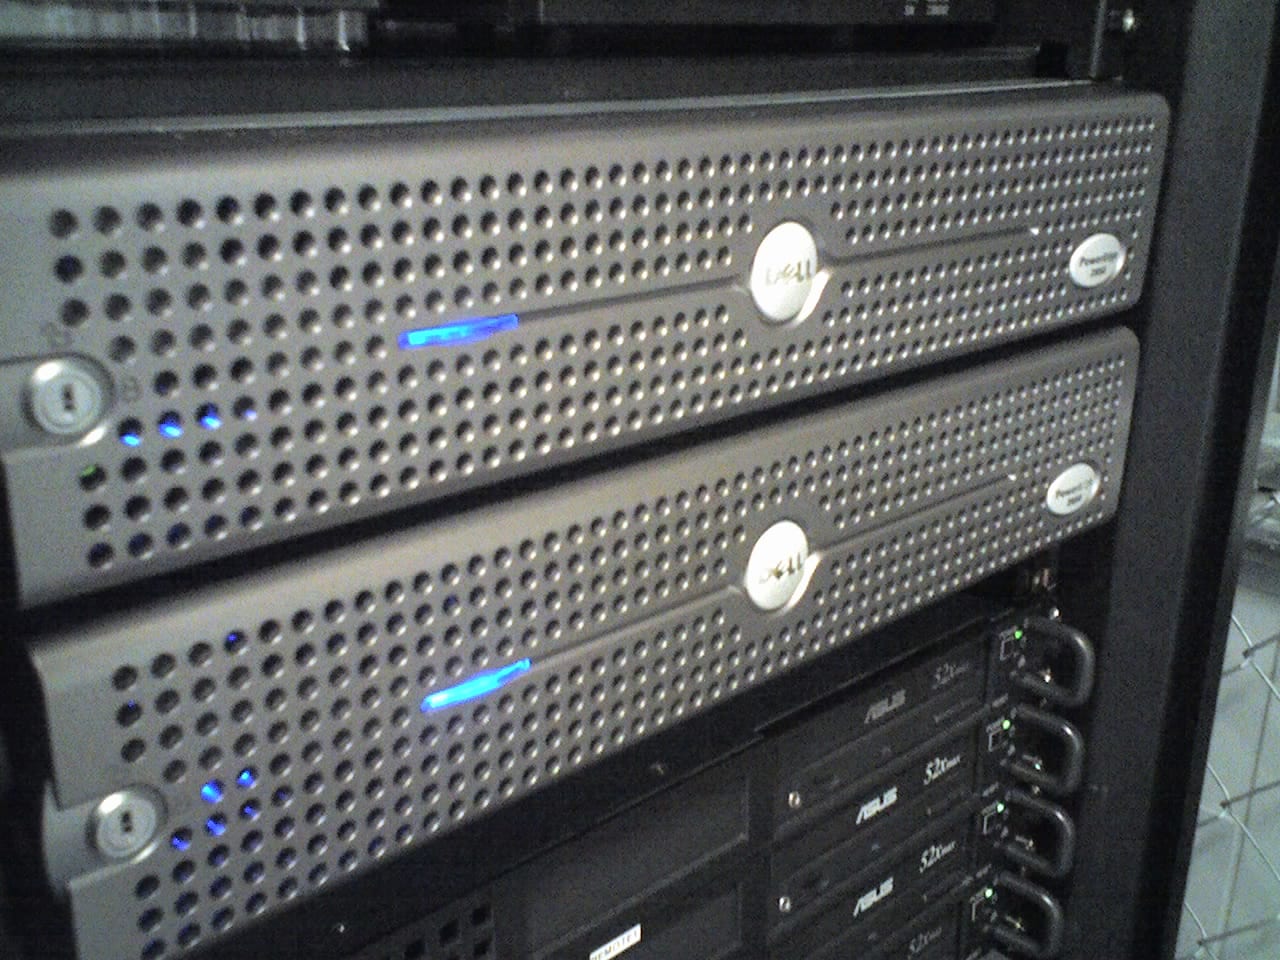
Photo: Dsv (Public domain) via Wikimedia Commons

Dell has issued an urgent advisory to customers, recommending they patch a critical vulnerability in its System Update (DSU) tool that could allow attackers to gain root access on affected PowerEdge servers. The flaw, identified as CVE-2026-86360, carries a CVSS score of 9.6, indicating its severe potential impact.

The vulnerability is a path traversal issue present in Dell System Update versions prior to 2.3.0.0. It could enable an unauthenticated attacker with remote access to execute arbitrary code with root privileges, potentially leading to a complete compromise of the vulnerable application and the underlying operating system. DSU is widely used by enterprise IT teams to deploy BIOS, firmware, and software updates on both Linux and Windows systems.

Dell's advisory specifically states that successful exploitation of CVE-2026-86360 could grant attackers filesystem access and full control over vulnerable servers. The company emphasizes the importance of applying the available security updates as soon as possible to mitigate the risk of exploitation.

In addition to the critical CVE-2026-86360, Dell addressed four other vulnerabilities in DSU versions preceding 2.3.0.0. Two of these, CVE-2026-86361 and CVE-2026-86362, are rated 8.2 and involve incorrect permissions or access controls that a low-privileged local attacker could exploit to achieve privilege escalation.

Another significant flaw, CVE-2026-63697, has a CVSS score of 7.6 and concerns improper certificate validation. This could allow a highly privileged remote attacker to execute code. Lastly, CVE-2026-71168, with a CVSS score of 7.3, is another path traversal vulnerability that could enable a low-privileged local attacker to achieve remote code execution.

Collectively, these vulnerabilities highlight multiple potential avenues for privilege escalation or code execution within the Dell System Update tool. Dell recommends that all customers upgrade their System Update installations to version 2.3.0.0 or later without delay.

As of the latest reports, Dell has not indicated any active exploitation of these vulnerabilities in the wild.


vulnerabilities in this storyCVE-2026-86360
vulnerabilitypatch
ShareXLinkedInWhatsAppFacebook

More News

view all →
CVE-2026-23871

CVE-2026-23871: WhatsApp Bug Helped Scammers Make Messages Look Legitimate

WhatsApp has released security updates addressing three vulnerabilities, one of which was actively exploited in a scam campaign designed to increase the perceived legitimacy of fraudulent messages. The company identified this specific flaw, tracked as CVE-2026-23871, while investigating and disrupting an ongoing fraud operation.

patch

PHP 8.6: Things are gonna get a lot more strict around here

The PHP development team has officially released PHP 8.6, marking the latest iteration of the widely used server-side scripting language. This release arrives following a turbulent period for the platform, which has faced a surge of security vulnerabilities since October. These flaws, which allowed unauthenticated attackers to trigger remote code execution (RCE) or crash PHP workers,…

security

4 Best XRP Lending Platforms Compared by Security, LTV, and Speed

A recent comparative analysis has evaluated four prominent platforms facilitating XRP lending, focusing on the trade-offs between security protocols, loan-to-value (LTV) ratios, and transaction speeds. The review examines CoinRabbit, Arch, Nexo, and Coinbase, providing a technical overview of how these services manage collateralized digital asset lending.

cloud

Dialing for Data: Inside the Com’s High-Profile Heists

Security researchers have identified a persistent and evolving campaign of vishing-led cyberattacks targeting data-intensive industries across the United States, the United Kingdom, and Australia. Since August 2026, a network of threat actors associated with the Com collective has conducted a series of data theft and extortion operations. These attacks primarily target the financial,…

phishing

Visa, Mastercard theft included info useful for phishing, but not draining bank accounts, say researchers

Visa, Mastercard, and JPMorgan Chase have confirmed they are investigating data breaches involving third-party service providers. The incidents came to light after a ransomware and extortion group known as n0n claimed responsibility for the thefts and began publishing samples of the exfiltrated data to pressure the financial institutions.

zero-day

China's 'Armory Castle' Lays Siege to VMware vCenter Zero-Day

A China-nexus threat actor identified as Armory Castle has been linked to the exploitation of a zero-day vulnerability affecting VMware vCenter. The activity was observed during the most recent cycle of security updates for the platform, suggesting the group maintained access to the vulnerability while the vendor was actively patching other known flaws in the software.



