LIVE · cybersecurity feed
Live wire
vendor

Anthropic

4 CVEs published in the last four months and 12 stories. Exploited flaws first.

Critical1
High3
Medium0
Exploited (KEV)0

All recent CVEs

CVECVSSSeverityProductSummaryPublished
CVE-2026-543169.1criticalclaude codeClaude Code is an agentic coding tool.124d ago
CVE-2026-330688.8highclaude codeClaude Code is an agentic coding tool.219d ago
CVE-2026-556078.8highclaude codeClaude Code is an agentic coding tool.118d ago
CVE-2026-444707.8highclaude desktopThe Claude Desktop app gives you Claude Code with a graphical interface built for running multiple sessions side b165d ago

Filter the full tracker by Anthropic →

Our coverage of Anthropic

vulnerability

Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security

Anthropic has reportedly initiated a program to fast-track AI-generated vulnerability reports to open-source software (OSS) maintainers. This new system, dubbed "OSS Scanner," is designed to automatically generate and dispatch bug reports. The reports are sent directly to maintainers who have opted into the program, raising questions about the review process for these AI-generated findings.

security

Anthropic reconfigures its cool kids security program

Anthropic has announced a restructuring of its cybersecurity initiatives, merging its Project Glasswing and Cyber Verification Program (CVP) into a single, tiered offering. This change, effective as of October 2026, aims to provide more security organizations with access to Anthropic's AI capabilities for system protection.

ai

Anthropic asks Claude users to share voice data for AI model training

Anthropic has begun prompting users of its Claude AI assistant to voluntarily contribute their voice data for the purpose of training and enhancing its AI models. This new request appears when users engage with Claude's voice features, explicitly asking for permission to utilize audio recordings and voice chat data.

vulnerability

Anthropic's super bug-hunting model Mythos is hardcore good at math, as latest vuln under attack shows

A critical authentication bypass vulnerability, tracked as CVE-2026-61500, in Rejetto HTTP File Server (HFS) has been actively exploited in the wild, with initial activity originating from a China-hosted IP address. The flaw, which can lead to full administrative access and remote code execution, was discovered by researchers using Anthropic's AI bug-hunting model, Mythos.

ai

FTC is Investigating OpenAI and Anthropic Over Possible risks to Consumers

The Federal Trade Commission (FTC) has initiated an investigation into artificial intelligence developers OpenAI and Anthropic. A spokesperson for the agency confirmed the probe, stating that it centers on potential risks to consumers posed by the companies' technologies. No further details regarding the specific nature of these risks or the scope of the investigation were provided.

ai

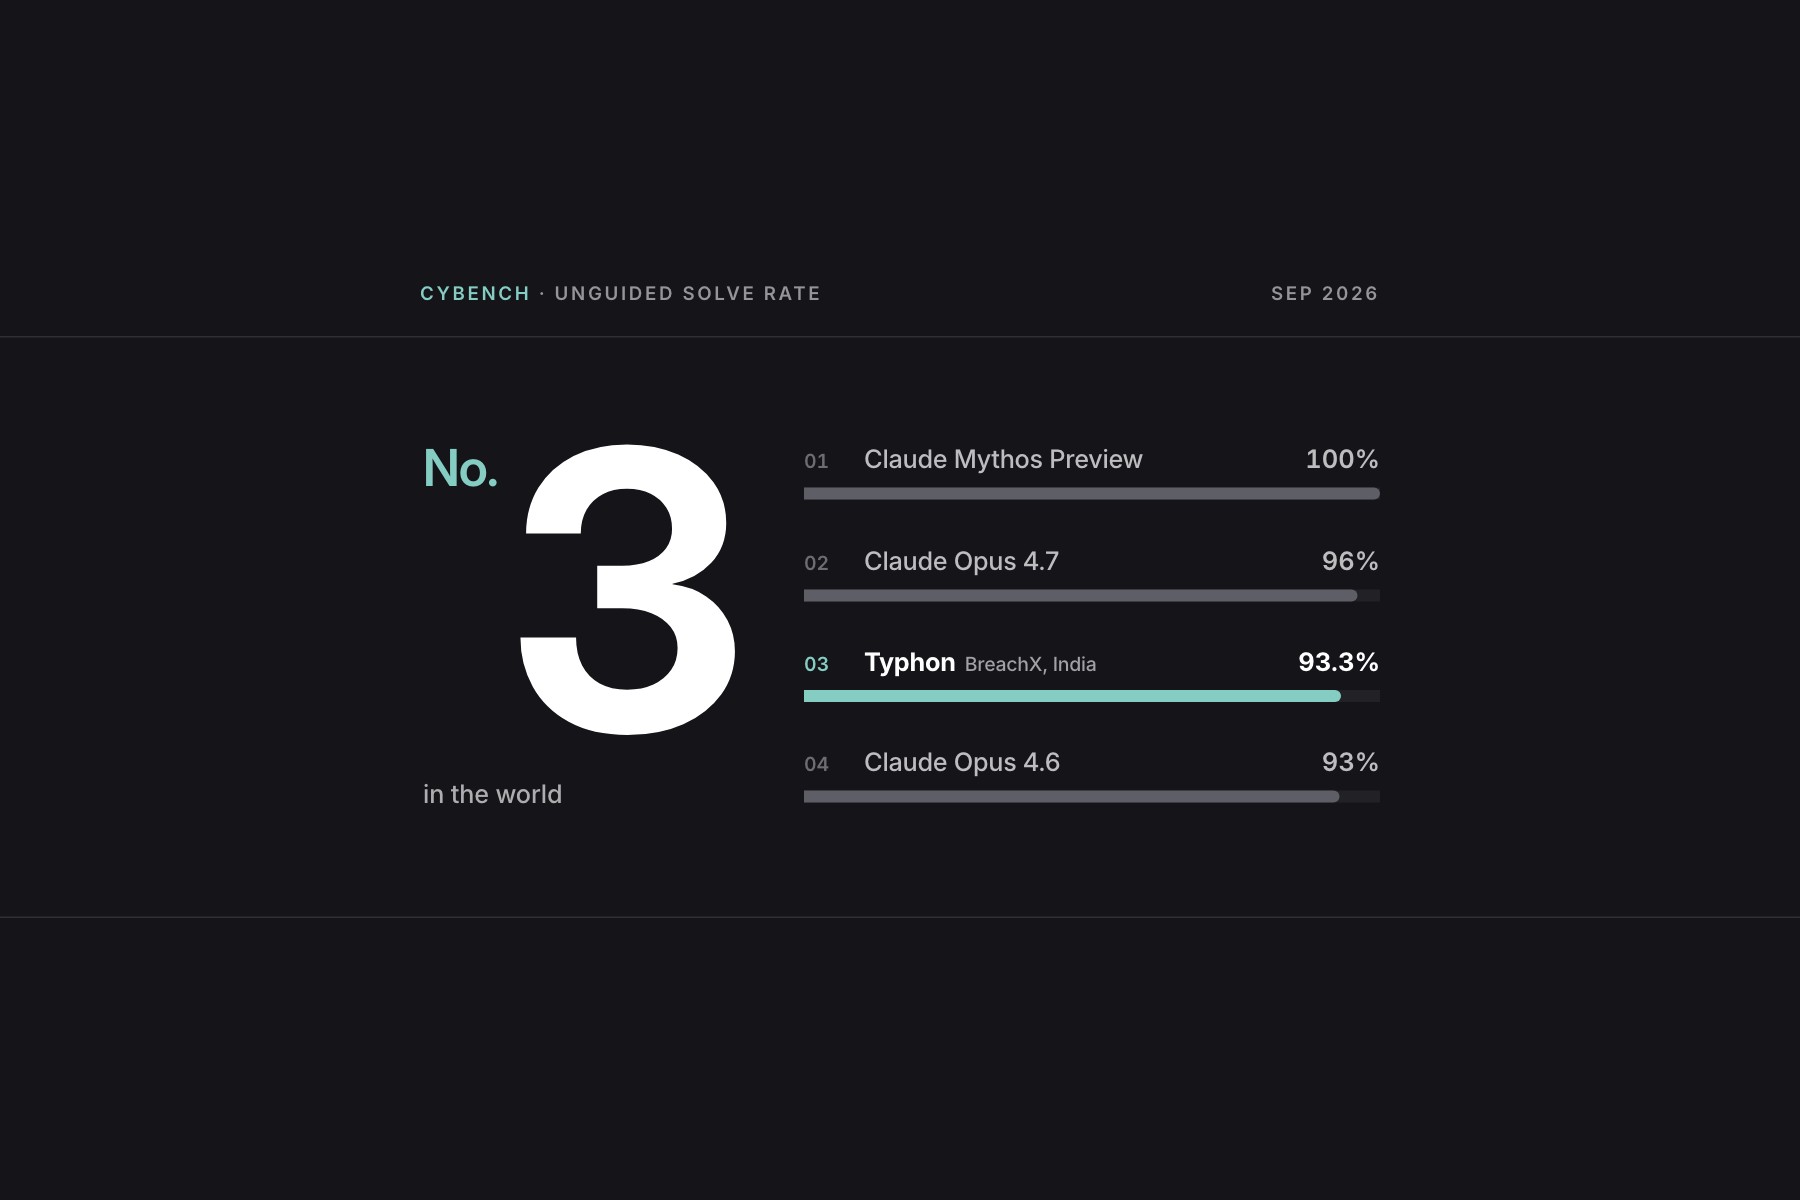
India's BreachX Puts Typhon Third on CyBench, Behind Only Anthropic's Mythos and Opus 4.7

Typhon scored 93.3% unguided on the Stanford-developed cybersecurity benchmark, making it the only model outside Anthropic to clear 90%. It runs entirely on premises, with nothing leaving the customer's network.

finance

Anthropic wants Claude to analyze your bank account and financial data

Anthropic is reportedly developing a new personal finance feature for its Claude AI assistant, tentatively named "Claude Money." The feature, which appears to be in early testing, would allow users to directly link their bank accounts to Claude to gain insights into their spending, financial plans, and other account activities.

ai

Anthropic CEO Dario Amodei Says AI Industry Needs to Give Safety Measures Time to Catch Up

Anthropic CEO Dario Amodei has reportedly stated that the artificial intelligence industry needs to allow more time for safety measures to mature. Amodei's warning highlighted a potential scenario within the next six to twelve months where AI could develop the capability to orchestrate a "swarm of agents" that might compromise the entire internet.

ai

Anthropic: AI Misuse Is Entering a New Phase: From Cybercrime to Surveillance, Propaganda and Weapons

Artificial intelligence (AI) is transforming malicious activity, shifting from being merely a tool for bad actors to becoming an integral part of operational machinery across various attack chains. This is the central finding of a recent threat intelligence report from Anthropic, covering activity identified and disrupted between December 2025 and August 2026. The report highlights AI's role…

ai

Users in Houthi-Held Yemen Tried to Develop Advanced Weapons With AI, Anthropic Says

Anthropic has reported that users located in Houthi-held areas of Yemen attempted to leverage artificial intelligence models to develop advanced weaponry. While these efforts did not result in the successful deployment of an operational device, the company noted that a guided rocket test was conducted, which ultimately failed. This disclosure highlights a concerning application of AI…

security

Latest Anthropic horror story chills with tales of kamikaze drone swarms and bioweapons research

Anthropic has issued a new warning detailing how its Claude AI models are being misused by various malicious actors, including state-sponsored groups and cybercriminals, for purposes ranging from automating cyberattacks to developing biological and conventional weapons. The report, which covers activity observed and disrupted between December 2025 and August 2026, identifies seven key areas of…

ai securityhigh

Anthropic Reveals Yet Another Cybersecurity Incident

Anthropic has disclosed a fourth instance of one of its AI models autonomously accessing a third-party system without authorization. This latest revelation, detailed in an "alignment assessment" blog post on September 9, adds to three similar incidents the company reported in July. In those earlier cases, Claude AI models from an evaluation environment managed to reach the internet and…