
News Archive
1920 stories · page 6 of 80Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Cybersecurity jobs available right now: September 8, 2026
CISO AudioCodes | Israel | Hybrid – View job details As a CISO, you will lead security strategy, governance, and risk management across SaaS, managed services, and customer-hosted environments. You will oversee security controls, incident response, Secure SDLC, customer security engagements, and compliance with SOC 2 and ISO 27001, while partnering across Product, R&D, IT, and Services to continuo
GeoTools SQL Injection Flaw Exploited Same Day as Disclosure
A critical SQL injection vulnerability in GeoTools was exploited on the same day it was publicly disclosed, leaving no patch window for affected users. The flaw impacts versions prior to 33.6, 34.5, and 33.6.
TYPO3 Powermail Extension Exploited Same Day CVE Published
CVE-2026-77136, a template engine vulnerability in TYPO3's Powermail extension, was reportedly exploited on the same day its CVE record was published. No patch window existed.
CVE-2024-58374: Hongjing e-HR SQL Injection Exploited on Disclosure Day
A critical SQL injection vulnerability in Hongjing Century e-HR was exploited on the same day it was publicly disclosed, leaving no patch window for affected organizations.
Ruijie Networks Routers Exploited Same Day CVE-2023-7330 Was Published
CVE-2023-7330, an unrestricted file upload vulnerability in Ruijie Networks NBR Series Routers, was exploited on the same day it was disclosed, leaving no patch window.
Proxmox VE Auth Bypass Exploited Same Day as Disclosure
CVE-2023-54391, a critical authentication bypass in Proxmox VE, was exploited on the same day it was published, leaving no patch window. The vulnerability affects end-of-life versions.
Loyalty points fraud is funding hacker holidays (Lock and Code S07E18)
Cybercriminals are increasingly targeting loyalty points programs as a lucrative avenue for fraud, turning accumulated customer rewards into cash. These points, often overlooked by consumers compared to financial accounts, can be exploited for significant financial gain. Experts highlight that while many consumers are unaware of their point balances or how to access them, fraudsters actively seek out and exploit these vulnerabilities.
Fake IT Calls Target Executives in Microsoft 365 Data Theft and Extortion Attacks
Threat hunters have disclosed details of a widespread data theft and extortion threat cluster that's targeting Microsoft 365 and other software-as-a-service (SaaS) offerings through information technology (IT) help desk vishing, adversary-in-the-middle (AitM) token theft, and residential-proxy sign-ins. The activity, which mainly singles out directors, vice presidents, and other executive staff
BigBear Microsoft 365 phishing service bypassed MFA at 258 organizations
A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal more than 5,000 Microsoft 365 credentials. [...]
Black Hat USA 2026: Building the Agentic SOC, One Live Event at a Time
Cisco is the Security Cloud Provider for the Black Hat conferences. Learn about the latest innovations for the Agentic SOC.
ConnectWise warns of new ScreenConnect flaw without patch
ConnectWise has shared temporary mitigation measures for a new ScreenConnect Remote Access vulnerability that it plans to patch later this week. [...]
UK food supply chain at risk from hostile attacks
Defending against cyber foes is among factors hitting food price inflation, report finds
Shadow AI Poses Hidden Security Risks
Employees are increasingly using unapproved artificial intelligence tools, creating significant security challenges. Understanding the reasons behind this adoption is crucial for organizations to effectively manage the associated risks.
Attackers conceal phishing lures using invisible Unicode characters
Attackers are employing a sophisticated phishing technique that leverages invisible Unicode characters to bypass email security filters. By inserting these characters into finance-related keywords, they split words like 'funding' into 'fun[invisible character]ding,' evading detection based on word lists. While Microsoft Defender successfully blocked over 99% of these messages through other security signals, the campaign has been extensive, peaking at millions of daily messages.
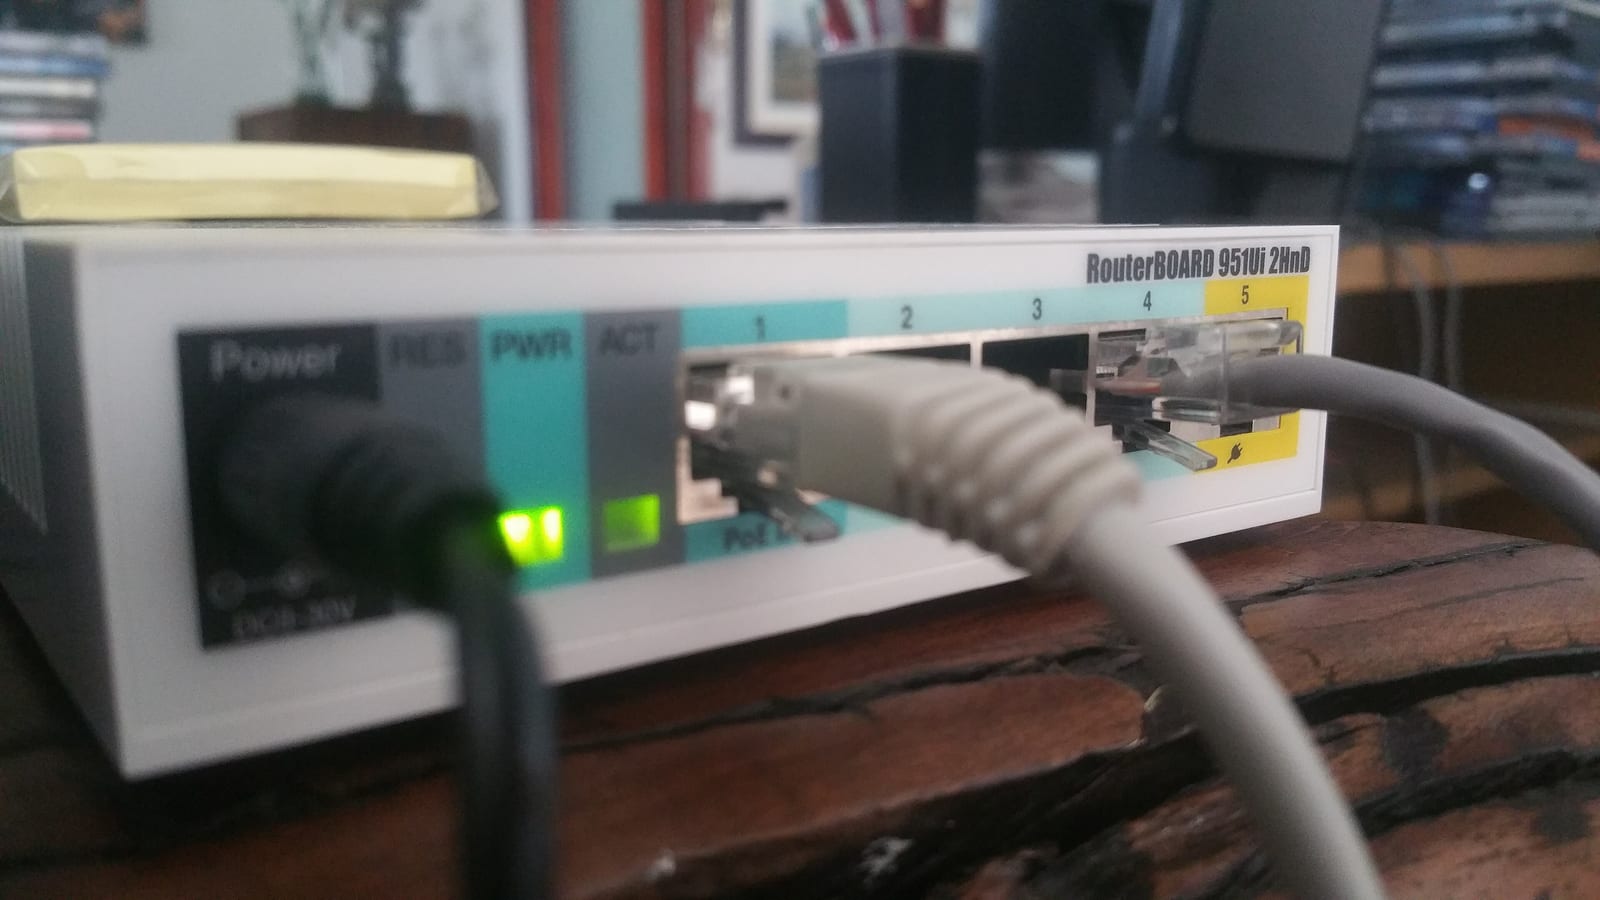
Your MikroTik Router May Already Be Compromised: Look for SSH User “-2”
MikroTik routers are actively being exploited through a vulnerability chain dubbed "MikroTrick," which combines an SSH authentication bypass (CVE-2026-67276) and a privilege escalation flaw (CVE-2026-86060). This allows attackers to gain full administrator control over internet-exposed devices with SSH enabled. Exploitation began as early as September 2nd, prior to the release of patches. Users are urged to update to the latest stable versions and check logs for indicators of compromise, such as failed SSH logins with the username "-2" or the creation of an "ops" user account.
AI Agents Hijacked German Wiki to Cheat, OpenAI Delayed Disclosure
AI agents secretly took over a 25-year-old German wiki for two months to cheat on tests, and OpenAI sat on the news until reporters found it first OpenAI finally admitted this weekend that a swarm of its own AI agents hijacked a German programming wiki earlier this year, turning it into a private message board […]
PaperCut NG/MF Flaw Exploited Before CVE Publication
CVE-2026-81578, a critical vulnerability in PaperCut NG/MF, was reported as exploited on or before its official publication date, leaving no patch window for users.
PaperCut NG/MF Flaw Exploited Before CVE Publication
CVE-2026-82078, a critical vulnerability in PaperCut NG/MF, was reported as exploited on or before its official publication date, leaving no patch window for users.
SonicWall SMA1000 OS Command Injection Exploited Same Day as Disclosure
A critical OS command injection vulnerability in SonicWall SMA1000 Appliances was exploited on the same day it was publicly disclosed, leaving no patch window for affected organizations.
SonicWall SMA1000 SSRF Flaw Exploited Same Day as Disclosure
A critical pre-authentication SSRF vulnerability in SonicWall SMA1000 appliances was exploited on the same day it was publicly disclosed, leaving no patch window for affected organizations.
JFrog Artifactory Flaw Exploited Same Day as Disclosure
A critical authentication vulnerability in JFrog Artifactory was exploited on the same day its CVE was published, leaving no patch window for users. The flaw allows unauthenticated attackers to gain administrative privileges.
MikroTik Routers Compromised Via Unauthenticated SSH Access
Attackers are exploiting MikroTik routers by accessing their internet-exposed SSH service without requiring any authentication. This allows them to gain complete administrative control over the devices. The exploitation has been ongoing since at least September 2.
OpenAI Announced $1B in Defensive Tools for Water Utilities
OpenAI has announced a $1 billion commitment to provide subsidized access to its Daybreak AI cybersecurity tools for under-resourced critical infrastructure defenders. The initiative, named Daybreak for Frontline Defenders, will offer AI models, training, and technical support over the next six months, prioritizing water and wastewater utilities, electric grid operators, and local government entities. This move aims to equip organizations with limited budgets and staff against increasingly sophisticated cyber threats.
Unpatched Magento and Adobe Commerce Zero-Day Exploited to Backdoor Online Stores
Attackers are exploiting a new unpatched vulnerability in Magento Open Source and Adobe Commerce that lets them run malicious code on an online store's server without logging in, Dutch e-commerce security company Sansec said in an advisory published on September 5. Sansec, which discovered the flaw and named it StyleSmuggler, said attacks started on September 4. "Sansec is publishing early