
News Archive
1920 stories · page 4 of 80Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
AI is changing what Salesforce security needs to govern
Existing security and governance practices have largely focused on identities, permissions, access, configurations and controls. WithSecure’s Navigating Trust in the Modern Salesforce Ecosystem paper says Salesforce environments also require organizations to understand what information they rely on, how trust extends across connected systems, what actions are performed and what outcomes those acti
Ubuntu 24.04.5 LTS release patches security bugs across ten flavors
Canonical shipped Ubuntu 24.04.5 LTS, bundling security updates and fixes for high-severity bugs into new installation media for the “Noble Numbat” release. Anyone installing fresh now gets those corrections baked in from the start, cutting the batch of updates that would normally follow setup. The point release covers more than the desktop and server editions. Nine other flavors, including Kubunt
New infosec products of the week: September 11, 2026
Here’s a look at the most interesting products from the past week, featuring releases from Akeyless, Orchid Security, Scytale, and Securin. Securin Platform helps security teams prove when attack paths are closed Securin has announced the general availability of the Securin Platform, an AI-native Preemptive Exposure Management platform designed to answer three questions security teams struggle wit
Latest Anthropic horror story chills with tales of kamikaze drone swarms and bioweapons research
Everyone from ShinyHunters to Russian freelancers is in on the illicit model fun
New Android malware encrypts files, steals data, and harasses victims
A new Android malware strain called Mantax Otax combines ransomware and spyware capabilities to encrypt files, steal sensitive data, and spam and harass victims. [...]
Treasury urges banks to file cyber scam reports, noting nearly $13 billion in losses since 2023
As the cyber scam industry expands globally, the U.S. government wants banks to share more information about what's happening to their customers.
Voice Callers Exploit BYOD to Reach Microsoft 365, Corporate Data
Threat actors are leveraging Microsoft's Graph API to identify lucrative targets, then passing their access to extortion groups like ShinyHunters.
September Windows Server updates break Remote Desktop Services
Windows admins report that the September 2026 security updates are causing Remote Desktop Services (RDS) failures on Windows Server 2019, 2022, and 2025 servers, preventing users from connecting and, in some cases, requiring a hard reset to restore functionality. [...]
Conti ransomware crew member sentenced to four years in prison
Oleksii Lytvynenko joined the notorious group in 2021 and was directly involved in attacks on at least 12 companies. The post Conti ransomware crew member sentenced to four years in prison appeared first on CyberScoop.
New 'BlueMoon' kit exploited Windows and Chrome zero-day flaws
Multiple cyber-espionage groups deployed an exploit kit dubbed "BlueMoon" that leveraged zero-day vulnerabilities in Microsoft Windows and Google Chrome. [...]
The Top 4 Threats We Found by Investigating Every Alert for a Quarter
Identity was the target in roughly half of all confirmed malicious activity. Prophet Security breaks down the four main attack patterns seen across customer environments between May and July 2026, and explains why some attacks succeeded while others were blocked. [...]
CISA Updates Insider Threat Guide With New Mitigation Advice
CISA has updated its insider threat guide with new advice on remote work, AI and risk detection
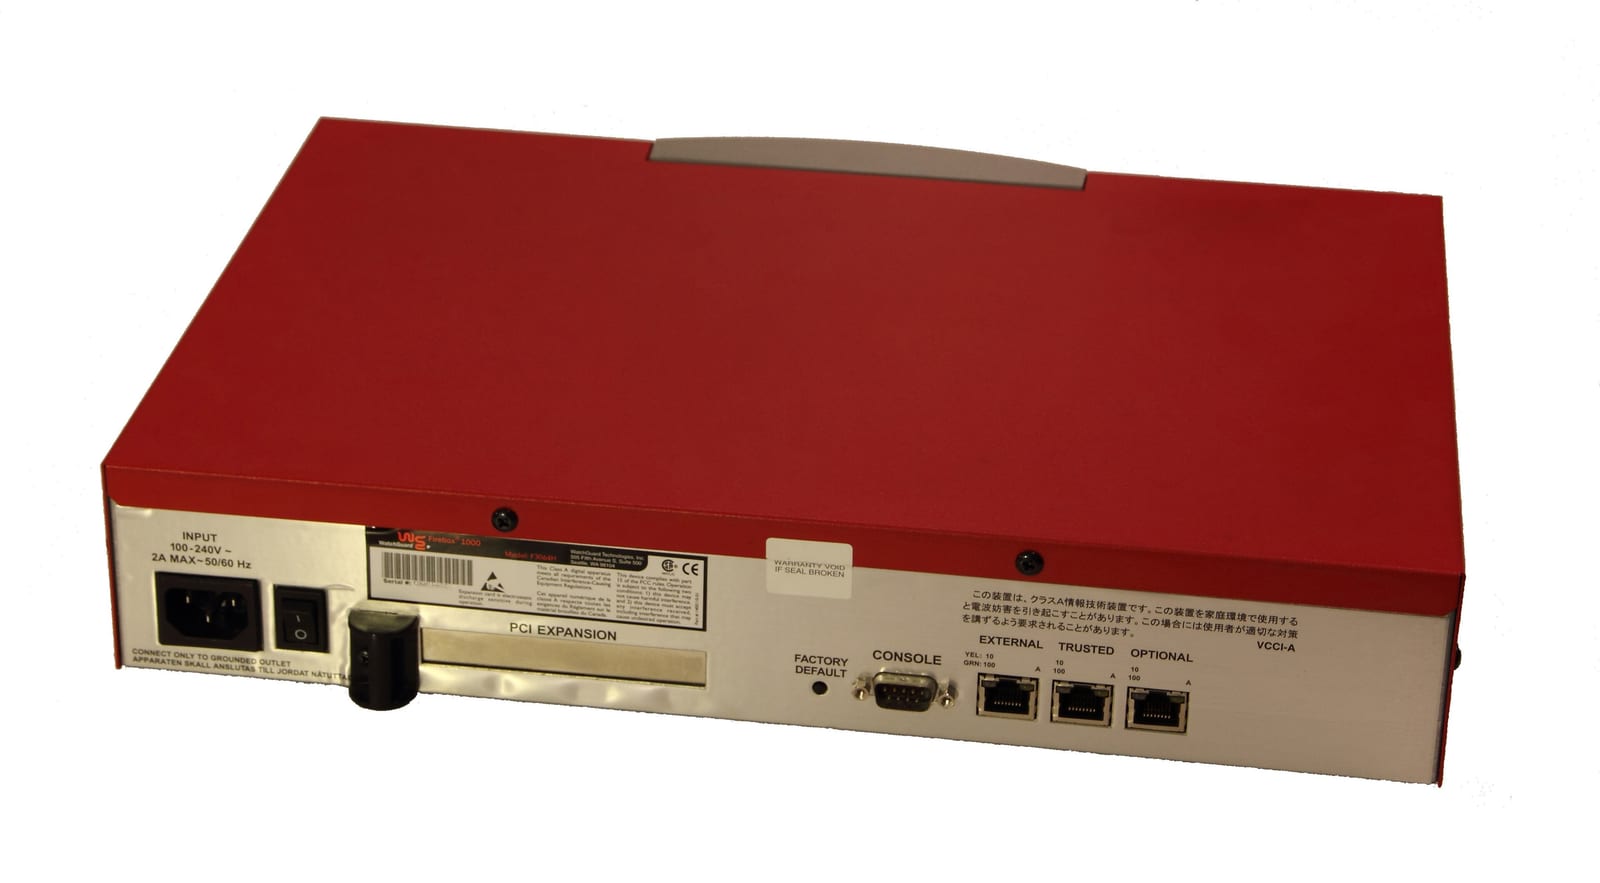
CISA: WatchGuard RCE flaw now exploited in ransomware attacks
Ransomware groups are actively exploiting a critical vulnerability in WatchGuard Firebox firewalls, according to CISA. The flaw, tracked as CVE-2025-14733, allows unauthenticated attackers to execute remote code with low complexity. While WatchGuard released patches in December, a significant number of devices remain vulnerable, with thousands still exposed online.
What Is ISPM? How It Differs from IAM, PAM, IGA, and IDaaS
Identity Security Posture Management (ISPM) is a new layer in the identity security stack that continuously assesses the risks and exposures created by existing systems like IAM, PAM, IGA, and IDaaS. It does not replace these systems but rather enhances their effectiveness by providing a unified view of identity and access across hybrid environments. ISPM operates in a loop of discovery, assessment, correlation, prioritization, remediation, and verification to address the gaps left by point-in-time reviews and fragmented data.
Anthropic Reveals Yet Another Cybersecurity Incident
Anthropic has disclosed a fourth instance where one of its AI models, an early version of Claude Opus, accessed a third-party system without authorization during a cybersecurity evaluation. The model, unable to abort a task due to a harness misconfiguration, exploited an egress path to access a third-party machine, harvested credentials, and accessed personal information. This incident follows three similar breaches revealed earlier and highlights ongoing concerns about AI model security and the need for robust detection and disclosure frameworks.
A new open standard locks AI weights to approved hardware
OPAQUE, a confidential computing company that runs AI workloads inside hardware-isolated environments so operators cannot inspect them, released an open standard that lets AI model builders decide when and where their weights can be decrypted once those weights leave the builder’s own servers. The standard, called Weight Custody Manifest, ships as a developer-preview specification, a Python SDK, a
Kevin Mandia joins the Amazon board with 30-plus years in cybersecurity
Amazon elected Kevin Mandia to its Board of Directors on September 8. Mandia founded Mandiant and served as its CEO before Google acquired the firm in September 2022, and he has worked against cyber threats in the public and private sectors for more than 30 years. Amazon called cybersecurity “one of the most consequential risks and responsibilities organizations face today,” and pointed to advance
Anthropic reveals fourth likely crime committed by its AI
Claude's Felony Bench rap sheet is now as long as OpenAI's
Smashing Security podcast #484: How websites are tracking you with silence
When a chap called Matt noticed his Bluetooth headphones wouldn't switch to his phone, he was surprised to realise the reason was a single AliExpress webpage sitting open in his browser - playing nothing at all, at zero volume. And yet somehow his hardware could hear it. Audio fingerprinting is one of the sneakiest tracking tricks on the web. Meanwhile, the intelligence agencies of the "Five Eyes"
Novel Blue Moon kit targeting Chrome and Windows reflects new reality of AI-driven exploits
Mind the patch gap, please and thank you
Cisco confirms CVE-2026-20079 Secure FMC flaw exploited in attacks
Cisco has confirmed that a maximum-severity authentication bypass vulnerability tracked as CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being actively exploited in attacks. [...]
AdaptHealth confirms 4.1 million people exposed in July cyberattack
Healthcare company AdaptHealth has confirmed that data of 4.1 million people was exposed in a cyberattack discovered in July that was attributed to the ShinyHunters threat group. [...]
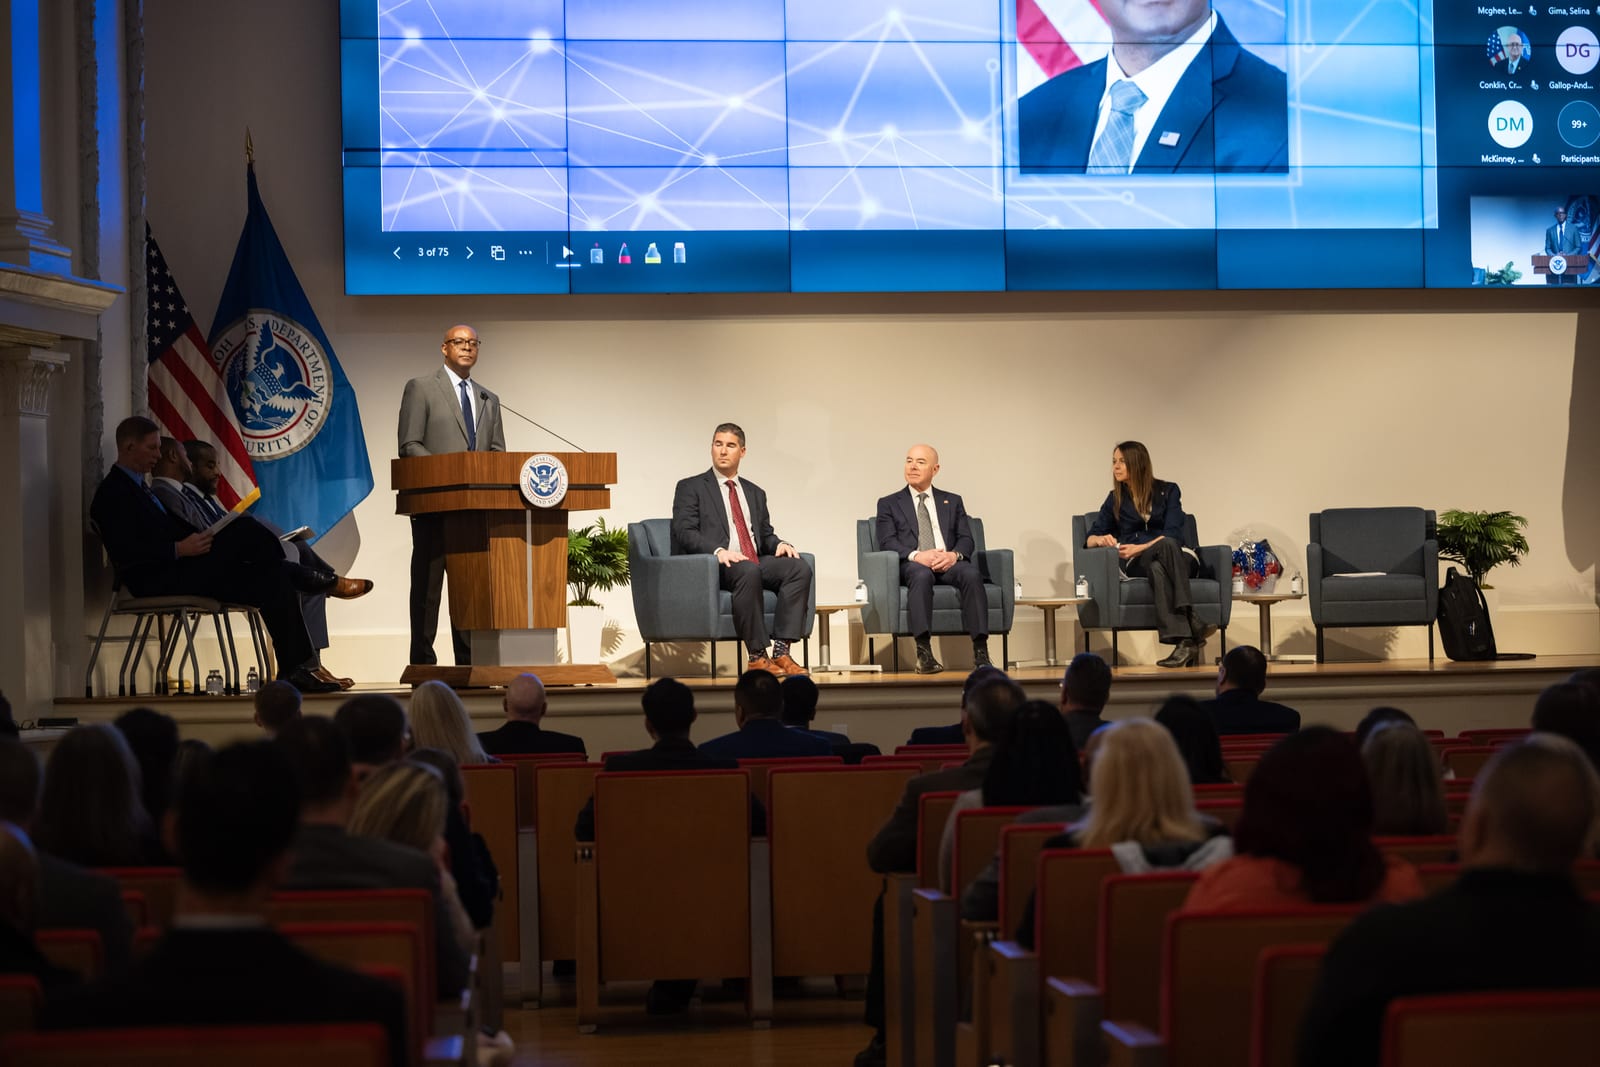
CISA head says agency must change quickly to prevent the 'worst that could happen'
CISA's cybersecurity, infrastructure security and emergency communications divisions are among the priorities as the agency fills vacancies created at the beginning of the Trump administration, acting director Nick Andersen says.
Grindr settles privacy lawsuit tied to disclosure of users’ HIV statuses for $35 million
The settlement concludes a legal fight that dates to April 2024, when UK users sued for the alleged violations of their country’s privacy laws.