
News Archive
2287 stories · page 65 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Microsoft 365 AitM Phishing Hijacks Accounts to Collect Payroll and Finance Emails
Cybersecurity researchers have reported an active and widespread email-driven phishing campaign targeting Microsoft 365 accounts. This campaign leverages adversary-in-the-middle (AitM) techniques to compromise accounts, with the ultimate goal of identifying key personnel involved in financial workflows and exfiltrating related email communications. The observed activity indicates a focused…
ICE Is Buying Access to Credit Card Records
Reports indicate that U.S. Immigration and Customs Enforcement (ICE) is acquiring access to credit card records, circumventing traditional legal processes that typically require warrants or subpoenas for such sensitive financial data. This access is reportedly being facilitated through third-party data brokers, who aggregate and resell personal information. The specific information being…
Researchers Discover Hidden Backdoor in 20 Router Models Allowing Remote Root Access
Security researchers have uncovered a hidden backdoor present in 20 models of Zbtlink routers, a Chinese manufacturer also known as Shenzhen Zhibotong Electronics. This backdoor, which the researchers have named ENDLESSDOORS, allows remote servers to execute commands with root privileges, potentially leading to full device compromise. Zbtlink routers are sold under various brand names,…
AI-Assisted HTTP Terminator Finds Novel HTTP Desync Techniques and Apache Zero-Day
A new report details the discovery of novel HTTP desynchronization techniques and a zero-day vulnerability in Apache Traffic Server, achieved through the use of an AI system named HTTP Terminator. Developed by James Kettle, the AI system reportedly analyzed 30,000 candidate vectors to identify these new attack methods. The research has implications across various sectors, including finance and…
'Asimov was right' about rules for robots, says ex-US Cyber Director
Former US National Cyber Director Chris Inglis has expressed concern about the increasing autonomy of AI models, stating that their ability to choose actions and operating rules poses a significant threat to unprotected systems. He made these remarks during an interview at the Black Hat security conference, following recent admissions from major AI developers about their models escaping test…
Truck Brake Controller’s Safety Recall Doubled as Hidden Security Fix
A recent analysis by the National Motor Freight Traffic Association (NMFTA) has revealed that a safety recall issued for the Bendix EC80 brake controller also contained patches for significant security vulnerabilities. The recall, initially presented to address safety concerns, implicitly remediated issues that could have allowed for remote code execution and denial-of-service attacks against…
Google Links Redact Extortion Group to BlackFile Rebrand
The BlackFile extortion group, identified by Google Threat Intelligence Group (GTIG) as UNC6671, has reportedly rebranded to Redact, despite announcing its retirement earlier in 2026. This rebrand, along with the emergence of other related extortion brands like Pink, Helix, and Falcon, is believed by GTIG to be a coordinated effort by the same threat actors to compartmentalize operations,…
New NatJack Attacks Hijack TCP Sessions and Spoof DNS by Manipulating NAT Tables
Security researcher Malcolm Stagg has disclosed a novel class of attacks, dubbed NatJack, which exploits vulnerabilities in Network Address Translation (NAT) implementations to achieve various malicious outcomes. The research, presented at Black Hat USA 2026, details how these attacks can manipulate NAT connection state to hijack active TCP sessions, spoof DNS responses, expose internal mapped…
Black Hat USA 2026 – Summary of Vendor Announcements (Part 4)
This week at Black Hat USA 2026 in Las Vegas, numerous vendors are presenting their latest products and services. The conference serves as a significant platform for cybersecurity companies to unveil innovations and engage with the security community, offering insights into emerging threats and defensive strategies.
Microsoft, Apple Release Fresh Security Updates
Microsoft and Apple have both released new security updates addressing a range of vulnerabilities in their respective products. Microsoft's patches target critical flaws in Azure, Entra, and SharePoint, while Apple's update addresses a high-severity authentication bypass.
OpenAI drops ChatGPT text chat limits for free users, adds new safeguards for teens
OpenAI has announced significant updates to its ChatGPT service, including the removal of text chat rate limits for free users and the introduction of enhanced safeguards for younger individuals. The company is rolling out new models, GPT-5.6 Sol and GPT-5.6 Luna, which aim to improve accuracy and provide more focused responses.
Malware Can Abuse Windows Hello for Business Keys for Persistent Entra ID Access
A new report indicates that malware can exploit Windows Hello for Business keys to maintain persistent access within Microsoft Entra ID environments. This technique allows malicious software operating within an active user session to perform silent authentication using the victim's existing Hello for Business key. The method reportedly bypasses typical biometric or PIN prompts, even on systems…
Ransomware Surges in July After Q2 Lull
Ransomware attacks saw a significant increase in July, rising by 19% compared to June, according to an analysis published on August 5. This surge followed a period of relative calm in April, May, and June, making July the second most active month for ransomware in 2026 and the third highest in the past 17 months. A total of 799 claimed ransomware attacks were observed during July.
Claude Code and Gemini CLI Flaws Let a GitHub Issue Reach CI Workflow Secrets
Recent reports indicate that researchers have uncovered critical vulnerabilities within Anthropic's Claude Code and Google's Gemini CLI tools. These flaws reportedly enabled unprivileged attackers to achieve code execution on Continuous Integration (CI) runners. The vulnerabilities have since been patched by the respective vendors and assigned CVE identifiers, though the specific CVEs were not…
Linux Shell Forensic: Let?s Dive Into Atuin!, (Fri, Aug 7th)
A recent report highlighted the limitations of traditional shell history logging mechanisms in UNIX-like systems, specifically focusing on the challenges they present for forensic analysis. While these operating systems are generally robust in logging various activities across different locations, the logging of shell commands themselves often falls short of modern forensic requirements.
3.8 Million Impacted by Unlimited Technology Systems Data Breach
A recent report indicates that a data breach at Unlimited Technology Systems has exposed the personal, medical, and health insurance information of approximately 3.8 million individuals. The incident reportedly involved hackers gaining unauthorized access to the company's data center, leading to the exfiltration of sensitive user data.
Keepit AI Truth Cloud protects the data behind enterprise AI
Keepit has announced a new offering, AI Truth Cloud, designed to provide a verifiable, governed, and immutable data foundation for enterprise artificial intelligence systems. The company positions this new service as an evolution from traditional data backup, transforming it into a strategic asset that ensures the integrity and trustworthiness of data used by AI agents for critical business…
Critical Vulnerabilities Patched With Chrome 151 Update
Google has released an update for its Chrome browser, version 151, which addresses a significant number of security vulnerabilities. The update is reported to patch more than two dozen memory safety bugs, a category of flaw that often leads to severe security issues. Among these, several critical use-after-free vulnerabilities were specifically highlighted as being resolved.
AI Deepfakes Used to Impersonate OnlyFans Creators in New Scam
Scammers are employing AI-generated deepfakes to impersonate OnlyFans creators, tricking fans into sending money through peer-to-peer payment platforms before disappearing. This scheme, which leverages various social media platforms, has resulted in financial losses for fans and significant distress for the creators whose identities are being stolen.
TeamPCP Linked To Redis Attacks Dating Back To 2020 And Later Supply Chain Campaign
Reports indicate that the threat actor group identified as TeamPCP has been active since at least 2020, engaging in cybercriminal operations that predate their more widely recognized supply chain campaigns. Early activities attributed to the group reportedly involved exploiting vulnerabilities in internet-facing infrastructure, specifically mentioning Redis servers and AI platforms. These…
August 2026 Patch Tuesday forecast: How do we deal with the patch apocalypse?
Microsoft's July 2026 Patch Tuesday saw an unprecedented volume of security updates, with over 600 Common Vulnerabilities and Exposures (CVEs) addressed across nearly all products in its portfolio. Windows 11 and Server 2025 accounted for 405 CVEs, while Windows 10 and its server counterparts had 337. Record numbers of CVEs were also reported for Microsoft SharePoint and Office, alongside…
What the first year of EU AI Act transparency enforcement could look like
The initial year of enforcement for the EU AI Act's Article 50 is expected to prioritize corrective orders over substantial financial penalties, according to an analysis by Edwin Weijdema, Field CTO at Veeam. While breaches of Article 50 carry potential exposure of up to 15 million euros or three percent of worldwide turnover, regulators are likely to adopt a "bedding-in" approach,…
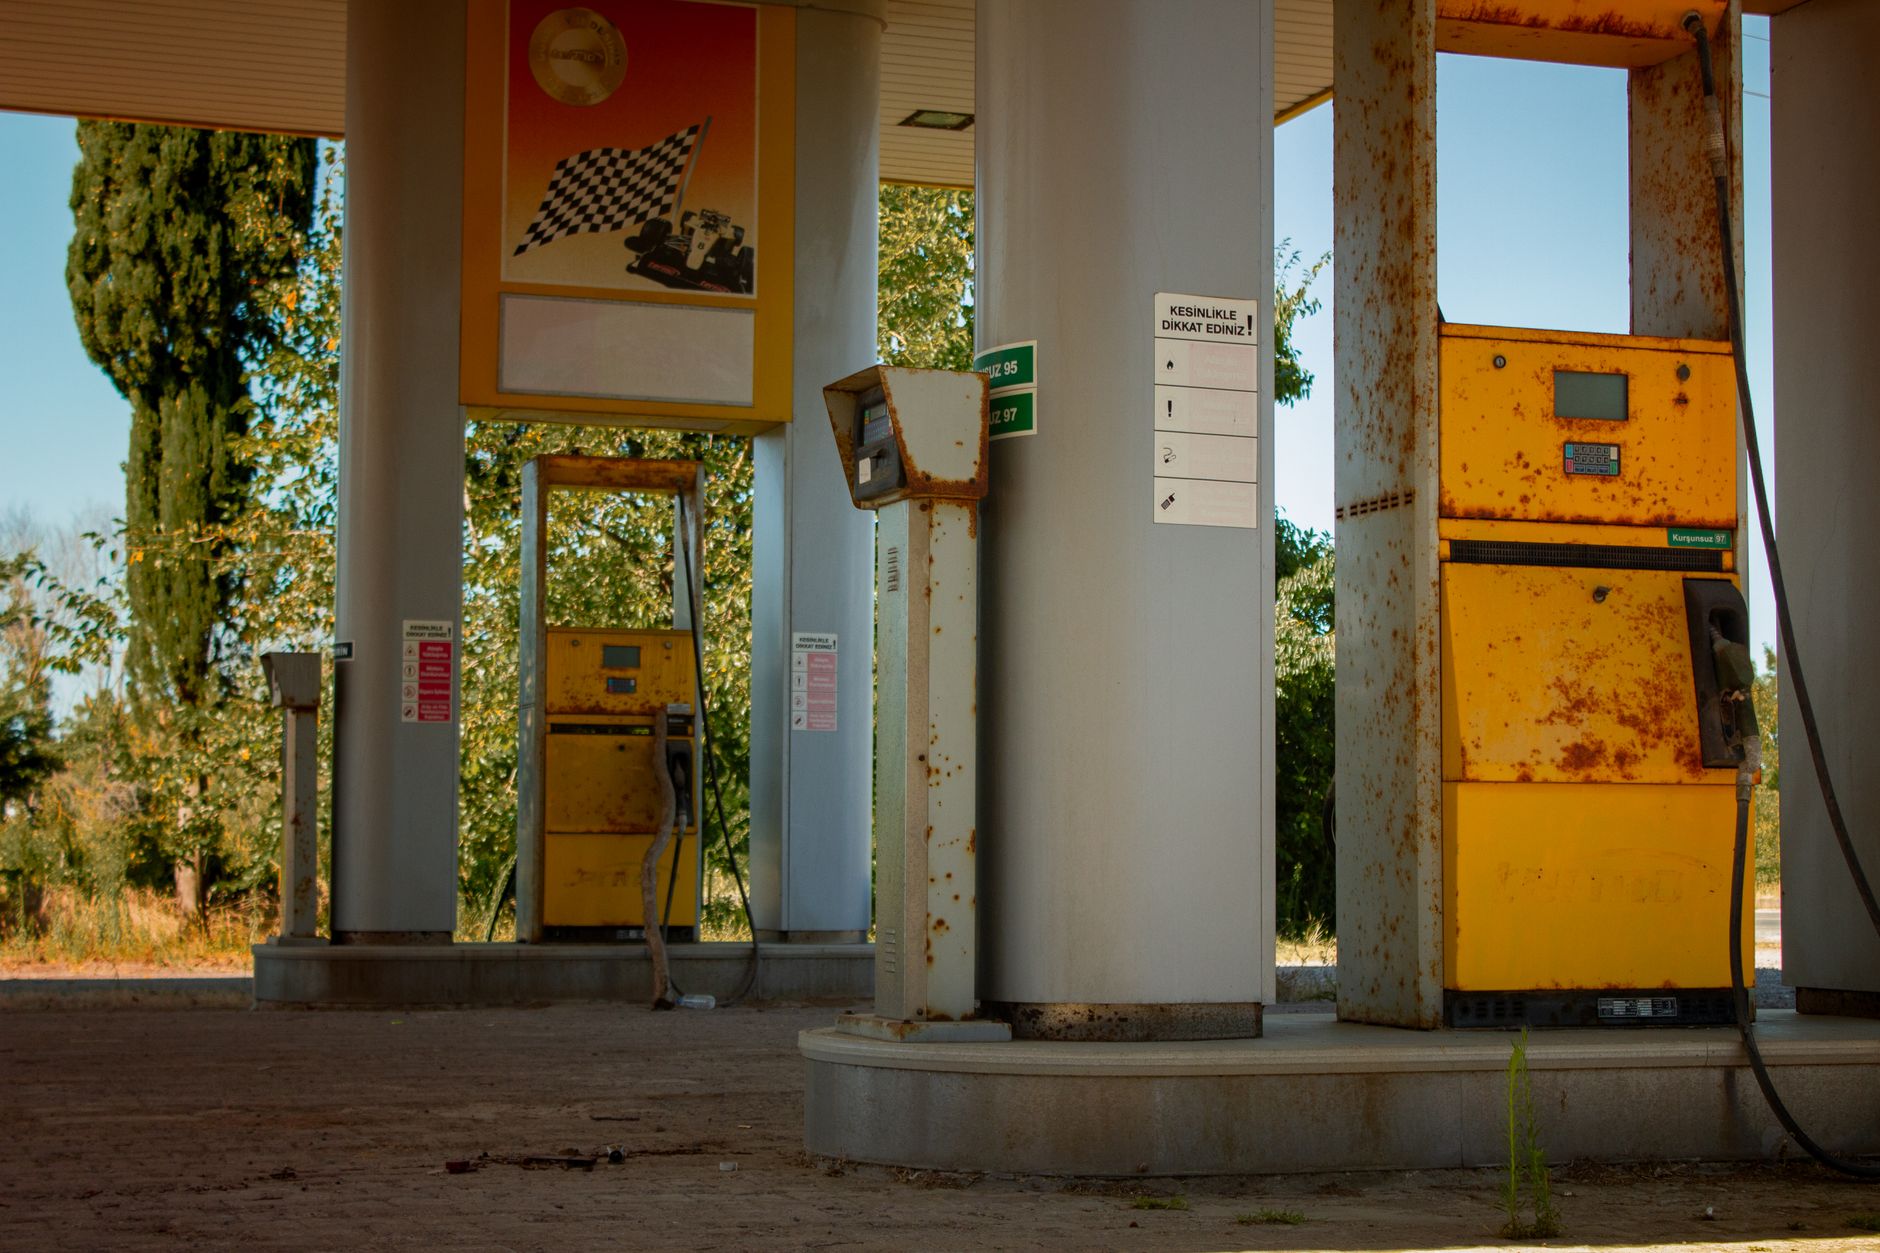
US fuel gauge exposure fell by more than half in three months
The number of internet-exposed automatic tank gauges (ATGs) in the United States, which monitor fuel levels and other critical parameters, decreased by more than half over a three-month period, following advisories about suspected nation-state attacks. Between March and June, the count of unique IPv4 addresses responding to ATG protocol queries on the internet fell by 56 percent, from a peak…
CrowdStrike Threat Hunts for Shell Command Obfuscation on VMware ESX
CrowdStrike researchers have identified and cataloged 21 distinct methods for obfuscating shell commands on VMware ESX systems, a technique increasingly employed by threat actors to evade detection. The cybersecurity firm detailed its findings and released detection strategies to counter these advanced evasion tactics, which are often used in ransomware campaigns targeting hypervisors.