
News Archive
2287 stories · page 92 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
From CI/CD to Cloud Data: How Shai Hulud Persistence Leads to Redshift Breach
A sophisticated supply chain attack, dubbed Shai Hulud, has been observed leveraging poisoned software dependencies to infiltrate CI/CD pipelines and subsequently gain access to sensitive cloud data, including information stored in Amazon Redshift. The campaign, attributed to a group known as TeamPCP, has been active since late 2025, targeting popular package repositories like npm and PyPI.
Thanks for Crushing the Submissions Inbox. We're Trying to Keep Up
The publication is currently facing a significant backlog of submitted content, leading to extended delays in their review and response process. This surge in submissions is a testament to the community's engagement, but it has created an operational challenge for the editorial team.
Small Businesses Need Cyber Readiness for Resilience
Small and medium-sized businesses (SMBs) are increasingly recognizing the critical importance of cybersecurity, with a recent report indicating that 45% of SMBs experienced a cyber incident in the past year. Despite this, 61% express concern about potential attacks in the next 12 months, highlighting a persistent gap between awareness and preparedness. These businesses, which constitute 90% of…
Robinhood Cuts Access Approval Time to Support High-Velocity Development
Robinhood has significantly reduced the time it takes for developers to gain access to necessary systems, a move designed to accelerate its high-velocity development environment. The company's application security team has re-engineered the access approval process, aiming to balance the need for speed with robust security protocols.
In Less Than 24 Hours, Attackers Weaponize Cisco CUCM Flaw
A critical vulnerability in Cisco Unified Communications Manager (CUCM) and CUCM Small and Medium Edition (SME) has been actively exploited by attackers less than a day after its public disclosure. The flaw allows for server-side request forgery (SSRF) and enables attackers to escalate their privileges to root access on affected systems.
Russian APT 'Gamaredon' Upgrades Its Arsenal, Requiring New Defenses
A Russian advanced persistent threat group known as Gamaredon has reportedly updated its toolkit, necessitating new defensive strategies. The group, also referred to as Primitive Bear or Callisto Group, has been active for several years, primarily targeting entities in Ukraine.
Beyond IOCs: AI-enabled threat intelligence
The cybersecurity industry is increasingly exploring the potential of artificial intelligence (AI) to enhance threat intelligence, moving beyond traditional indicators of compromise (IOCs) to derive deeper insights from unstructured data. While AI is often viewed as a double-edged sword, empowering both attackers and defenders, its application in managing and analyzing threat intelligence…
Introduction to COM usage by Windows threats
The Component Object Model (COM), a core Windows technology, is increasingly being leveraged by malicious actors for various stages of cyberattacks, according to recent analysis. While COM is designed for legitimate purposes such as inter-process communication, automation, and code reuse across different programming languages, its inherent capabilities are also attractive to threat actors.…
Gamaredon Group Evolves Tactics With New Tools and Alliances
The Russia-aligned advanced persistent threat (APT) group Gamaredon, also known as UAC-0010, maintained a high operational tempo throughout 2025, primarily targeting governmental and military institutions in Ukraine. The group, which the Security Service of Ukraine (SSU) attributes to the 18th Center of Information Security of Russia's FSB, significantly evolved its tactics, tools, and…
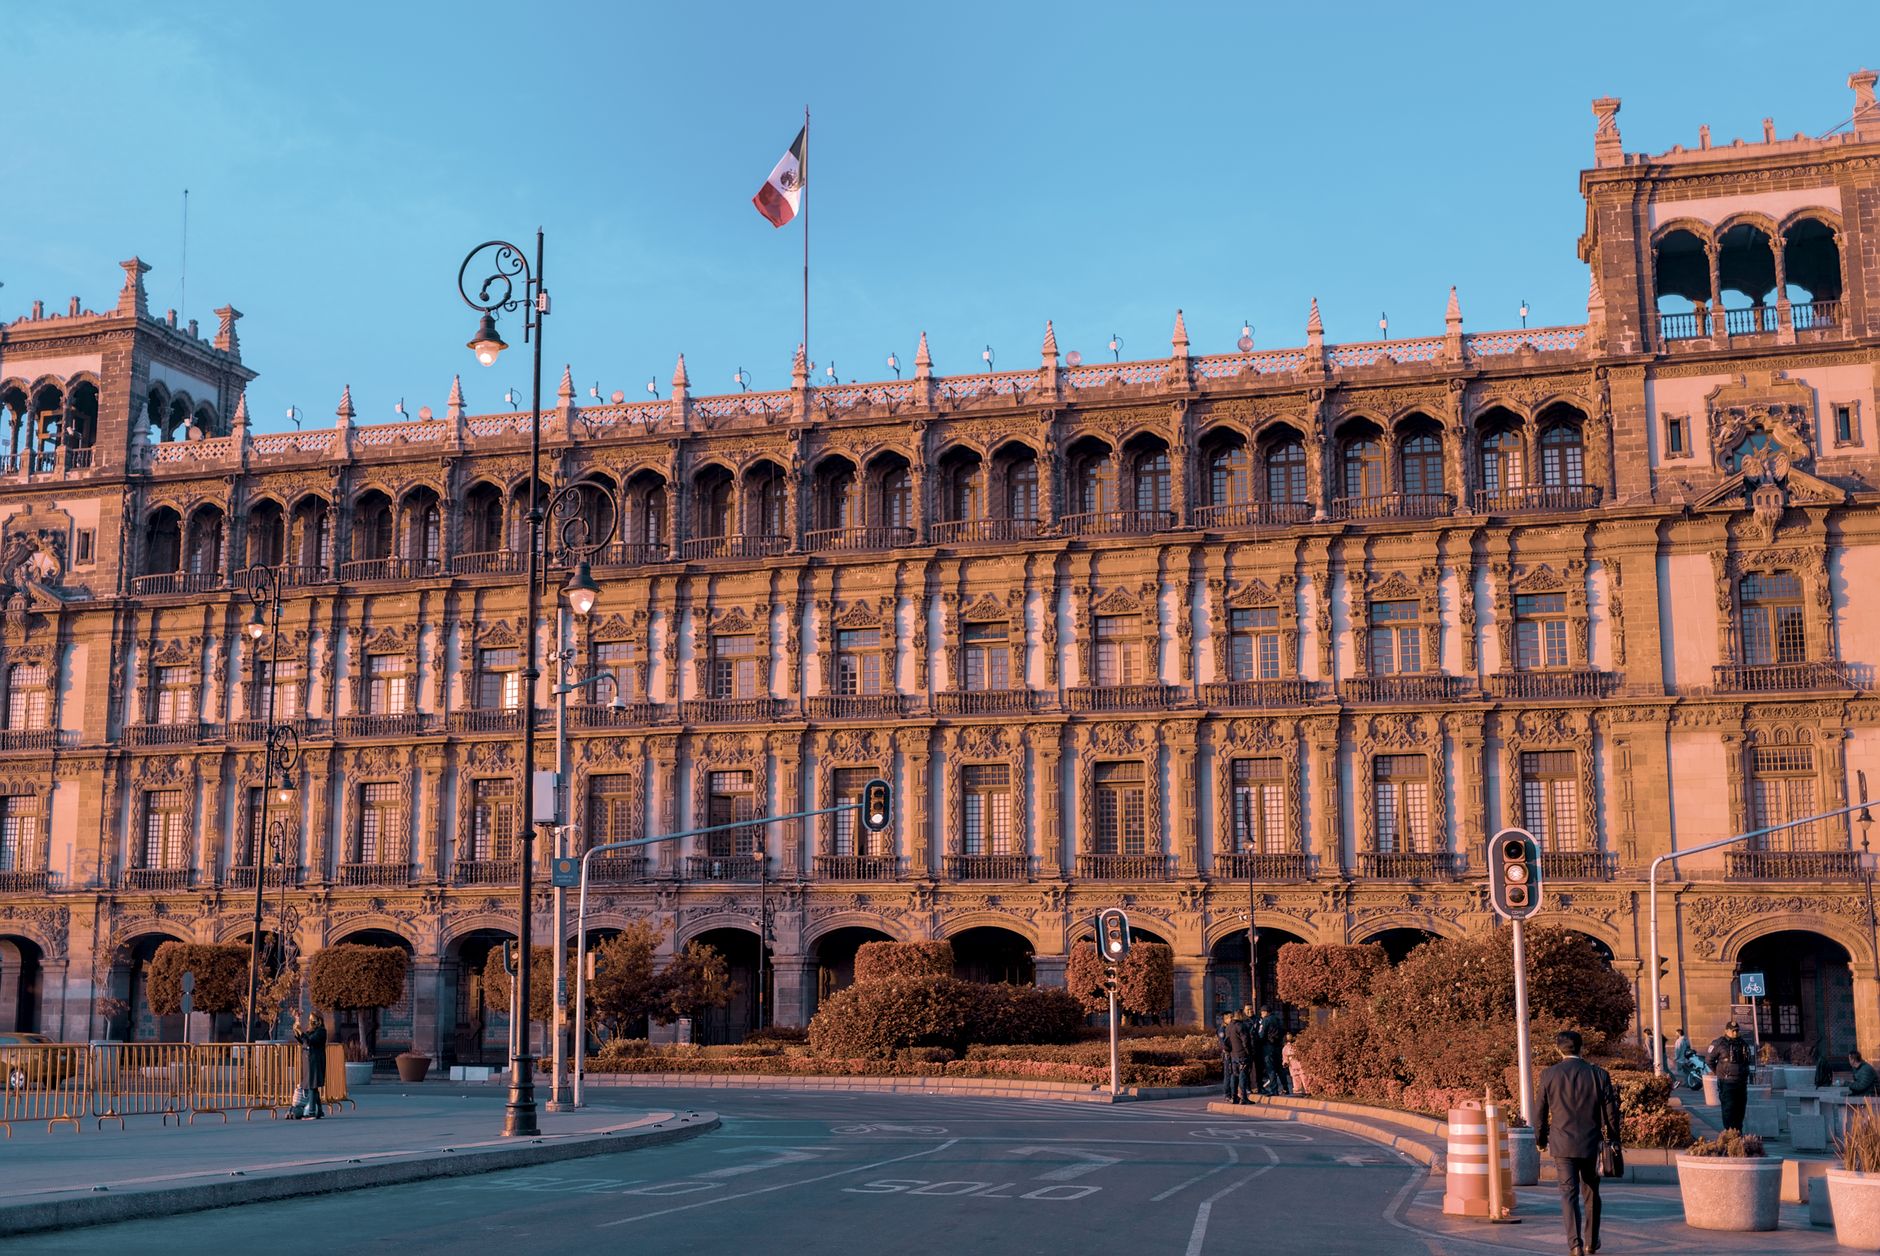
Evaluating Mexico’s New Cybersecurity Plan
Mexico has introduced a new National Cybersecurity Plan designed to address the nation's most pressing cyber threats over the next six years. The plan, published in December 2025, aims to bolster Mexico's digital defenses against organized crime, geopolitical adversaries, and emerging artificial intelligence threats, a move prompted by a series of significant cyber incidents affecting federal,…
Where Expertise Meets Algorithm: The Insikt Group® Intelligence Edge
Recorded Future's Insikt Group research team combines human expertise with automated analysis to produce actionable threat intelligence. The team comprises individuals with backgrounds in government, military, law enforcement, and intelligence agencies, bringing decades of experience to their work. This approach, described as a "centaur model," leverages seasoned human judgment alongside…
Smashing Security podcast #473: How a hacker could have Rickrolled the entire World Cup
A security researcher gained access to the live broadcast controls for all matches of the 2026 FIFA World Cup, potentially allowing them to disrupt the global event with any content they chose. The researcher, identified as Bob DaHacker, reportedly spent days attempting to contact FIFA officials about the vulnerability but struggled to reach anyone.
AI Creates 457 Million Security Issues for Organizations
A recent analysis by Tenable identified 457 million AI-related security issues across more than 7,000 organizations over a 30-day period, averaging 62,000 exposures per organization. These issues are primarily linked to misconfigurations and unmanaged dependencies within AI tools, rather than traditional Common Vulnerabilities and Exposures (CVEs). The findings highlight a significant…
CERT-In’s AI Vulnerability Blueprint: Why Indian CISOs Need Machine-Speed Risk Operations in the Post-Mythos Era
India's cybersecurity agency, CERT-In, has issued a new blueprint that significantly raises the bar for vulnerability remediation, demanding a shift from human-speed to machine-speed risk operations. This directive, released on May 25, 2026, mandates the containment of known exploited vulnerabilities on internet-facing and critical systems within 12 hours. This requirement stands in stark…
Weekly Update 509
A newly identified vulnerability in certain versions of the Realtek SDK could potentially allow attackers to execute arbitrary code on affected devices. The vulnerability, identified as CVE-2023-32250, was discovered by security researchers at GRIMM.
ZDI-26-397: X.Org Server CreateSaverWindow Use-After-Free Information Disclosure Vulnerability
A critical use-after-free vulnerability has been identified in the X.Org Server, potentially leading to sensitive information disclosure and privilege escalation. The vulnerability, tracked as ZDI-26-397, resides in the server's management of ScreenSaverScreenPrivateRec objects. It arises from an insufficient validation process, where the server performs operations on an object without first…
FortiBleed Campaign Exposing Credentials for 73,932 FortiGate Systems
A campaign dubbed "FortiBleed" has exposed administrative and VPN credentials for an estimated 73,932 FortiGate firewall systems globally. The compromised data, reportedly originating from a Russian-speaking threat group, has impacted organizations across critical sectors including government, telecommunications, financial services, healthcare, manufacturing, and multinational corporations.
OpenClaw Skill Marketplace Faces AI Supply Chain Threat
OpenClaw, a platform for AI agents that execute third-party skills from its dedicated marketplace, ClawHub, has been targeted by persistent and evolving malicious campaigns. These attacks leverage the unique architecture of AI agent ecosystems, where skills, defined by markdown-driven packages, possess broad access to local systems, making ClawHub a critical vulnerability in the agentic…
macOS Backdoor Uses Fake Messages to Evade AI Analysis
A newly identified macOS backdoor, tracked as macOS.Gaslight, employs a sophisticated technique to evade security analysis by embedding fabricated system messages designed to mislead AI-powered security tools. Researchers have assessed with high confidence that this implant is linked to North Korean state-aligned threat activity.
Scattered Spider Hackers Plead Guilty on Day 1 of Trial
Two individuals identified as key members of the cybercrime group Scattered Spider have pleaded guilty to criminal charges in the United Kingdom. The pleas occurred on the first day of a trial that had been expected to last six weeks. The charges stem from a cyberattack in August 2024 that significantly disrupted Transport for London, the agency managing the public transit system for Greater…
Miasma Worm Exploits Developer Credentials in Supply Chain Attacks
A sophisticated supply chain attack campaign, dubbed Miasma, has targeted multiple organizations by exploiting stolen developer credentials, leading to the compromise of numerous software packages. The campaign, which began on June 1, affected packages within Red Hat, Vapi.ai, and Microsoft Azure repositories. Researchers observed that the malicious packages generated by Miasma included valid…
Fake shops target shoppers across Europe with fake Samsung deals, counterfeit goods and World Cup scams
A recent investigation by Bitdefender Labs has uncovered a significant escalation in fake online shop campaigns targeting consumers across 12 European countries between March and May 2026. These operations, far from being isolated incidents, are now functioning as coordinated, multinational businesses employing professional e-commerce tactics.
Hacker hijacks Brazil’s national alert system, sending “misanthropy” to millions of phones
Millions of mobile phone users in Brazil received fake emergency alerts on the night of June 19-20, 2026, after an intruder gained access to the nation's Civil Defence alert system. The unauthorized messages, which bypassed silent mode and displayed prominently on device screens, contained the word "misantropi4" in place of critical information.
The Purchase Scam Tactic Headed for the World Cup | Recorded Future
A sophisticated purchase scam tactic, leveraging compromised legitimate websites to trick shoppers through organic search results, is being actively deployed and is expected to scale significantly around major events like the upcoming World Cup. This method allows scammers to bypass traditional advertising monitoring and avoid the costs associated with search engine optimization for their own…