
News Archive
2287 stories · page 94 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Microsoft Patch Tuesday for June 2026 — Snort rules and prominent vulnerabilities
Microsoft has released its June 2026 security update, addressing a total of 206 vulnerabilities across its product range, with 32 of these classified as "critical." The update includes fixes for numerous remote code execution (RCE) and elevation of privilege vulnerabilities affecting core Windows components, as well as products like Microsoft Office, SQL Server, and Azure Kubernetes Service.
Got a LinkedIn message from a recruiter? It might be Chinese intelligence, warn FBI and MI5
Intelligence agencies from five allied nations are warning professionals to be wary of unsolicited messages on platforms like LinkedIn, as Chinese military intelligence is reportedly using these channels to recruit individuals for information gathering. The FBI, MI5, and their counterparts in Australia, Canada, and New Zealand have issued a joint advisory detailing a sophisticated operation…
Meta’s own AI chatbot to blame for Instagram accounts being stolen in seconds
Cybercriminals are reportedly exploiting a vulnerability in Meta's AI-powered support chatbot to gain unauthorized access to Instagram accounts. The method, which requires no specialized technical expertise, allows attackers to hijack accounts rapidly and at scale.
Reporting from Vegas: Networking, AI, and good boys
The cybersecurity landscape is increasingly focused on the challenges and opportunities presented by artificial intelligence, particularly concerning data management and security infrastructure. Discussions at recent industry events highlight the significant hurdles businesses face in handling the vast amounts of data required for AI operations, especially in an agentic environment.
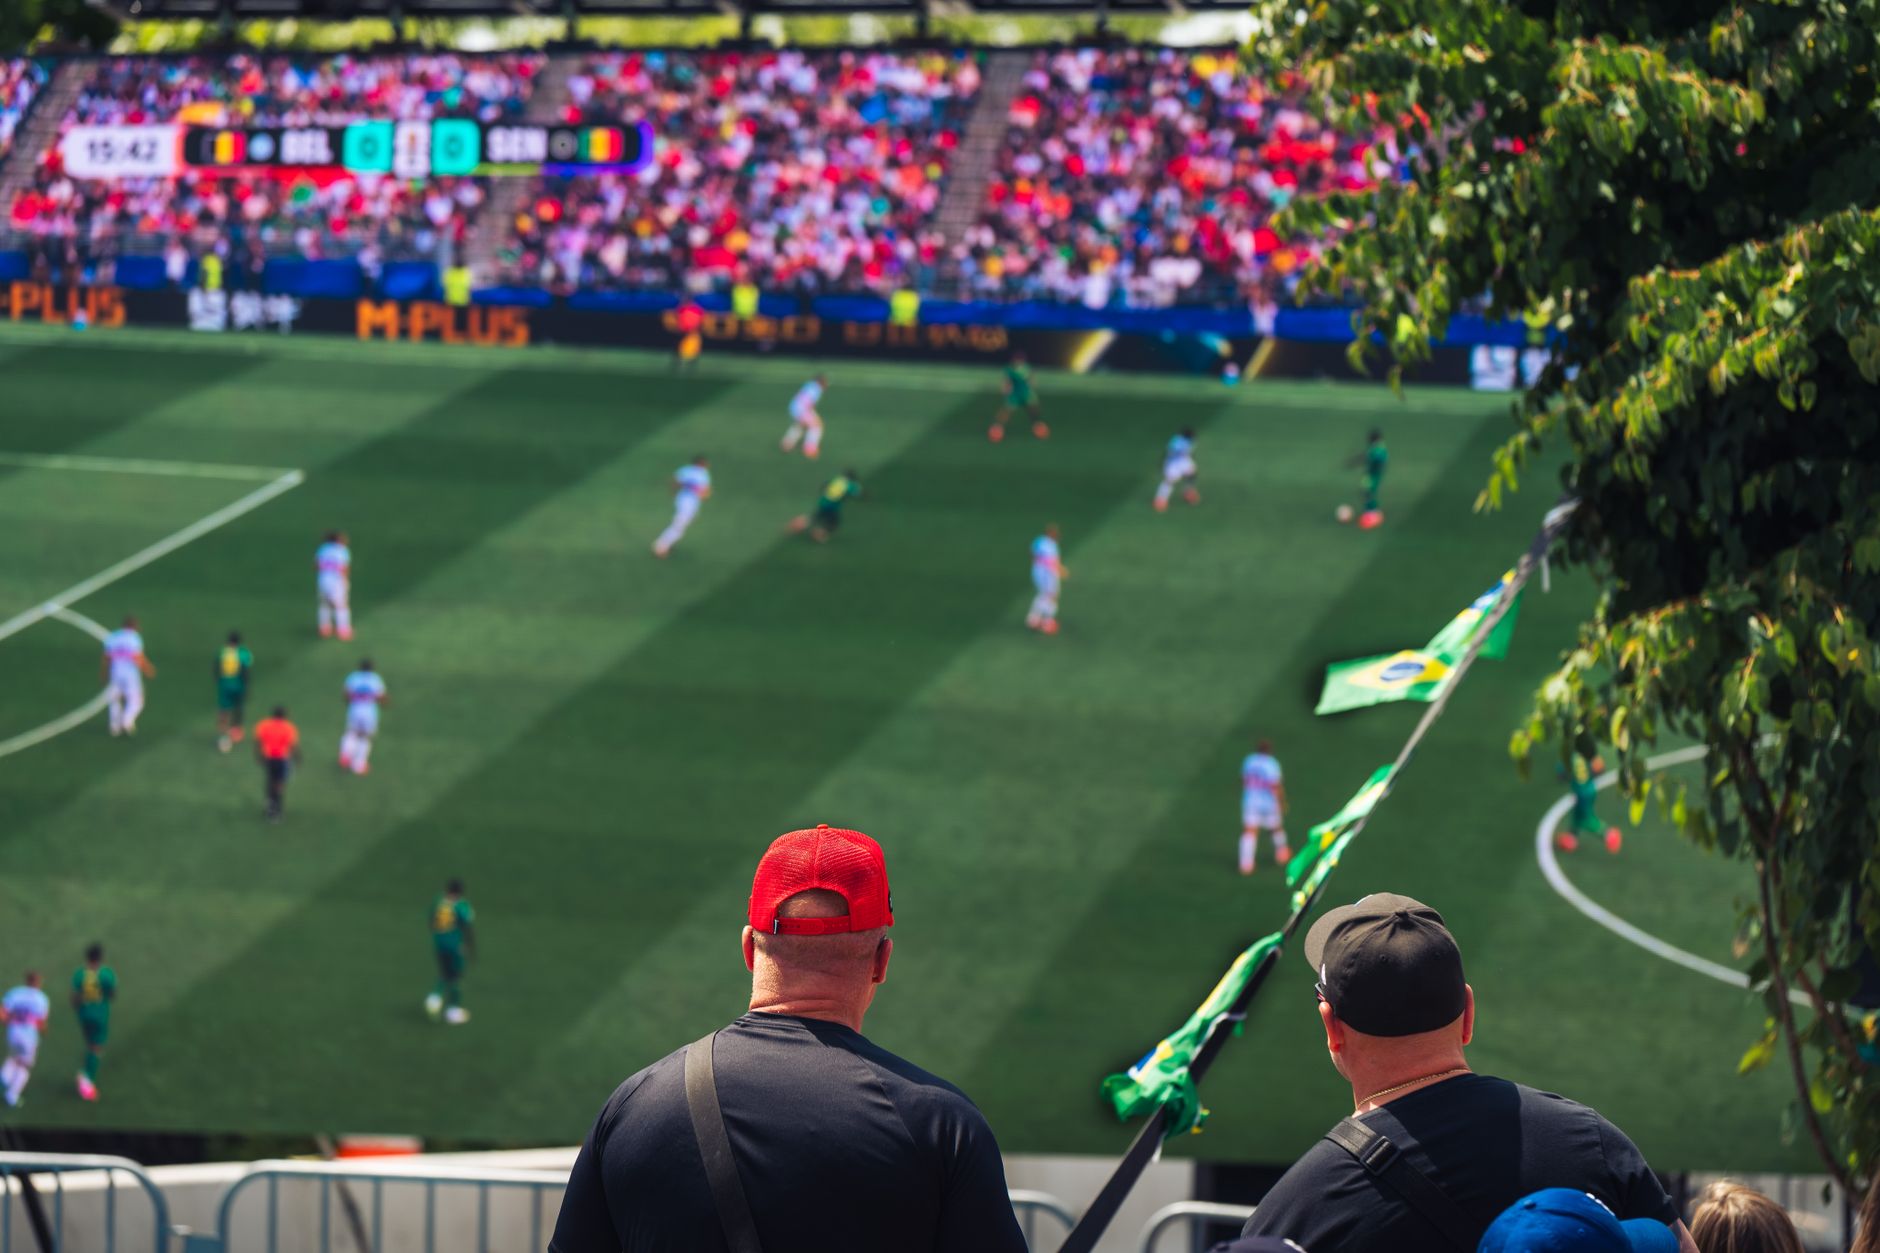
Cybercriminals Are Targeting the FIFA World Cup 2026
Cybercriminals are actively targeting the upcoming FIFA World Cup 2026, establishing infrastructure and launching various scams to exploit the event's global appeal, according to research from FortiGuard Labs. The tournament, set to begin on June 11, 2026, is expected to attract significant attention and drive a high volume of digital transactions, creating a fertile ground for malicious actors.
Winning the cyber marathon with Tony Giandomenico
Tony Giandomenico, Senior Director of Product Management at Cisco Talos, has observed a significant acceleration in the capabilities of advanced AI models, which he believes will fundamentally alter the cybersecurity landscape. This rapid evolution, he notes, is prompting a reevaluation of how both defenders and adversaries will leverage these technologies.
Hypotheses, telemetry, and human judgment: Inside Cisco Talos Threat Hunting
Cisco Talos Threat Hunting employs a proactive approach, starting with hypotheses about adversary behavior rather than waiting for known malicious patterns to trigger alerts. This method aims to detect threats that evade traditional, signature-based security tools by actively searching for specific indicators within telemetry data. The process combines artificial intelligence with human…
Smashing Security podcast #470: This AI security flaw might be impossible to fix
A website that purported to assist travelers with UK visa applications has been found to have collected sensitive personal data, including passport scans and selfies, from thousands of users. The data was reportedly stored in an unsecured Amazon storage bucket, making it accessible to unauthorized individuals. When a journalist attempted to alert the company operating the website, they were…
Inside the Cross-Platform Propagation of a New Gafgyt Variant C0XMO
FortiGuard Labs has identified a new variant of the Gafgyt botnet, dubbed C0XMO, which exhibits cross-platform propagation capabilities by exploiting a vulnerability in DD-WRT router firmware. The malware, discovered in March, utilizes CVE-2021-27137 to gain initial access. A notable characteristic of C0XMO is its separation of lateral movement functions into a distinct Python script, allowing…
Welcoming the Philippine Government to Have I Been Pwned
The Philippines government has joined Have I Been Pwned's free service for government organizations, gaining access to tools that can help monitor data breaches. This marks the 46th government entity to utilize the platform's resources.
Gamaredon Facilitated Turla's Access to Ukrainian Targets
ESET researchers have uncovered evidence of collaboration between the Gamaredon and Turla espionage groups, with Gamaredon actively enabling Turla's access to Ukrainian targets. Between February and June 2025, Gamaredon's tools were used to deploy Turla's Kazuar backdoor and restore access. This partnership highlights a division of labor where one group establishes access and the other deploys advanced espionage tools.
From API key to live threat detections in minutes: how Elastic Security ingests Google Threat Intelligence
Elastic Security now offers native integration with Google Threat Intelligence (GTI), allowing security teams to ingest known malicious indicators and leverage AI-driven workflows for real-time alert enrichment and investigation. This integration aims to streamline the process from initial setup to live threat detection within minutes.
Malvertising Scams Proliferate Across APAC Via Social Media Ads
Bitdefender Labs has identified a widespread malvertising network operating across 13 countries in the Asia-Pacific (APAC) region, distributing over 12,000 scam campaigns through paid advertisements on Meta platforms. Between January and April 2026, researchers Alexandra Svetlana Dinulica and Vlad Mihai Sireanu observed more than 400,000 ad sightings associated with these campaigns.
Hackers Used Meta’s AI Support Bot to Seize Instagram Accounts
Instagram accounts, including those belonging to the Obama White House and the Chief Master Sergeant of the U.S. Space Force, were temporarily defaced with pro-Iranian content following the discovery of a method to exploit Meta's AI support bot for account takeovers. Instructions detailing this exploit began circulating on Telegram, demonstrating how to manipulate the AI assistant into…
1,000 Data Breaches Later, the Disclosure Lag is Worse Than Ever
The 1,000th data breach has been added to the Have I Been Pwned (HIBP) service, a milestone that prompts reflection on the persistent need for such tools. The ongoing accumulation of data breaches suggests that the time lag between a breach occurring and its public disclosure may be worsening.
Weekly Update 506
A recent wave of data breaches attributed to the threat actor group ShinyHunters has brought renewed attention to the challenges organizations face in responding to and disclosing such incidents. While the criminal nature of these attacks is evident, the varying degrees of organizational response, including instances of non-disclosure, highlight ongoing issues in cybersecurity incident…
Police arrest man following hack of Ajax football club
Dutch police have arrested a 35-year-old man in connection with a significant data breach at the Ajax football club. The suspect is accused of repeatedly gaining unauthorized access to the club's IT systems, potentially compromising the personal information of hundreds of thousands of supporters.
Less panic patching, more precision
Security teams are being urged to re-evaluate their vulnerability management strategies to better prepare for an anticipated surge in patching requirements. The current default practice of prioritizing vulnerabilities based solely on the Common Vulnerability Scoring System (CVSS) is insufficient, as CVSS measures theoretical severity rather than actual risk.
MyPillow listed on ransomware gang’s leak site, but denies it has been breached
The ransomware group known as Play is claiming to have exfiltrated data from the US-based pillow manufacturer MyPillow. The group posted on its dark web leak site that it had obtained private and personal confidential information. Play threatened to release an unspecified amount of this data on Friday, potentially exposing documents related to clients, budgets, payroll, identification, taxes,…
DICOM, Pydicom, GDCM, and Orthanc: A technical tour of what really happens in the heap
Researchers have detailed a heap overflow vulnerability affecting systems that process DICOM (Digital Imaging and Communications in Medicine) files, a standard widely used in medical imaging. The vulnerability can be triggered during the image upload process, potentially leading to an out-of-bounds write on an Orthanc server, a popular open-source PACS (Picture Archiving and Communication…
Football Fever Fuels Scam Campaigns Across Email and Social Media
Football fans are increasingly becoming targets of sophisticated scam operations that leverage the excitement surrounding major tournaments and club loyalties, according to recent findings from Bitdefender Labs. Investigations have uncovered over 55 distinct scam campaigns exploiting various aspects of football fandom, including merchandise, streaming services, collectibles, and giveaways.…
Phishing Campaign Deploys JavaScript-Driven PureLogs Variant to Steal Sensitive Data
A recent phishing campaign is distributing a variant of the PureLogs malware, designed to steal sensitive data from compromised Windows systems. The campaign employs a multi-stage attack chain involving obfuscated JavaScript, PowerShell, and process hollowing techniques.
Welcoming the Bhutanese Government to Have I Been Pwned
The government of Bhutan has joined Have I Been Pwned's (HIBP) free service for government entities, the 45th such organization to do so. The Bhutan Computer Incident Response Team (BtCIRT) will now utilize HIBP's capabilities to monitor Bhutanese government domains for potential data breaches.
Netherlands Seizes 800 Servers, Arrests 2 for Aiding Cyberattacks
Authorities in the Netherlands have arrested two individuals suspected of facilitating Russian cyberattacks and disinformation campaigns by providing essential IT infrastructure. The arrests, which occurred on May 18, are linked to the operations of hosting companies that allegedly supported entities sanctioned by the European Union for engaging in malicious cyber activities.