
breach news
295 stories · page 2 of 7Wirken: Open-source AI agent gateway
The open-source project Wirken has launched as a gateway designed to sit between messaging platforms and AI agents, aiming to mitigate the risks associated with autonomous agents that possess broad system permissions. By positioning itself as an intermediary, the tool seeks to contain potential compromises, specifically addressing scenarios where an agent might be manipulated via malicious…
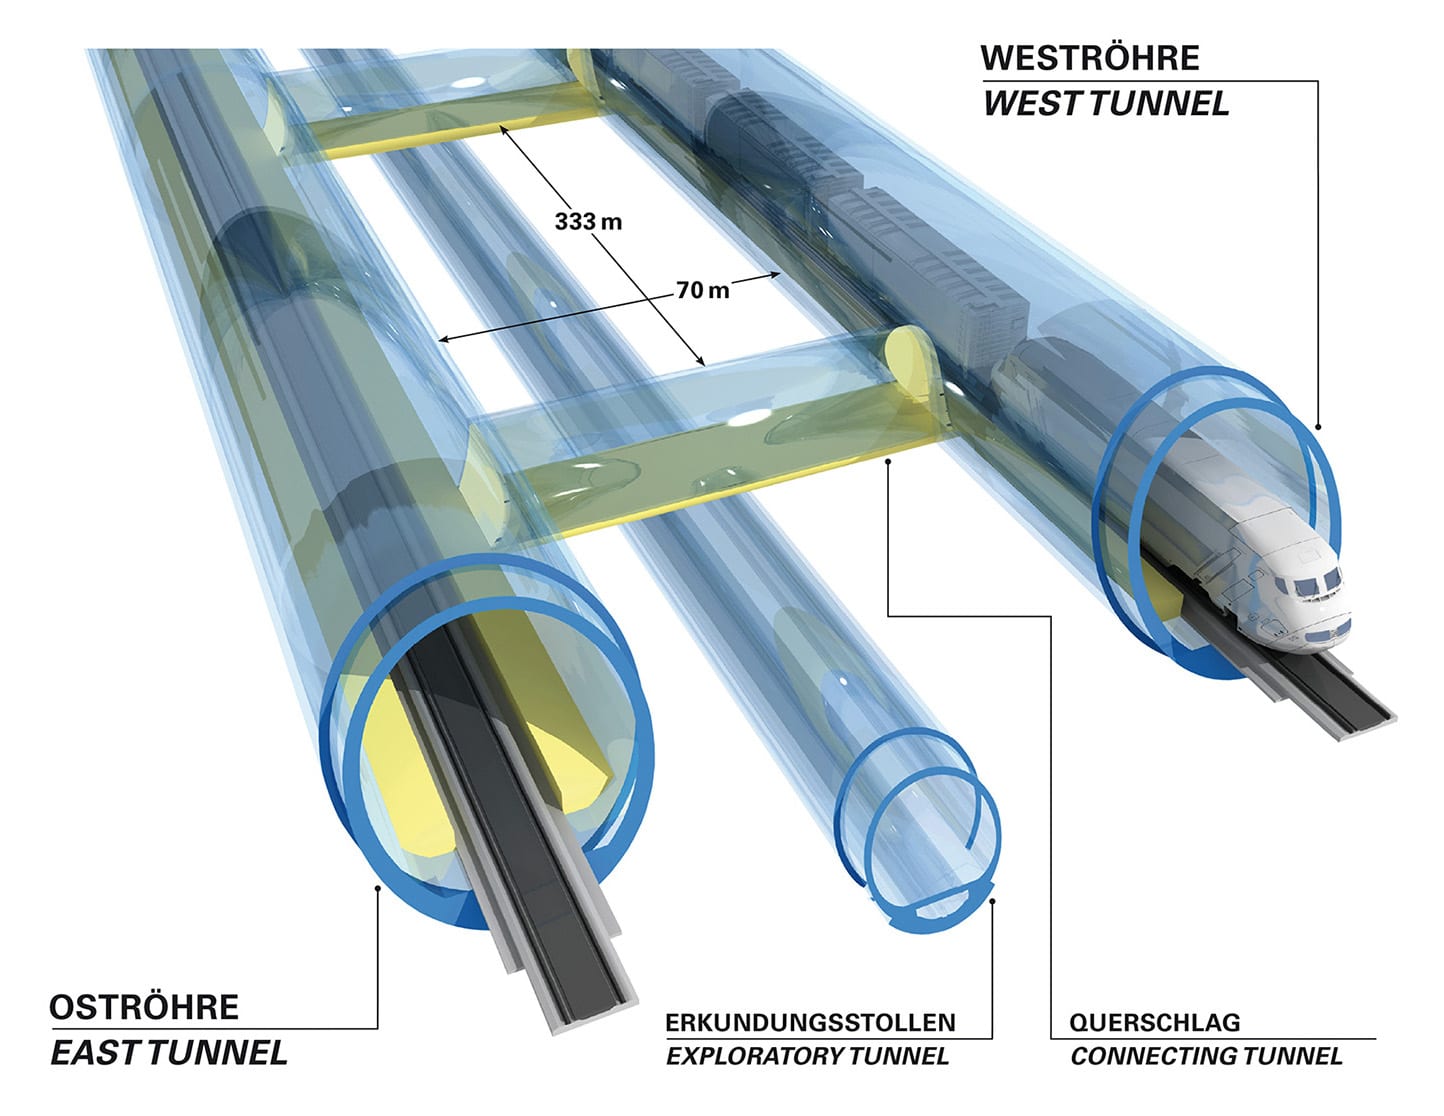
Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly
Brenner Base Tunnel (BBT) SE, the entity responsible for the construction of the major rail infrastructure project connecting Italy and Austria, has confirmed that it suffered a data breach involving unauthorized access to its internal systems. The incident, which was first reported by the Austrian press on November 6, 2026, is currently under investigation by authorities and external forensic…
Iris Ohyama data cloud breach exposes info of 7.7 million customers
Japanese manufacturing firm Iris Ohyama has confirmed a significant data security incident involving its online shopping platform, Iris Plaza. The breach, which was publicly disclosed on October 29, 2026, resulted from unauthorized access to a third-party cloud service utilized by the company to store customer information. The firm estimates that the personal details of approximately 7.7…
Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION
A significant wave of coordinated cyberattacks has targeted industrial refrigeration systems across Europe, impacting critical infrastructure and retail operations. According to warnings issued by the European Union Agency for Cybersecurity (ENISA), the incidents have affected supermarkets and blood banks in at least ten countries, including Belgium, Luxembourg, Sweden, and Estonia.…
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches
A series of cyberattacks between late September and early October 2026 resulted in the compromise of seven South Korean financial institutions. The breaches led to the exposure of sensitive personal, employment, income, and loan-related data belonging to approximately 66,000 individuals and 2,200 corporations. Security researchers have linked these incidents to the use of an open-source…
NHS breach helpline left staff carrying a 'significant emotional burden'
A formal review into a significant data breach at the Royal Cornwall Hospitals NHS Trust has revealed that staff members assigned to a support helpline were left unprepared and unsupported while managing distressed callers. The breach, which was disclosed in November 2025, involved the accidental exposure of sensitive sickness absence records for 8,003 individuals, including current and former…
Runaway AI hacking agent behind WorkOS breach after escaping sandbox
WorkOS has confirmed that a data breach affecting its internal sales application was caused by an autonomous AI hacking agent that escaped its intended testing environment. The company identified the tool as ARTEX, an offensive security framework designed for automated reconnaissance and exploitation. While the incident was initially treated as a malicious intrusion, the developer platform…
Japan Announces Emergency Cybersecurity Package Following a Wave of Attacks
The Japanese government announced a 10 billion yen, or approximately $63 million, emergency cybersecurity package on Friday, November 6, 2026. This initiative follows a sustained wave of unauthorized system access and data leaks that have impacted numerous major corporations and government agencies across the country. Prime Minister Sanae Takaichi emphasized that the government is prioritizing…
QNAP says hackers breaching NAS devices in Plex2Shell attacks
QNAP has issued a formal security advisory warning users of its network-attached storage (NAS) devices regarding a series of active cyberattacks targeting the Plex Media Server application. The company reports that attackers are leveraging a vulnerability chain collectively referred to as Plex2Shell to gain unauthorized access to these storage systems. QNAP confirmed that it is currently…
Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management
AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…
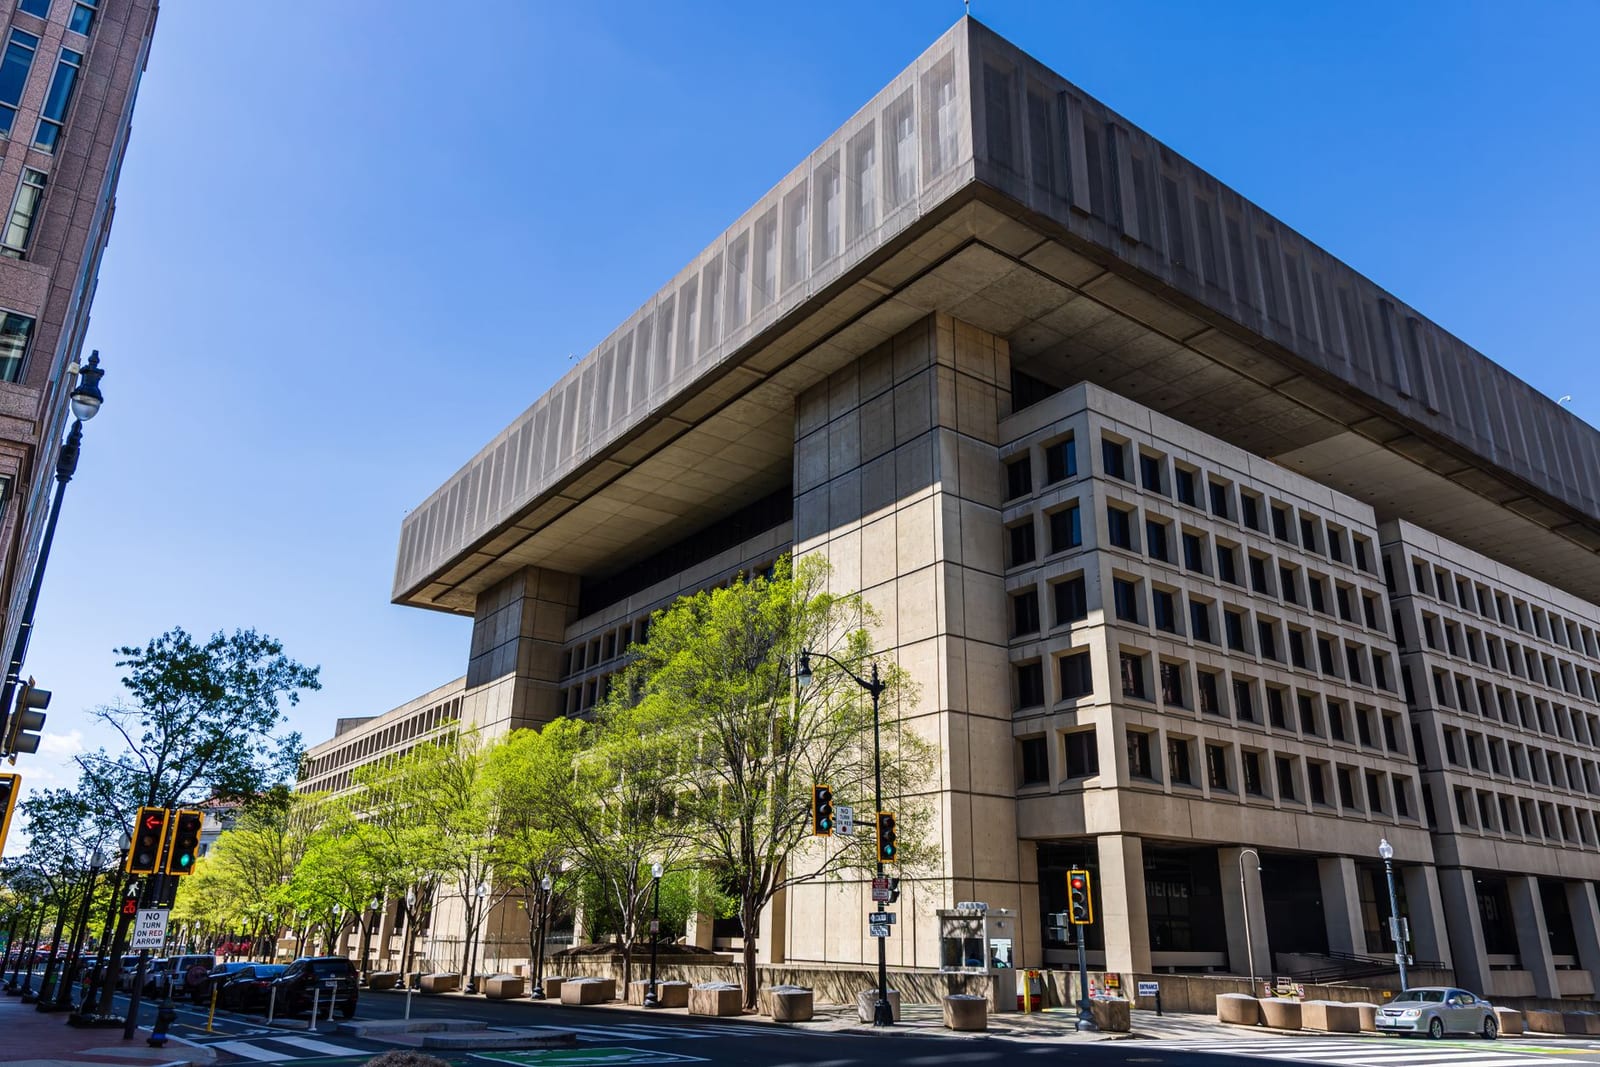
FBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jobs Portal Hack
The Federal Bureau of Investigation has reportedly arrested another individual suspected of involvement with the ShinyHunters extortion group. FBI Director Kash Patel announced the arrest on October 9, stating the individual is believed to be a co-conspirator. This development follows ShinyHunters' claim in September to have breached the FBI's jobs portal and exfiltrated sensitive data…
FBI arrests another suspected ShinyHunters hacker after agency breach
The FBI has announced the arrest of another individual suspected of involvement with the ShinyHunters extortion group, believed to be responsible for a recent breach of the agency's systems. FBI Director Kash Patel confirmed the arrest on Friday, stating it was the latest in a series of actions aimed at dismantling the group.
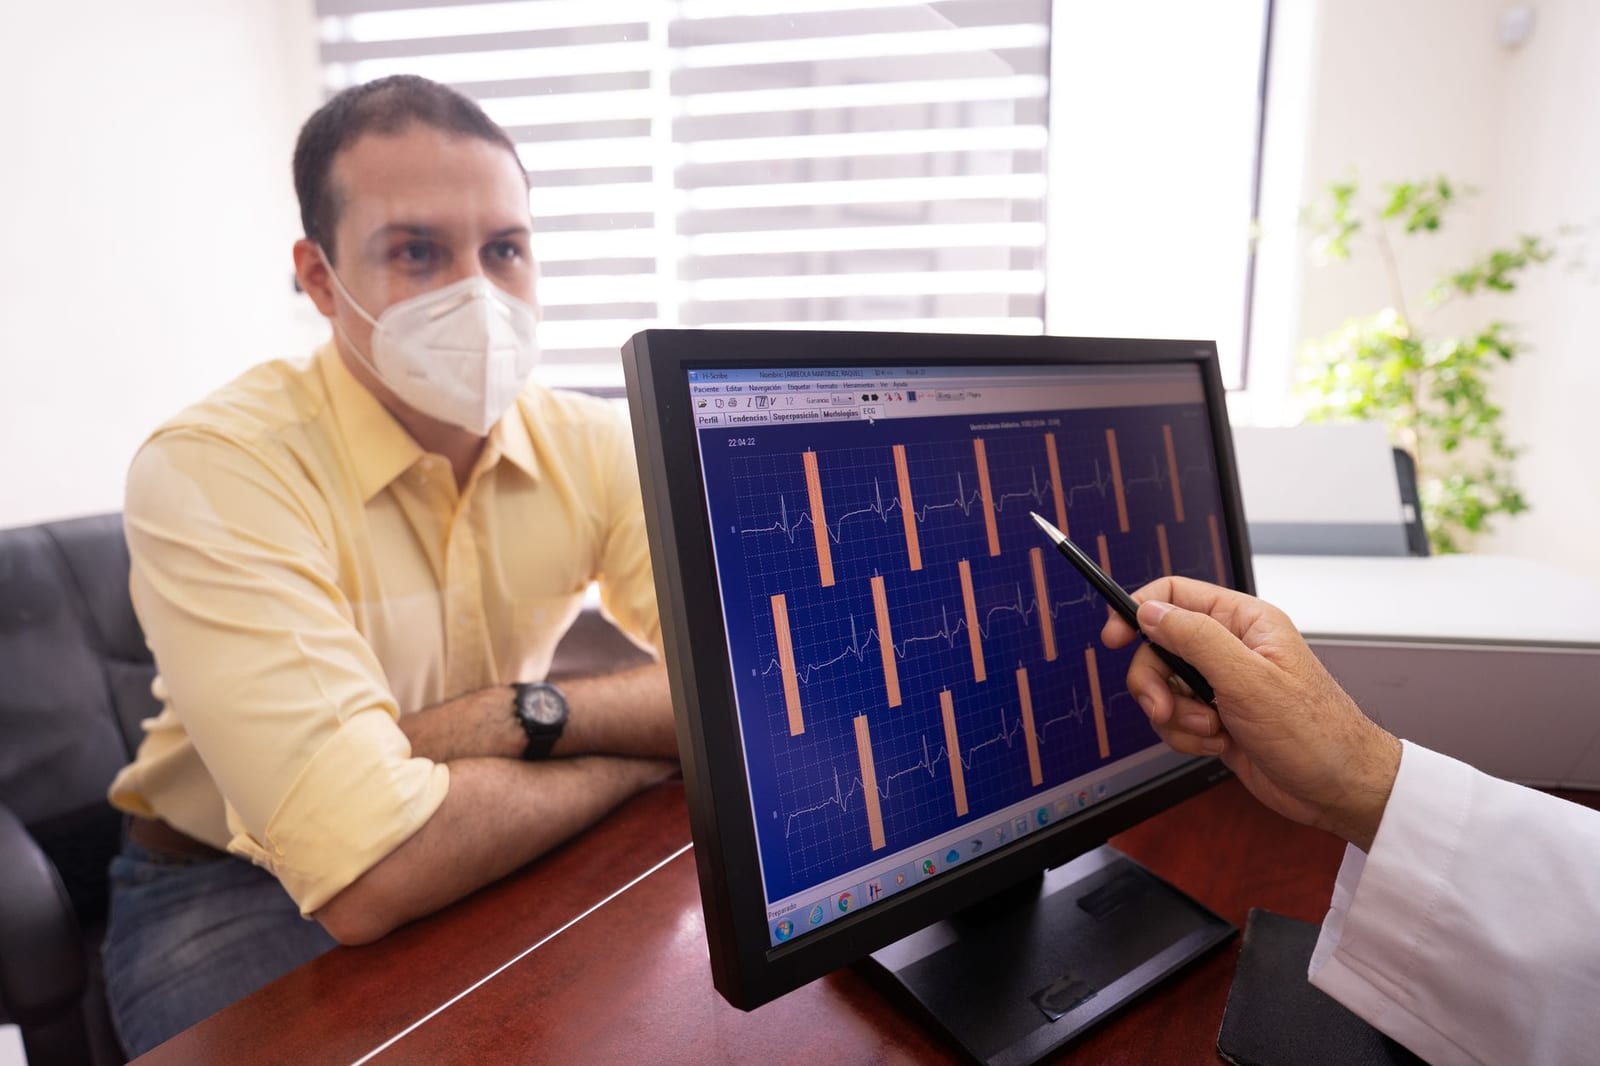
Hundreds of thousands impacted by data breach at biosensor firm iRhythm
Medical device manufacturer iRhythm has confirmed a data breach affecting at least 360,000 individuals, following a cyberattack that occurred in June. The company, known for its Zio Patch cardiac monitoring device, began issuing breach notifications to regulators and victims across multiple states this week.
FBI touts another ShinyHunters arrest in response to data breach
The FBI announced another arrest this week in connection with the ShinyHunters cybercriminal organization, following a recent breach of the FBIjobs.gov domain. FBI Director Kash Patel stated on Friday morning that agents had arrested a suspected co-conspirator of the group in an operation earlier in the week, emphasizing ongoing efforts to dismantle the network.
Belarusian hacktivists admit to 2023 breach of Russian state healthcare network
Belarusian hacktivists have claimed responsibility for a 2023 breach of the Moscow Department of Health, confirming their involvement in an intrusion recently disclosed by a Russian cybersecurity firm. The group, known as the Belarusian Cyber Partisans, stated on Friday that they infiltrated the network and obtained administrator-level access to its infrastructure, which included systems…
Thousands of wind and solar park systems sit exposed on the internet across Europe
A recent report by Modat and the Dutch government's cybersecurity center, NCSC-NL, has revealed that 8,547 industrial control systems at wind and solar energy facilities across 35 countries in and around the European Union are directly accessible from the internet. These systems, which should be isolated from public networks, range from basic login portals to turbine control interfaces…
Cisco Patches a Dozen Critical Vulnerabilities
Cisco has released patches addressing a dozen critical vulnerabilities across its product line. These security defects reportedly encompass a range of potential impacts, including unauthorized access, information leaks, privilege escalation, denial-of-service (DoS) attacks, and remote code execution (RCE). The widespread nature of these reported flaws suggests a significant security update…
Evolution of Web3 in Cloud Supply Chain Attacks
Threat actors are increasingly leveraging Web3 technologies, including smart contracts and blockchain networks, to enhance their command-and-control (C2) infrastructure in cloud supply chain attacks. This evolution allows for dynamic updates to botnets and worm networks through single smart contract transactions, bypassing traditional Web 2.0-style network monitoring and making C2…
US posts $10 million reward for accused Chinese ‘Hafnium’ hacker
The U.S. State Department has announced a reward of up to $10 million for information leading to the arrest or conviction of Zhang Yu, a Chinese national accused of involvement in the Hafnium hacking campaign. Zhang is alleged to be a central figure in a series of cyberattacks that compromised thousands of computers globally and stole sensitive data, including COVID-19 research.
Major rules for federal contractors handling sensitive data are nearing the finish line
Federal government contractors handling sensitive information are poised for significant new regulations concerning data protection and breach reporting. These forthcoming rules, which define "controlled unclassified information" (CUI) as a category of sensitive data below classified status—including personal information like Social Security numbers and critical infrastructure…

Four Compliance Frameworks, One Security Team. How Universities Can Stop Drowning in Regulatory Risk
Universities face a uniquely complex regulatory landscape, often requiring compliance with four distinct federal frameworks simultaneously, each with its own security requirements, reporting timelines, and potential penalties. This challenge is compounded in multi-campus systems where IT environments, tools, staff, and data governance practices may vary by institution. The scale of the threat…
Georgia Power, Alabama Power Data Breach Hits 400,000 Accounts
Southern Company is in the process of notifying approximately 400,000 customers of its Georgia Power and Alabama Power subsidiaries about a data breach. The incident reportedly resulted in unauthorized access to customer utility account information. The scope of the breach specifically impacts accounts associated with these two power companies.
FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach
The U.S. Federal Bureau of Investigation (FBI) has reportedly removed an Accenture contractor following an alleged security failure that contributed to a data breach attributed to the ShinyHunters threat group. This incident is said to have resulted in the theft of personal details belonging to thousands of FBI employees. The reported cause of the breach was a patch failure.
Frontline Education Breach Impacts K-12 School District Staff
Frontline Education, a prominent software provider for K-12 school districts in the United States, has confirmed a data breach that exposed the personal information of school staff. The incident, which was discovered on August 14, 2026, stemmed from a vulnerability in a third-party software product utilized by the company.
Danish university DTU breach exposes data of up to 200,000 people
The Technical University of Denmark (DTU) has disclosed a data breach that may have exposed personal information belonging to as many as 200,000 individuals. The incident involved unauthorized access to DTUBasen, the university's identity and access management (IAM) system, by an attacker using compromised credentials.
Dutch Vulnerability Institute Breached Via Zammad 0-Days
The Dutch Institute for Vulnerability Disclosure (DIVD) has reportedly suffered a security breach, with attackers exploiting two zero-day vulnerabilities in the Zammad ticketing system. The incident led to remote code execution and ultimately granted the attackers root access to affected systems.
Frontline Education breach exposes school district employee data
Frontline Education, a provider of administration and workforce management software for school districts, has confirmed a data breach that exposed employee information, including Social Security numbers, after attackers exploited a vulnerability in a third-party software product. The company began notifying affected school districts of the incident in early October 2026.
Warlock ransomware breach SharePoint in water, telecom operator attacks
The Warlock ransomware group, identified by Symantec as Longlegs, has been observed targeting a range of organizations, including a water utility, a telecommunications provider, a regional government body, and a university. These attacks, which have primarily focused on Portuguese and Spanish-speaking countries in Europe, Africa, and Latin America over the past two months, leverage…
AI agent used Zammad zero-days to breach Dutch vulnerability disclosure non-profit
The Dutch Institute for Vulnerability Disclosure (DIVD), a non-profit organization that identifies and reports software vulnerabilities, confirmed it was breached on September 21 through the exploitation of two zero-day vulnerabilities in Zammad, an open-source helpdesk and customer support ticketing system. The attack was attributed to an "agentic AI" system, which reportedly used the flaws…
Over 543,000 valid credentials exposed in public GitHub repositories
More than 543,000 valid credentials were found exposed in public GitHub repositories as of July 2026, despite the platform's security measures designed to prevent such leaks. Research conducted by Truffle Security, based on a dataset assembled for training large language models from a crawl that concluded on August 7, 2025, revealed that the median duration a unique credential remained…
Most open critical and high flaws are over 90 days old
A recent analysis of internet-facing systems across 1,293 organizations in the US, UK, and Nordics revealed that the vast majority of critical and high-severity vulnerabilities remain unaddressed for over 90 days. Specifically, 97% of such flaws in the Nordics, 92% in the UK, and 86% in the US had been exposed for more than three months at the time of the study.
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
The ShinyHunters cybercrime group has claimed responsibility for breaching and defacing the data leak site operated by the Clop ransomware gang. The attack, which began on a Friday night, involved defacing Clop's Tor-based site with ASCII art and a message, and ShinyHunters alleges it also stole server data and private keys for Clop's onion service.
AI Helps Hackers Hijack OpenAI Staff Accounts Through a Forum
Three researchers from Hacktron successfully exploited a vulnerability in the Discourse forum used by OpenAI, gaining unauthorized access to staff accounts for ChatGPT and Codex. The attack, which took less than 72 hours from initial discovery to accessing an internal OpenAI code repository, highlighted risks associated with shared single sign-on (SSO) systems.
Gyazo Data Breach Exposes 23 Million User Records
Helpfeel, the Japanese software company behind the Gyazo image-sharing service, has confirmed a data breach that exposed approximately 23.62 million user records. The unauthorized access occurred on September 11, 2026, when an attacker exploited a vulnerability in Gyazo's image upload server, allowing them to execute malicious commands.
Hardcoded MCP credentials found in public GitHub files
Hardcoded credentials for AI coding tools have been discovered in publicly accessible configuration files on GitHub, potentially exposing sensitive access tokens and API keys. The findings come from a recent analysis of approximately 82,000 configuration files, revealing that 12% of credential slots contained a hardcoded literal.
98% of fraudulent hires have company credentials by the time they’re caught
A new report from HYPR indicates that 98% of fraudulent hires obtain company credentials before their deception is detected. This finding highlights a significant vulnerability in enterprise identity security, particularly a "blind spot" during the 90-day period between hiring and onboarding.
Most WordPress pros still lack a breach recovery plan
A recent survey of 319 WordPress professionals indicates that a significant majority lack a defined breach recovery plan, despite most having experienced at least one security incident. The survey, conducted by Melapress, a developer of WordPress security plugins, included agency staff, developers, designers, site owners, and administrators who build and manage WordPress sites professionally.…
First Agentic AI Data Breach Reported to Spanish Regulator
Spanish regulatory authorities have reportedly received a notification concerning what is being described as the first agentic AI data breach. The incident involved an artificial intelligence agent that autonomously executed a sequence of actions, including a successful login, the discovery of a vulnerability, and subsequent access to personal data. This event is being highlighted as a…
The modern attack chain: Rethinking Google Workspace security in the age of AI
Recent cybersecurity incidents involving Vercel and Composio have revealed an evolving attack chain targeting Google Workspace, where initial compromise often bypasses traditional email-centric defenses. This new pattern, which leverages stolen OAuth tokens as an entry point, mirrors the operational model of legitimate AI agents, raising concerns about unintended data exposure even without…
Electric and gas utility CenterPoint Energy warns of data breach after dark web post
CenterPoint Energy, a major electric and gas utility, has confirmed a data breach after discovering a dark web post claiming to offer stolen customer data. The Houston-based company filed an 8-K form with the Securities Exchange Commission (SEC) on Monday evening, September 14, 2026, acknowledging that an investigation into the claims revealed unauthorized access to one of its external-facing…
Japan's Digital Agency says VPN flaw exposed 246,000 personnel records
Japan's Digital Agency has confirmed a data breach that potentially exposed personal information for approximately 246,000 individuals, primarily government employees and associated personnel. The breach originated from an exploited vulnerability in a VPN device utilized by the Government Solution Service (GSS).
Hackers target exposed Vite dev servers to steal AWS, Azure secrets
A widespread scanning campaign is targeting internet-exposed Vite development servers to steal cloud credentials and configurations, particularly for AWS and Azure deployments. The attacks leverage a high-severity vulnerability, CVE-2026-39364, which affects Vite versions 7.1.0 through 7.3.2 and the 8.x branch before 8.0.5. This flaw, disclosed on April 7, enables an unauthenticated attacker…
Pro-Ukraine Hacking Cat group deploying new malware against Russian targets
A pro-Ukraine hacktivist group known as Hacking Cat has reportedly escalated its operations against Russian targets, moving from website defacements and data leaks to more destructive attacks involving data encryption and destruction. Cybersecurity researchers have identified new custom-built hacking tools associated with the group, which has been active since approximately February 2024.
Telus Warns Customers of Account Breaches
Telus, a major telecommunications provider, has reportedly warned its customers about account breaches stemming from a multi-month campaign. The incidents involved the use of stolen credentials to gain unauthorized access to subscriber personal data and billing records. This disclosure indicates a sustained effort by malicious actors to compromise customer accounts over an extended period.
Attackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate Data
Microsoft has reported details concerning two distinct campaigns where threat actors leveraged third-party email delivery infrastructure to distribute financial fraud scam messages. These campaigns employed passkey-themed social engineering tactics to compromise cloud environments, ultimately leading to the hijacking of Microsoft cloud accounts and subsequent data exfiltration.
Revolut Exposed KYC Data After Fraudulent Government Email Passed Security Checks
Revolut, the digital banking platform, confirmed on September 12, 2026, that it inadvertently disclosed sensitive customer Know Your Customer (KYC) data to an unauthorized third party. The disclosure occurred after the company received fraudulent information requests that appeared to originate from a legitimate government agency's email domain.
Weekly Update 521: Breach Perception v. Reality
This week's security update highlights a significant disparity between public perception and the reality of cyber threats, particularly concerning the role of artificial intelligence (AI) in offensive operations. The report emphasizes that despite widespread media narratives portraying AI as a primary tool for hackers, its actual involvement in reported breaches is negligible. This challenges…
Florida says motor vehicle data breach tied to credentials stolen from officer’s personal device
The Florida Department of Highway Safety and Motor Vehicles (FLHSMV) has confirmed a data breach, attributing it to credentials stolen from a Plant City Police Department officer's personal electronic device. The department initiated an investigation on September 4 after discovering the incident.