
breach news
229 stories · page 5 of 5
Facial Recognition at Madison Square Garden
Madison Square Garden Entertainment (MSGE) has confirmed its use of facial recognition technology at its venues, including Madison Square Garden, Radio City Music Hall, and the Beacon Theatre. The company states that the technology is employed to identify individuals who have been prohibited from entering their properties.
Hermes AI agent used to automate attack on Thai Finance Ministry
A threat actor allegedly utilized the open-source Hermes AI agent in an unattended "YOLO" mode to automate post-exploitation activities during a purported breach of Thailand's Ministry of Finance. This activity was uncovered by the threat intelligence firm Hunt.io and security researcher Bob Diachenko, who identified several exposed web directories containing files related to the operation.…
Chick-fil-A data breach affects more than 13,000 customers
Chick-fil-A has confirmed that a recent credential stuffing attack compromised the personal data of over 13,000 customers. The fast-food chain detected suspicious login activity on its website and mobile app, specifically targeting Chick-fil-A One loyalty accounts, between June 17 and June 19.
Data Breach Confirmed After Australian Energy Giant Origin Is Hacked
Origin Energy, a major Australian energy provider, has confirmed a data breach following claims by a hacker to have stolen information belonging to approximately 2 million of its customers. The threat actor has reportedly threatened to leak the stolen data if their demands are not met.
Australian energy provider Origin says data breach exposes client data
Origin Energy, a major Australian energy retailer, has confirmed a data breach that exposed personally identifiable information (PII) of some of its 4.8 million customers. The company, which provides electricity, natural gas, and broadband internet services, is currently investigating the full scope of the incident to notify affected individuals.
South Korea discloses data breach impacting diplomats worldwide
South Korea's Ministry of Foreign Affairs (MFA) has confirmed a data breach affecting the National Diplomatic Academy's online education system, leading to the exposure of personal information belonging to current and former employees, including diplomats stationed abroad. The breach, which occurred between April 2025 and February 2026, was attributed to an unknown threat actor exploiting a…
Chick-fil-A discloses data breach after credential stuffing attacks
Chick-fil-A has disclosed a data breach affecting an unspecified number of customers, attributing the incident to a series of credential stuffing attacks that targeted its website and mobile application in June. The fast-food chain, which operates over 3,000 restaurants across multiple countries, began notifying affected individuals through data breach letters filed with various Attorney…
Clover Health Investments Discloses Data Breach
Clover Health Investments has disclosed a data breach resulting from a social engineering attack. The incident led to the compromise of employee accounts, which subsequently provided unauthorized access to personal and health information.
PR3TACK preemptive framework maps threats before attackers use them
A new open framework, PR3TACK (Preemptive Tactics and Countermeasures Knowledgebase), aims to map potential attacker techniques before they are observed in active intrusions. Developed by Vishal Thakur of Atlassian, PR3TACK is designed to bridge the gap between the emergence of new attack methods and their documentation in defensive frameworks, which typically catalog techniques only after…
Estée Lauder discloses data breach via Oracle E-Business flaw
Estée Lauder, the global cosmetics firm, has confirmed a data breach stemming from an exploited vulnerability in its Oracle E-Business Suite (EBS) system, which the company utilized for human resources (HR) operations. The company's investigation determined that an unauthorized third party gained access to the system and obtained personal information of certain individuals on or around August…
Hugging Face Says Autonomous AI Agent System Breached Production Infrastructure
Hugging Face has reported a security incident where an autonomous AI agent system successfully breached a portion of its production infrastructure. The company indicated that the AI-led cyberattack resulted in unauthorized access to a limited number of datasets and service credentials.
Exposed Server Reveals AI-Assisted Phishing Toolkit Behind WebDAV Malware Campaign
Security researchers at Rapid7 have reportedly uncovered an AI-assisted phishing toolkit after a malware operator inadvertently exposed their delivery server. The server, left wide open, contained 1,048 files, offering a comprehensive look into the attacker's operations. This cache included lure templates, tests for filename spoofing, execution experiments, various droppers, builder notes, and…
20th July – Threat Intelligence Report
Ernst & Young, a global accounting and professional services firm, has disclosed a data breach stemming from a compromised third-party IT support platform. The incident potentially exposed sensitive information, including client documents, tax details, and employee data, which had been submitted in support tickets.
Hugging Face breached by autonomous AI agent
Hugging Face, a prominent platform for open-source machine learning models and datasets, has confirmed a security breach that it attributes to an autonomous AI agent system. The company disclosed the incident in a blog post published on Thursday, July 16, following the detection of unauthorized access earlier that week.
More alerts are making your team slower, and an outcome-based SOC fixes that
--- Source 2 --- Rapid7 Unveils AI-Powered SOC Platform to Combat Alert Fatigue and Accelerate Threat Response
Your Period Tracker Is (Probably) Spying on You
A recent audit by the Mozilla Foundation, conducted in partnership with Harvard's Berkman Klein Center, has revealed significant privacy concerns with several popular period tracking applications, with one app, Stardust, scoring particularly low. The audit examined six widely used trackers, finding that most engaged in data sharing practices that could compromise user privacy.
New TrojPix Attack Leaks Data From Air-Gapped Systems via Video Cable Emissions
Researchers have developed a novel method, dubbed TrojPix, capable of exfiltrating data from air-gapped systems by manipulating on-screen pixels. This technique exploits the electromagnetic emissions generated by video cables to transmit sensitive information.
U.S. Government Entity Paid Kairos $1 Million in Data-Theft Extortion Case
A U.S. government entity reportedly paid approximately $1 million to a cybercriminal group named Kairos to prevent the leak of stolen data. This information comes from a case study published by Ransom-ISAC, which analyzed a leaked negotiation transcript and the blockchain records associated with the payment.
Attackers Seize Exposed AI Endpoints to Power Offensive Ops
Cybercriminals are reportedly exploiting publicly accessible artificial intelligence (AI) endpoints to fuel their malicious operations. The exact nature of these offensive operations is not detailed, but the exploitation of AI infrastructure indicates a new avenue for threat actors.
Iran, Russia, China Target Water Systems for Sabotage
Nation-state actors, reportedly from Iran, Russia, and China, have successfully infiltrated industrial control systems within the water sector, exploiting basic security vulnerabilities rather than advanced malware. These attacks have targeted Programmable Logic Controllers (PLCs) that manage critical water infrastructure operations.
Third-Party Breaches Teach Education Sector a Costly Lesson in Vendor Risk
The education sector is facing increasing risks from third-party breaches, prompting institutions to bolster their defenses against attacks targeting sensitive student data. These attacks often involve ransomware and other malicious activities, highlighting a critical need for improved vendor risk management.
Maine forced to take down data breach portal after fake notices filed with authorities
The state of Maine has temporarily taken down its public data breach notification portal after malicious actors submitted fraudulent breach disclosures, impersonating well-known technology companies. The false reports were publicly posted before their authenticity could be verified, leading the named companies to deny any breach had occurred.
Privacy own-goal: World Cup blunder leaks Lionel Messi’s passport details
Details from the passports of every player on Argentina's World Cup squad, including star player Lionel Messi, were inadvertently leaked to the public ahead of a recent match. The sensitive information was present on an official team sheet circulated before a friendly game against Iceland.
Weekly Update 507
A cybersecurity data breach tracking initiative has surpassed a significant milestone, having now documented over 1,000 separate data breaches. This achievement represents not only the collection and verification of breach data but also the extensive operational efforts required to maintain the service.
1,000 Data Breaches Later, the Disclosure Lag is Worse Than Ever
The 1,000th data breach has been added to the Have I Been Pwned (HIBP) service, a milestone that prompts reflection on the persistent need for such tools. The ongoing accumulation of data breaches suggests that the time lag between a breach occurring and its public disclosure may be worsening.
Weekly Update 506
A recent wave of data breaches attributed to the threat actor group ShinyHunters has brought renewed attention to the challenges organizations face in responding to and disclosing such incidents. While the criminal nature of these attacks is evident, the varying degrees of organizational response, including instances of non-disclosure, highlight ongoing issues in cybersecurity incident…
MyPillow listed on ransomware gang’s leak site, but denies it has been breached
The ransomware group known as Play is claiming to have exfiltrated data from the US-based pillow manufacturer MyPillow. The group posted on its dark web leak site that it had obtained private and personal confidential information. Play threatened to release an unspecified amount of this data on Friday, potentially exposing documents related to clients, budgets, payroll, identification, taxes,…
Lawmakers Demand Answers as CISA Tries to Contain Data Leak
Lawmakers on Capitol Hill are demanding answers from the U.S. Cybersecurity & Infrastructure Security Agency (CISA) following a report that a contractor intentionally exposed a significant amount of sensitive agency data, including AWS GovCloud keys, on a public GitHub account. The breach has prompted an inquiry from both houses of Congress as CISA works to mitigate the fallout and revoke the…
CISA Admin Leaked AWS GovCloud Keys on Github
A contractor for the Cybersecurity & Infrastructure Security Agency (CISA) inadvertently exposed highly privileged credentials for AWS GovCloud accounts and numerous internal CISA systems through a public GitHub repository. Security experts have described the leak as one of the most significant government data exposures in recent history, containing details on CISA's internal software…
Weekly Update 504
The debate surrounding whether to pay ransoms to cybercriminals to prevent data leaks continues to be a significant concern for organizations. In a recent development, Grafana, a popular open-source analytics and monitoring solution, reportedly chose not to pay a ransom demand. This decision comes amidst ongoing discussions about the efficacy and ethical implications of ransom payments in the…
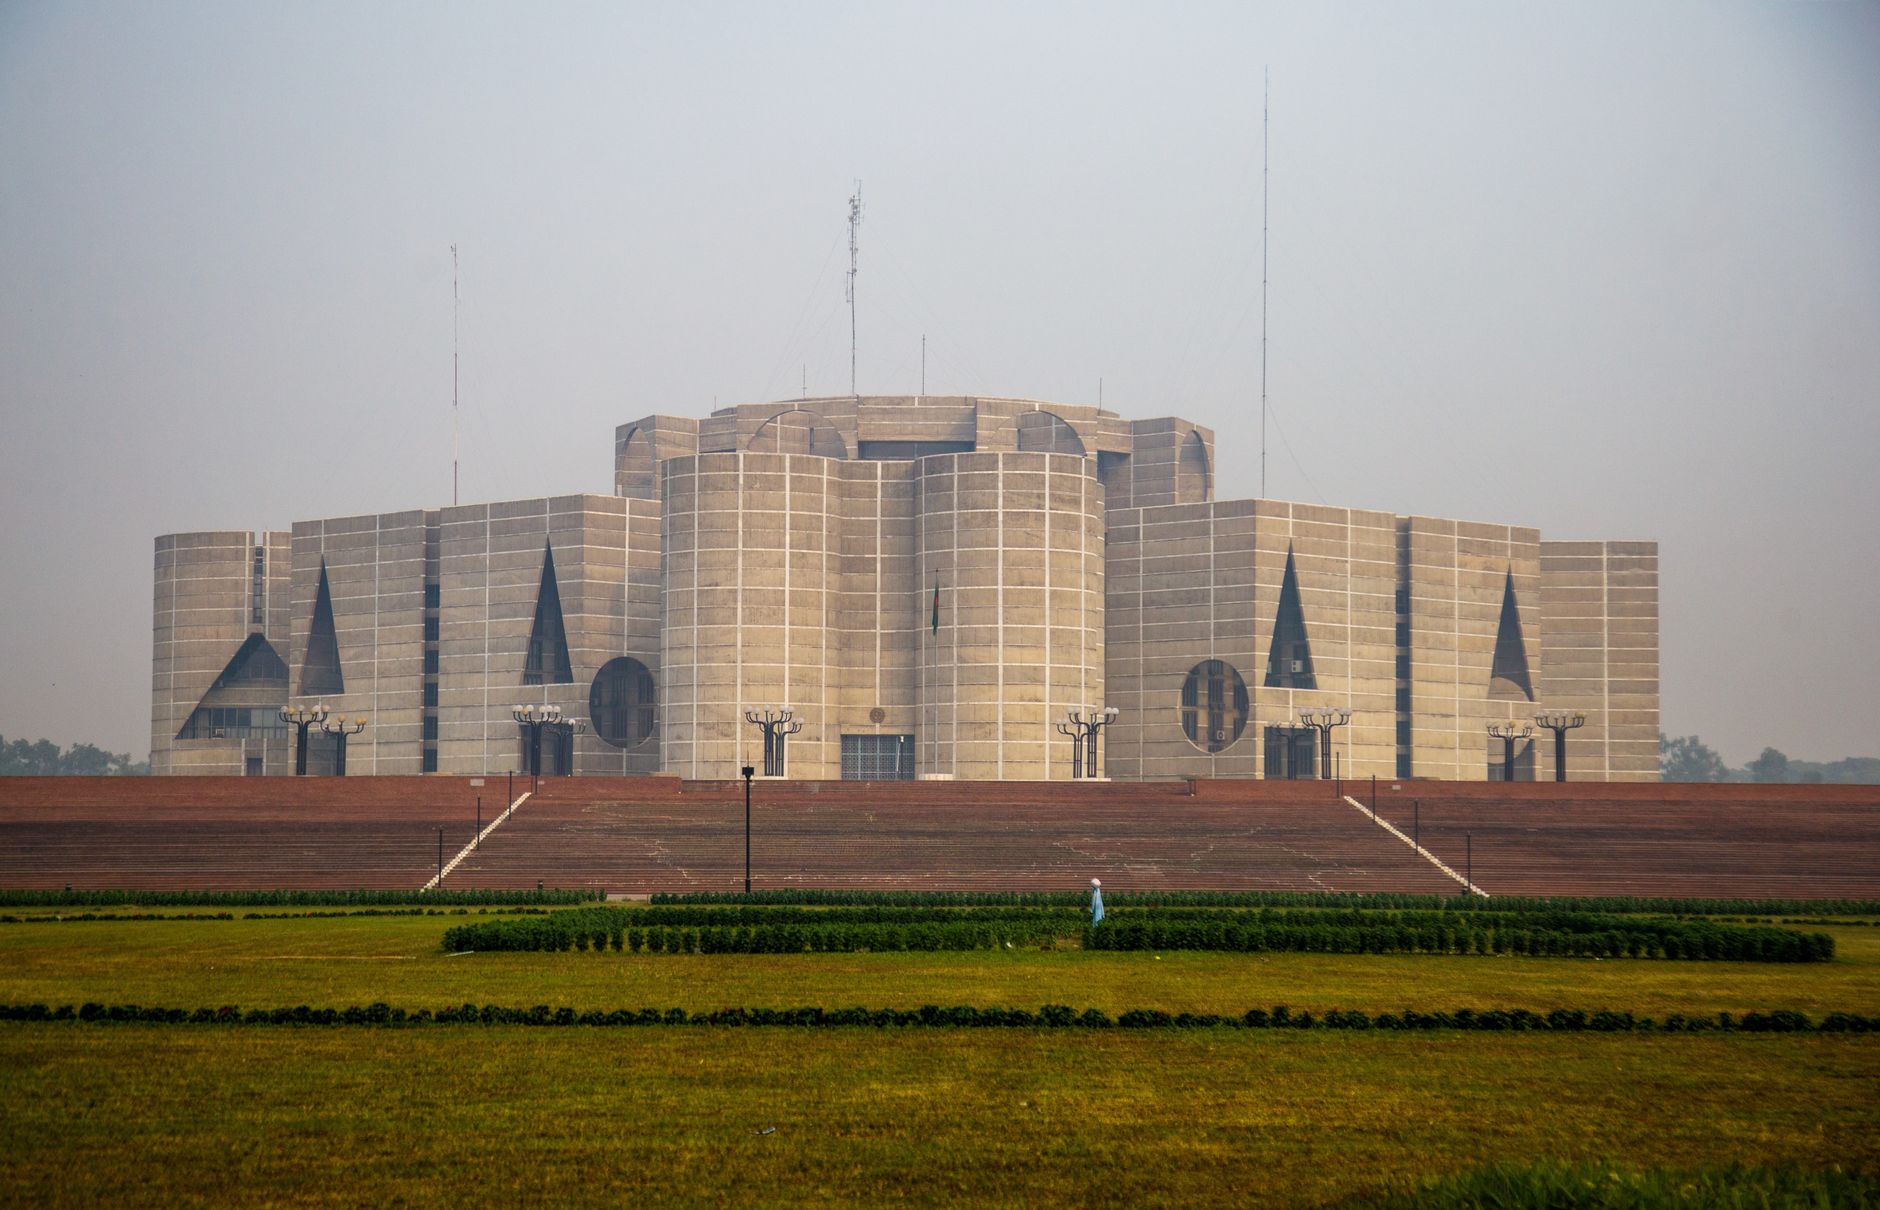
Welcoming the Bangladesh Government to Have I Been Pwned
The government of Bangladesh has joined a growing list of nations utilizing the Have I Been Pwned (HIBP) service to enhance its cybersecurity posture. The BGD e-GOV CIRT department has been granted full access to HIBP's free government service, enabling them to monitor their official domains against data breaches.
Weekly Update 503
Instructure, the company behind the Canvas learning management system, has not yet publicly addressed a potential data breach, despite a deadline set by a ransomware group known as ShinyHunters. The group had threatened to leak data allegedly stolen from Instructure by November 20th.
A Deep Dive into the GetProcessHandleFromHwnd API
The GetProcessHandleFromHwnd API, a Windows function that allows an application to obtain a handle to the process owning a specific window handle (HWND), has undergone significant changes since its introduction, with its original documentation containing several inaccuracies. Initially believed to be a convenience function relying on window hooks, its implementation and security properties…
Bypassing Administrator Protection by Abusing UI Access
A security researcher has detailed multiple vulnerabilities in Windows' User Account Control (UAC) system, specifically concerning the "UI Access" feature, which were present even before the introduction of Administrator Protection. These bypasses, totaling nine discovered by James Forshaw, have since been addressed by Microsoft. This article focuses on five of these issues, stemming from the…
Breaking the Sound Barrier, Part II: Exploiting CVE-2024-54529
A type confusion vulnerability in Apple's CoreAudio framework, identified as CVE-2024-54529, has been successfully exploited by a Google security engineer. The vulnerability resides within the `coreaudiod` system daemon, specifically in the `com.apple.audio.audiohald` Mach service. Researchers discovered that certain message handlers within this service would retrieve an object from an…
A 0-click exploit chain for the Pixel 9 Part 2: Cracking the Sandbox with a Big Wave
A security researcher has identified a critical vulnerability in the Linux kernel used by Google Pixel devices, specifically affecting the BigWave hardware accelerator. This flaw, if exploited, could allow an attacker to escape the restricted "mediacodec" sandbox and gain arbitrary read and write capabilities within the kernel. The vulnerability was discovered by Seth Jenkins, who detailed his…
A 0-click exploit chain for the Pixel 9 Part 1: Decoding Dolby
Google's Pixel 9 devices are susceptible to a zero-click exploit chain that targets the Dolby Unified Decoder (UDC), a component responsible for processing Dolby Digital and Dolby Digital Plus audio formats. This vulnerability allows for arbitrary code execution within the mediacodec context of the device, forming the first stage of a more complex attack. The exploit chain was developed by…