
vulnerability news
725 stories · page 9 of 16
CISA Warns of Exploited Oracle WebLogic Vulnerability
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding an actively exploited vulnerability in Oracle WebLogic Server. The flaw, identified as CVE-2026-21962, is reportedly being widely leveraged by various threat actors targeting WebLogic installations.
Actively Exploited Oracle WebLogic Flaw Lets Unauthenticated Attackers Access Critical Data
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical security flaw affecting Oracle WebLogic Server and Oracle HTTP Server to its Known Exploited Vulnerabilities (KEV) catalog. The agency cited evidence of active exploitation for this maximum-severity vulnerability.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days
A zero-day elevation-of-privilege vulnerability, tracked as CVE-2026-69414 and dubbed "ShieldBreak," has been discovered in the Microsoft Malware Protection Engine, which is integral to Microsoft Defender. This flaw allows a local attacker with low privileges to escalate to SYSTEM-level access on affected Windows systems.
Exploited Zimbra Flaw Highlights Shrinking Window to Patch
A recently exploited vulnerability in Zimbra, identified as CVE-2026-73570, has prompted a directive from the Cybersecurity and Infrastructure Security Agency (CISA) for federal agencies to apply patches within a three-day window. The flaw is reported to enable a complete takeover of a user's communications, underscoring the critical nature of the exploit and the urgency of mitigation.
Unpatched Calix flaw lets hackers bypass NAT to expose internal devices
An unpatched vulnerability in Calix GS7 XGS (GS5239XG) residential routers, also marketed as the GigaSpire 7u10txg, allows remote, unauthenticated attackers to create port-forwarding rules that expose internal network devices to the public internet. The flaw, tracked as CVE-2026-75501, is a missing authentication issue affecting devices running EXOS/6.6.47 firmware.
Hackers target WordPress sites in miniOrange auth bypass attacks
Threat actors are actively attempting to exploit two critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On plugin for WordPress. These vulnerabilities, tracked as CVE-2026-61979 and CVE-2026-15981, can be chained together to forge SAML responses and gain administrative access to affected WordPress sites.
CISA orders urgent patching of actively exploited Zimbra flaw
The Cybersecurity and Infrastructure Security Agency (CISA) has mandated that U.S. government agencies patch an actively exploited vulnerability in Zimbra Collaboration Suite (ZCS) within three days. The deadline for Federal Civilian Executive Branch (FCEB) agencies to secure their systems was set for August 24.
Rethinking Application Security for the AI Era
Recent analysis suggests that the advent of artificial intelligence (AI) is significantly accelerating the window between the public disclosure of a software vulnerability and its active exploitation by malicious actors. This compressed timeline necessitates a fundamental shift in how enterprises approach application security, moving beyond traditional reactive patching strategies to more…
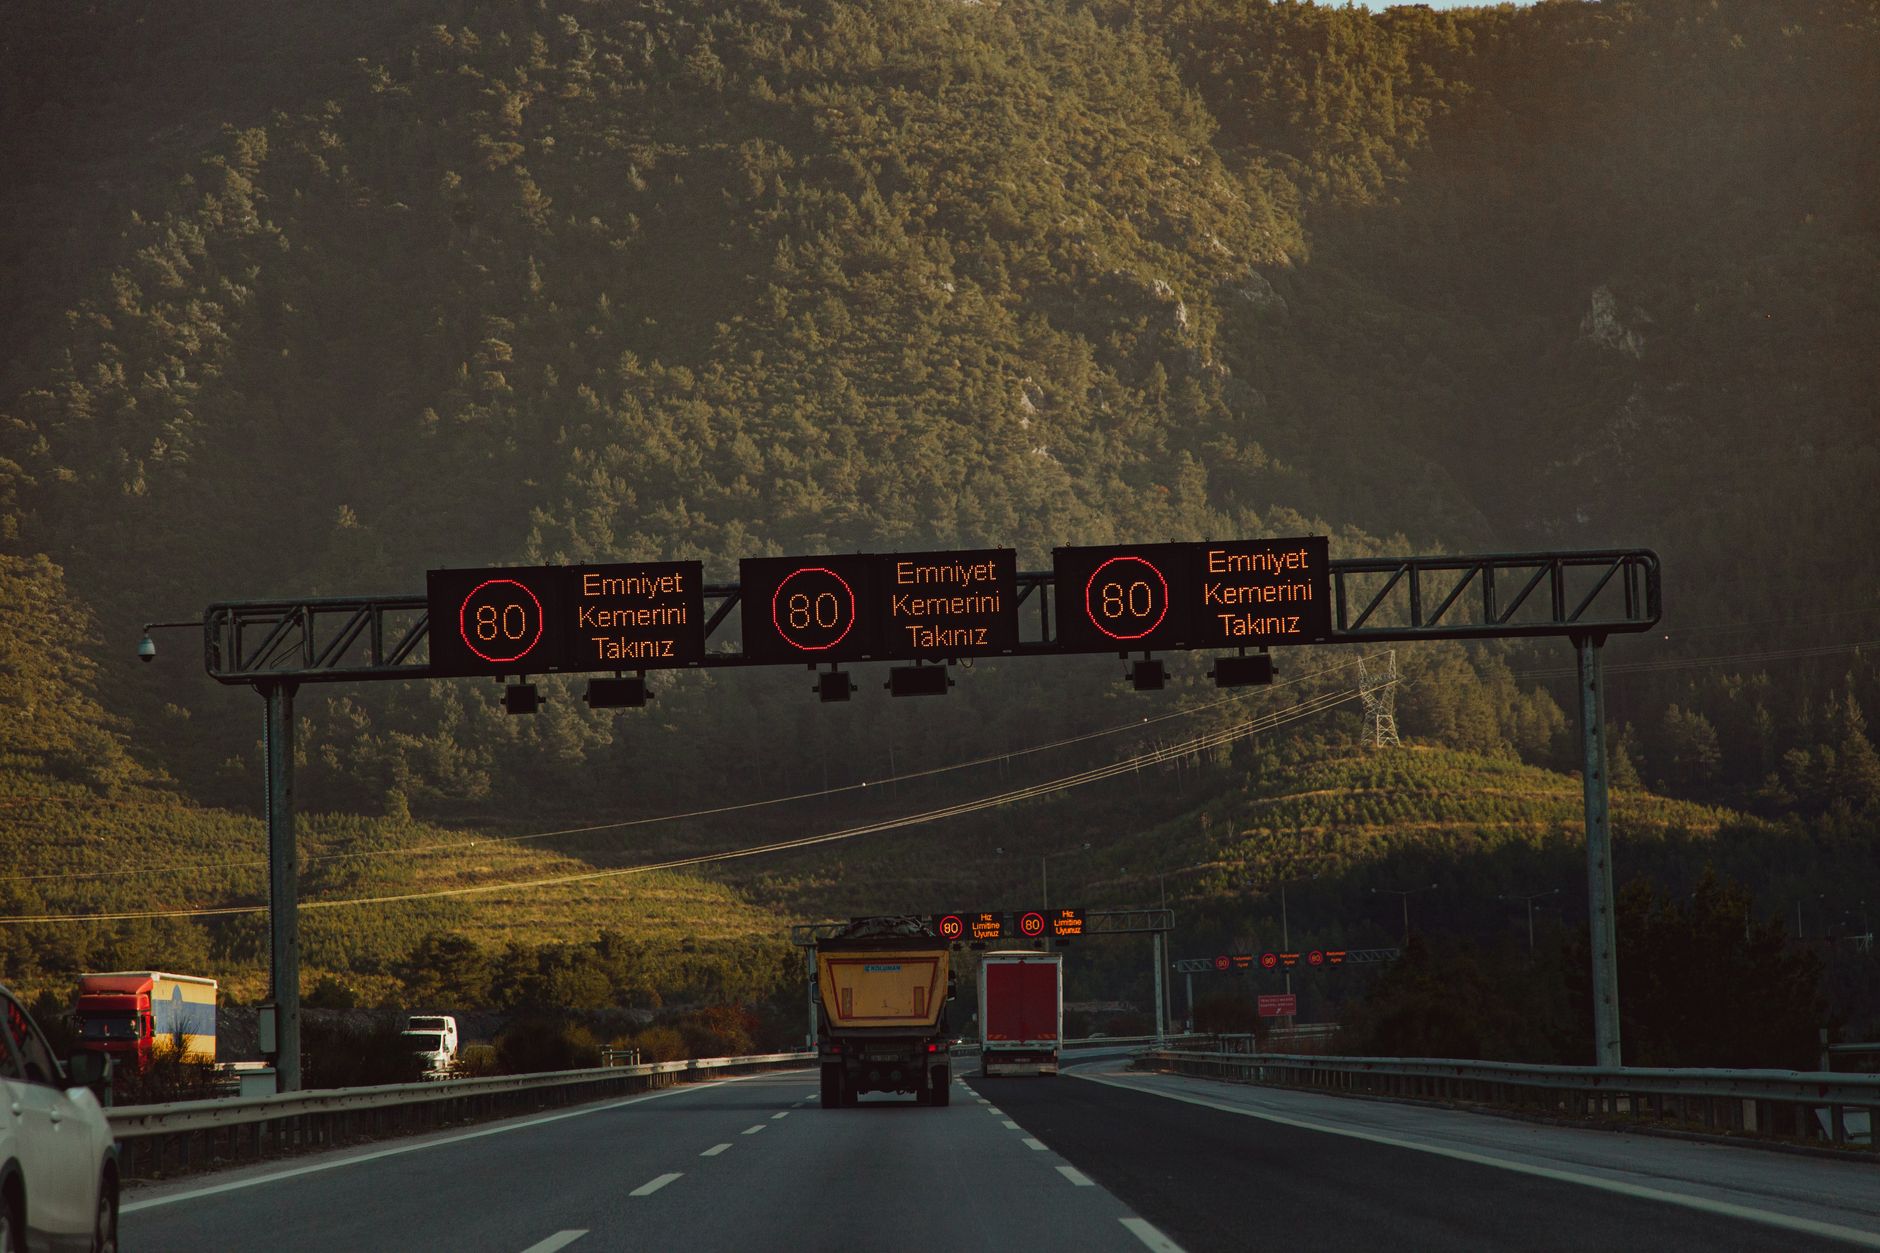
Slovakia Warns of Cyber Risks in Road Speed Cameras
Slovakia's National Security Authority (NBÚ) has issued a warning regarding significant cybersecurity risks associated with several types of road speed cameras, identifying them as potential threats to public networks and sensitive vehicle data. The alert, prompted by a request from the Interior Ministry, focuses on connected devices that collect vehicle information, communicate with other…
ToxicPanda 2.0 Gets a Major Upgrade, Expanding Attacks Across 16 Countries
A significantly upgraded version of the ToxicPanda Android malware, dubbed ToxicPanda 2.0, has expanded its targeting to 349 financial applications across 16 countries, a substantial increase from the 16 applications it previously targeted. Researchers at Zimperium's zLabs team documented the new variant, noting its command set has grown to 167 remote instructions.
Critical Flaw in NASA/JPL Open-Source Spacecraft Command Software Allowed Unauthenticated Command Execution
A critical vulnerability has been identified in AIT-GUI, the browser-based operator console for NASA/JPL's open-source AMMOS Instrument Toolkit. The flaw, rated with a CVSS score of 9.4 and tracked as GHSA-p9r8-2q67-fp86, allowed unauthenticated execution of commands on spacecraft instruments. The issue has been addressed in AIT-GUI version 2.5.2.
U.S. CISA adds Zimbra Collaboration Suite (ZCS) flaw to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in Zimbra Collaboration Suite (ZCS), identified as CVE-2026-73570, to its Known Exploited Vulnerabilities (KEV) catalog. This move mandates that all U.S. federal civilian executive branch (FCEB) agencies address the flaw by August 24, 2026, to protect their networks, and private organizations…
Homeland security cybercops say patch TrueConf (Russia's Zoom) if you're using it
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has mandated that federal agencies patch two actively exploited vulnerabilities in TrueConf Server, a video conferencing platform developed in Russia. The flaws, identified as CVE-2026-72529 and CVE-2026-72530, were added to CISA's Known Exploited Vulnerabilities catalog on Thursday, indicating their use in real-world attacks.…
Microsoft Defender's Own Driver Can Be Weaponized to Delete Security Software at Boot
Check Point Research has disclosed a technique that leverages a legitimate Microsoft Defender driver, BTR.sys (Boot Time Removal Tool), to delete security software at boot time. The technique reportedly does not exploit a software flaw but rather weaponizes the driver's intended functionality. This method is said to affect Windows systems from Windows 7 up to Windows 11 25H2.
In Other News: Zombie Card Attack, T-Mobile Cut Cable to Stop Hackers, GitHub Denies AI Caused Bug
A recent report highlighted several security incidents and developments, including a "Zombie Card" attack, a distributed denial-of-service (DDoS) attack against Threema, and the emergence of the Evooo1Bot Linux botnet. Additionally, T-Mobile reportedly severed a cable in an attempt to thwart attackers, while GitHub denied that artificial intelligence was responsible for a specific bug.…
Six Maximum-Severity Flaws Found in Cisco Products
Cisco has released a series of security patches addressing nine vulnerabilities across its Crosswork platforms and Secure Workload software, with six of these flaws receiving the maximum CVSS score of 10.0. The vulnerabilities were discovered during an internal security review conducted by Cisco's engineering team, which included the use of advanced AI models. As of the announcement on August…
Critical Isolated-vm Vulnerability Leads to RCE on Host
A critical vulnerability has been reported in the `isolated-vm` library, a Node.js module designed for running untrusted code in a sandboxed environment. The flaw, described as a type confusion bug, could allow an attacker to achieve remote code execution (RCE) on the host system by escaping the V8 sandbox and hijacking the control flow of the host process.
CISA orders feds to patch actively exploited TrueConf Server flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has directed federal agencies to immediately patch two critical vulnerabilities in the TrueConf Server self-hosted communications platform, which are reportedly being actively exploited in the wild. The directive, issued on Thursday, August 21, 2026, requires all U.S. Federal Civilian Executive Branch (FCEB) agencies to secure…
Critical Microsoft Entra ID vulnerability exploited in the wild (CVE-2026-69836)
Microsoft has issued a patch for a critical remote code execution vulnerability, identified as CVE-2026-69836, within its Entra ID cloud identity service. The company confirmed that the vulnerability has been actively exploited in the wild. Entra ID, previously known as Azure Active Directory, is a core Microsoft service responsible for authenticating user logins and managing access to…
Microsoft warns of max severity Entra ID flaw exploited in attacks
Microsoft has confirmed it has patched a critical vulnerability in its Entra ID identity and access management (IAM) platform, previously known as Azure Active Directory. The flaw, tracked as CVE-2026-69836, has a maximum severity rating and has been exploited in active attacks.
SickKids data breach exposes employee and job applicant info
The Hospital for Sick Children (SickKids) has disclosed a cybersecurity incident that exposed the personal information of some current and former employees, as well as job applicants. The Toronto-based pediatric hospital confirmed that the breach originated from a vulnerability in a third-party software application used by SickKids and other organizations.
GitLab Critical GraphQL Flaw Actively Exploited
GitLab has confirmed that a critical vulnerability in its GraphQL API, identified as CVE-2026-19478, is being actively exploited in the wild. The flaw, which carries a CVSS score of 9.4, allows unauthenticated attackers to remotely modify or delete public projects and associated user data on self-managed GitLab instances.
Poland’s CERT Warns of Active Exploitation of Critical Zimbra Collaboration Suite Flaw
CERT Polska has confirmed active exploitation of a critical unauthenticated remote code execution vulnerability in Zimbra Collaboration Suite, identified as CVE-2026-73570. The flaw, which allows attackers to execute arbitrary shell commands with the privileges of the `zimbra` user, was patched by Zimbra on July 20, 2026, in version 10.1.20. Active exploitation was confirmed less than a month…
U.S. CISA adds TrueConf Server flaws to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two critical vulnerabilities in TrueConf Server, an on-premises video conferencing and unified communications platform, to its Known Exploited Vulnerabilities (KEV) catalog. The flaws, identified as CVE-2026-72529 and CVE-2026-72530, both carry high CVSS scores, indicating their severity.
Microsoft Rolls Out 22 Fresh Security Patches
Microsoft has released 22 new security patches, addressing a range of vulnerabilities across its product line. The majority of these fixes target issues related to remote code execution, privilege escalation, and information disclosure. This regular update cycle is a standard practice for major software vendors to maintain the security posture of their offerings.
Citrix urges customers to fix critical NetScaler authentication bypass (CVE-2026-19490)
Citrix has issued an urgent advisory for customers to patch two critical vulnerabilities in its NetScaler ADC and NetScaler Gateway products, including a severe authentication bypass flaw identified as CVE-2026-19490. The company, through its parent Cloud Software Group, strongly recommends that users review the official security bulletin and upgrade affected appliances immediately.
CISA Urges Immediate Patching of Exploited TrueConf Vulnerabilities
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a directive urging organizations to immediately patch critical vulnerabilities found in TrueConf software. This advisory comes as the Head Mare hacktivist group is reportedly actively exploiting these flaws to facilitate the distribution of PhantomCore malware. The directive underscores the urgency for all entities…
Cl0p Targets 40+ Organizations Through PTC Windchill Flaw
The Cl0p ransomware group claims to have compromised over 40 organizations by exploiting a critical vulnerability in PTC's Windchill and FlexPLM product lifecycle management (PLM) software. This vulnerability, identified as CVE-2026-12569, is a remote code execution (RCE) flaw with a CVSS score of 9.3, stemming from the deserialization of untrusted data. It affects all CPS versions and…
GitLab Code Injection Vulnerability Actively Exploited
A critical code injection vulnerability in GitLab, tracked as CVE-2026-19478, is reportedly being actively exploited in the wild. The flaw was publicly disclosed recently, and exploitation attempts have been observed shortly thereafter. This vulnerability allows unauthenticated attackers to manipulate or remove public projects and their associated data, though specific conditions must be met…
Microsoft Entra ID Flaw (CVSS 10.0) Exploited in Wild, Allows Remote Code Execution
Microsoft has issued a warning regarding a critical security flaw in its Entra ID cloud-based identity and access management service, which has reportedly been exploited in the wild. The vulnerability, identified as CVE-2026-69836, carries a maximum CVSS score of 10.0, indicating its severe potential impact. Despite the active exploitation, Microsoft has stated that no immediate customer…
Cisco bug severity warning reads like Olympic gymnastics scores: 10, 10, 9.9, 9.6, and 7.5.
Cisco has issued an advisory regarding five vulnerabilities discovered in its Secure Workload Software, a micro-segmentation tool previously known as Tetration. These flaws, identified during an internal security review that included the use of advanced AI models, range in severity from critical to high. Cisco confirmed that it has not observed any malicious exploitation of these…
Hackers poison arrayref Rust crate to push infostealer malware
A widely used Rust library, arrayref, was compromised through its maintainer account to distribute infostealer malware during compilation, affecting developers' systems. The attack, which occurred on August 20, also impacted two other crates, append-only-vec and internment, within a 23-minute window.
N-able Bug Exposes Password Vault Master Keys
A recently disclosed vulnerability in N-able's Passportal password manager reportedly exposed master keys for password vaults. The flaw, which affects a product widely used by Managed Service Providers (MSPs) and Small and Medium Businesses (SMBs), raises concerns about the security of cloud-based password management solutions even after a patch has been applied.
ThreatsDay: Gogs 10.0 RCE, n8n Workflow-to-RCE, $10M Reward, GLM-5.3 AI Exploit, and More
This week's cybersecurity reporting highlights a diverse array of threats and developments, including the exploitation of legitimate signed drivers for malicious kernel operations, a significant cyber espionage campaign attributed to an Iran-based threat actor targeting academic institutions, and the proliferation of malware leveraging DLL sideloading techniques. The landscape also includes…
Hackers Target Zimbra Servers in Active Exploitation Campaign
CERT Polska has reported an active exploitation campaign targeting Zimbra Collaboration servers. The campaign specifically leverages a vulnerability identified as CVE-2026-73570. Details surrounding the nature of the attacks and the specific impact on affected systems are currently emerging, with CERT Polska providing the initial public alert.
Critical Elementor Pro bug exposes WordPress sites to RCE attacks
A critical remote code execution (RCE) vulnerability, identified as CVE-2026-32475, has been discovered in the Elementor Pro WordPress plugin, potentially allowing attackers to upload executable files to affected websites. The flaw impacts Elementor Pro versions prior to 4.2.2.
JFrog Artifactory Flaws Enable Software Supply Chain Attacks
Two vulnerabilities in JFrog Artifactory have been identified that could enable anonymous or low-privileged users to manipulate package metadata without altering the underlying artifacts, potentially leading to software supply chain compromises. The flaws, reported by Oligo Security to JFrog on June 25 and publicly detailed on August 20, have since been patched by JFrog.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days
A new zero-day vulnerability, dubbed ShieldBreak and tracked as CVE-2026-69414, has been identified in the Microsoft Malware Protection Engine, a core component of Microsoft Defender. This elevation-of-privilege flaw allows a local attacker with low privileges to escalate their access to SYSTEM level on affected Windows systems.
Frequently asked questions about the active threat to Siemens S7 Series PLCs
Multiple U.S. government agencies have issued a joint cybersecurity advisory warning of active threats targeting Siemens S7 Series programmable logic controllers (PLCs) across critical infrastructure sectors. The advisory, designated AA26-231A, was released on August 19, 2026, by the National Security Agency (NSA), the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau…
Isolated-vm Flaw Lets Sandboxed JavaScript Escape to Host for Potential RCE
A significant security vulnerability has been identified in the isolated-vm Node.js library, which could allow sandboxed JavaScript code to escape its intended isolation and potentially achieve arbitrary code execution on the host system. The flaw specifically impacts the ExternalCopy component of the library.
Critical NetScaler Flaw Can Bypass Authentication on Certain Gateway and AAA Servers
Citrix has issued urgent security updates for its NetScaler ADC and NetScaler Gateway products to remediate two significant vulnerabilities. The more critical of these, tracked as CVE-2026-19490, carries a CVSS score of 9.3 and enables an authentication bypass. This flaw specifically impacts certain configurations, particularly those where the NetScaler appliance functions as a Gateway or an…
Attackers Exploit Zimbra SNMP Flaw for Unauthenticated Remote Code Execution
Attackers are reportedly exploiting a critical vulnerability in Zimbra Collaboration Suite (ZCS) that enables unauthenticated remote code execution. The flaw, tracked as CVE-2026-73570 and assigned a CVSS score of 8.9, is attributed to insufficient input sanitization within the Simple Network Management Protocol (SNMP) notification processing component of ZCS.
BTR Reforged: Weaponizing Defender’s Remediation Driver as a Kernel Operation Primitive
A security research firm has identified a method to repurpose a legitimate, Microsoft-signed Windows Defender component, BTR.sys, into a kernel operation primitive, potentially allowing attackers to execute arbitrary file and registry operations from Ring 0. This technique, dubbed "BTR Reforged," does not rely on traditional exploits, vulnerabilities, or memory corruption, but rather on the…
Atlassian, Splunk Patch Dozens of Critical, High-Severity Vulnerabilities
Atlassian and Splunk have released patches addressing numerous critical and high-severity vulnerabilities across their product lines. The reported flaws could potentially be exploited by attackers to achieve arbitrary code execution, gain unauthorized access to sensitive data, and escalate privileges within affected systems. Users of Atlassian and Splunk products are strongly advised to apply…
Citrix urges admins to patch new NetScaler flaws as soon as possible
Citrix has issued an urgent advisory to customers, recommending immediate action to secure systems against two newly disclosed vulnerabilities impacting NetScaler Gateway secure remote access solutions and NetScaler ADC networking appliances. The company confirmed these flaws affect supported versions of customer-managed NetScaler ADC and NetScaler Gateway, including specific FIPS and NDcPP…
MLflow Vulnerability Exploited for Cloud Credential Theft
A critical-severity vulnerability in MLflow has reportedly been exploited to facilitate the theft of cloud credentials. The flaw, described as allowing attackers to send HTTP requests to internal endpoints, was observed in active exploitation, leading to the extraction of sensitive information.
Zombie Card Attack Can Revive Expired Visa Cards for Contactless Payments
Researchers have reportedly developed a novel attack, dubbed "Zombie Card," capable of reactivating expired Visa contactless payment cards for in-store transactions. This method reportedly allows an attacker to bypass the expiration date check during a transaction, effectively enabling the use of otherwise invalid cards.
Cisco Patches Critical Crosswork, Secure Workload Vulnerabilities
Cisco has released patches addressing critical vulnerabilities in its Crosswork Network Automation and Secure Workload (formerly Tetration) products. These security flaws have been reported to potentially enable remote code execution, authentication bypasses, and path traversal attacks against affected systems. The patches are intended to mitigate the risk posed by these vulnerabilities.