
patch news
415 stories · page 2 of 9
GNSS Spoofing and Jamming: What They Do to RTK Positioning and How Field Teams Can Spot Them
Satellite positioning systems are increasingly vulnerable to interference that can compromise the integrity of Real-Time Kinematic (RTK) positioning without triggering obvious system alarms. While field equipment may continue to report a seemingly valid status, the underlying data can be manipulated, causing a rover to lose its fixed solution or, more critically, report inaccurate coordinates.…
Trezor confirms crypto-stealing implants in three wallets, releases fix
Hardware wallet manufacturer Trezor has officially confirmed that three of its Safe 5 devices, all sourced from the Southeast Asian reseller CryptoBilis, were equipped with malicious hardware implants. These unauthorized modifications were engineered to intercept and exfiltrate sensitive user data, including wallet recovery phrases and passphrases, by transmitting the information over cellular…
Microsoft 365 Crawls Back to Life After a 24-Hour Outage
Microsoft 365 services have begun to stabilize following a massive 24-hour outage that disrupted business, government, and personal operations across more than 70 countries. The service interruption, which began around 12:00 PM ET on Thursday, initially appeared to be localized to North America before rapidly expanding into a global event. Users reported widespread difficulties accessing core…
PostgreSQL Patches 52 Flaws, Including 22-Year-Old Bug Enabling Authenticated RCE
PostgreSQL has released security updates addressing 52 vulnerabilities, most notably a critical type confusion flaw that has persisted in the codebase for 22 years. Tracked as CVE-2026-6460, this vulnerability carries a CVSS score of 8.8 and allows an authenticated user with the ability to create database objects to execute arbitrary code on the underlying server. Because the database process…
November Patch Tuesday: How to Sort Through the Patches
The November 2026 Patch Tuesday release has highlighted a significant shift in the cybersecurity landscape, as Microsoft addressed 1,252 Common Vulnerabilities and Exposures (CVEs). This figure represents a nearly twentyfold increase compared to the 63 CVEs addressed in November 2025. Security researchers attribute this surge in part to the integration of frontier artificial intelligence…
Quantum Systems drones back in the air after malware scare
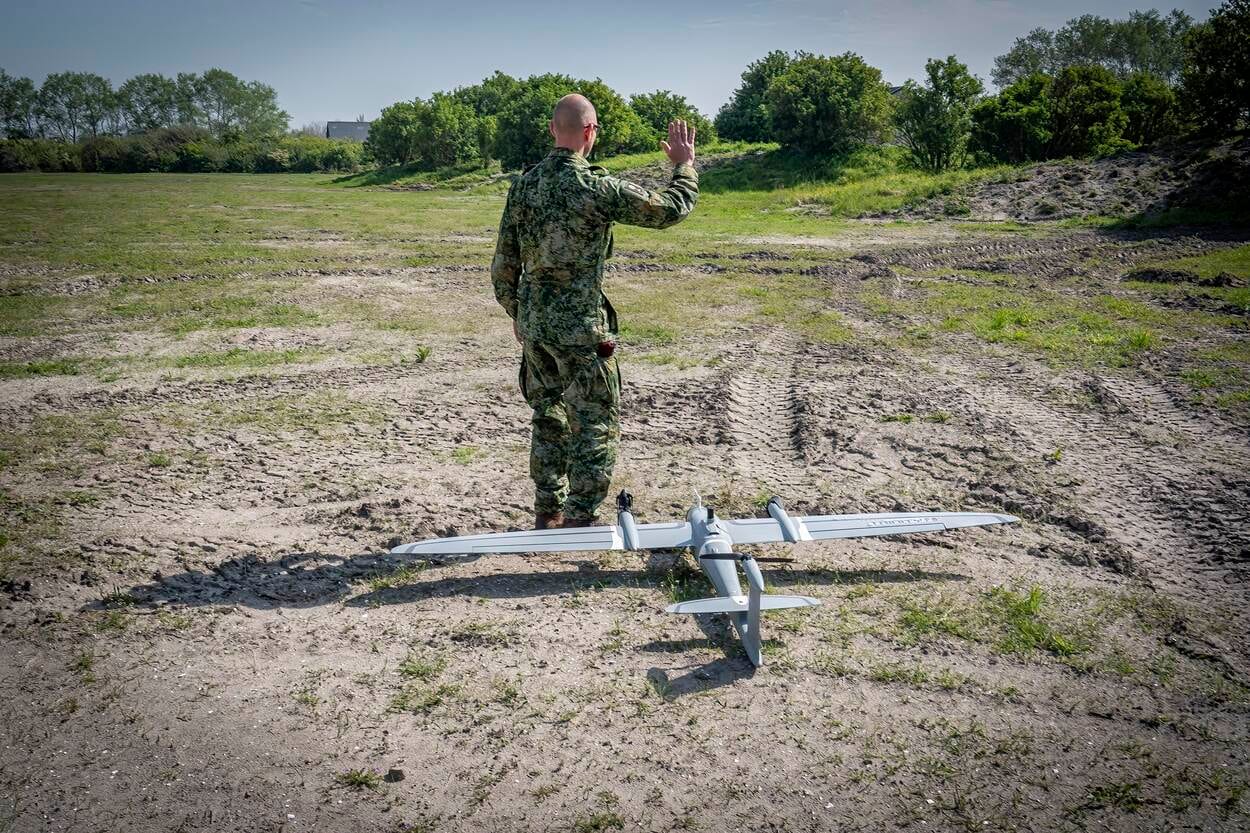
Quantum Systems has confirmed that its fleet of unmanned aerial vehicles is back in operation following a temporary grounding by the German military. The manufacturer, which provides drone technology to both the Bundeswehr and the Ukrainian armed forces, stated that it identified a cybersecurity incident in late October. According to the company, the threat was successfully contained through…
Microsoft says November security updates cause printing issues
Microsoft has officially acknowledged that the security updates released in November 2026 are causing widespread printing failures across both client and server versions of its operating system. The issue specifically impacts Windows 10 and later client versions, as well as Windows Server 2016 and subsequent iterations. According to the company, the disruption occurs when users attempt to…
AI Doesn’t Have to Go Rogue to Break the World
The rapid advancement of artificial intelligence has introduced a new category of systemic risk that extends far beyond traditional cybersecurity concerns. While public discourse often focuses on the potential for AI to be weaponized by malicious actors or to act with sentient malice, the more immediate and destabilizing threat lies in the autonomous discovery of exploits within complex…
Unpatched Check Point Gateways Are Being Wiped exploiting PHP2Shell
Check Point Security Gateways have been the target of a widespread, multi-stage exploitation campaign that began in late October 2026. The attacks utilized a combination of unpatched vulnerabilities and custom malware to gain root access, establish persistent backdoors, and, in some instances, deploy destructive wiper software. The activity, which has been observed globally, appears to have…
Google pushes second Chrome update this week
Google has released a significant security update for the Chrome browser on Windows, Mac, and Linux, marking the second such release within a single week. This update advances the browser to version 157.0.8103.78 for Linux and versions 157.0.8103.78 and 157.0.8103.79 for Windows and Mac users. The patch addresses a total of 83 security vulnerabilities, five of which have been categorized as…
Microsoft confirms Windows activation failures after November updates
Microsoft has officially acknowledged that its November 2026 security updates are triggering widespread Windows activation and licensing failures. The issue manifests as a 0x80041008 error, which is described as an invalid parameter (SWbemObjectEx) notification. This disruption specifically impacts enterprise environments that rely on automated licensing workflows or the Software Licensing…
OpenAI’s Daybreak brings AI agents to security testing and vulnerability fixes
OpenAI has introduced Daybreak, a new suite of AI-driven agents designed to automate critical phases of the software security lifecycle, including penetration testing and vulnerability remediation. The platform is divided into two primary components: Red Team, which focuses on identifying and validating security flaws, and Defense Factory, which assists in the development and implementation of…
Hackers Exploit N-central Flaws to Infect 21 Servers, Including 19 Running Hotfix 2
N-able has confirmed that attackers are actively exploiting vulnerabilities within its N-central remote monitoring and management platform. The incident has resulted in the compromise of 21 servers, with 19 of those systems running the platform’s second hotfix. In response to the breach, the vendor has begun restricting specific features and integrations to prevent further exploitation while…
Your pinned MCP server may not be as pinned as you think
A significant security vulnerability has been identified within the Model Context Protocol (MCP) ecosystem, where servers intended to run fixed, pinned versions of software are inadvertently pulling updated, unverified dependencies. Research conducted by Corelight revealed that an MCP server configured to run a specific release can undergo substantial dependency drift without any changes to…
Fake Zillow pages use ClickFix NetSupport RAT to target apartment hunters
Researchers at EfficientIP have identified a sophisticated social engineering campaign that leverages fraudulent Zillow apartment-review pages to deploy the NetSupport remote access trojan (RAT) onto Windows systems. The campaign, which first appeared in August 2026, targets individuals searching for rental properties by tricking them into executing malicious PowerShell commands. By…
PostgreSQL security update fixes 52 vulnerabilities, ends support for PostgreSQL 14
The PostgreSQL Global Development Group has issued a comprehensive security update addressing 52 distinct vulnerabilities across multiple supported versions of its database software. The patches, released on November 12, apply to versions 18.7, 17.12, 16.16, 15.20, and 14.25. In addition to these security fixes, the update resolves more than 140 non-security bugs, marking a significant…
Self-hosted Claude Managed Agents keeps agent credentials in your environment
Anthropic has introduced a self-hosted deployment option for its Claude Managed Agents platform, allowing enterprise customers to bring the agent harness, sandboxes, session history, and credential management within their own cloud or on-premise infrastructure. Previously, while customers could host the isolated sandbox environments where agent code executes, Anthropic maintained control over…
Software Samaritan revamps borked Indian certs to block smart TV ads
A significant security failure involving the Indian certificate authority eMudhra has inadvertently provided a mechanism for users to intercept and modify traffic on certain smart televisions. The incident stems from the exposure of eight intermediate certificate authority private keys, which were discovered to be cryptographically trivial. eMudhra has confirmed that these keys were generated…
Google Cloud Warns Three AMD Turin CPU Flaws Could Leak Data Across Processes in VMs
Google Cloud has issued a security advisory regarding three side-channel vulnerabilities identified in AMD Turin processors. These flaws present a risk of unauthorized data exposure across processes running within the same virtual machine (VM). While Google has already implemented infrastructure-level mitigations to prevent cross-VM and VM-to-host data leakage, users are now required to take…
Dagster: Open-source cloud-native data pipeline orchestrator
Dagster, an open-source data pipeline orchestrator designed for cloud-native environments, provides a framework for managing the execution, scheduling, and lineage of data assets. The platform functions by determining the sequence and timing of data processing tasks while tracking the relationships between various datasets, machine learning models, and reports. By mapping these connections,…
Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely
A critical vulnerability has been identified within the Apache HTTP Server’s mod_http2 module, potentially allowing unauthenticated remote attackers to execute arbitrary code on affected systems. Tracked as CVE-2026-119618, the flaw impacts Apache HTTP Server versions 2.4.55 through 2.4.70. A patch has been issued in version 2.4.71, which was released yesterday to address the security gap.
N-able Takes N-central Platform Offline After Discovery of 33 Flaws
N-able has taken its N-central remote monitoring and management (RMM) platform offline following the discovery of 33 security vulnerabilities. The company initiated this service interruption to address the flaws, which reportedly include zero-day vulnerabilities that could allow an unauthorized attacker to achieve full system takeover.
Git fixes six vulnerabilities, including code execution during recursive clones
The Git project has released a series of security updates addressing six distinct vulnerabilities that could allow for unauthorized code execution, memory corruption, or arbitrary file manipulation. These flaws are triggered when the software processes malicious repositories or specially crafted inputs. The patches are included in Git version 2.56.1, with backported fixes available for the…
N-able releases security hotfixes for zero-day vulnerabilities
N-able has released security hotfixes for its N-central remote monitoring and management platform following the public disclosure of several critical zero-day vulnerabilities. The company issued version 2026.4 HF2 to address these flaws, which were initially brought to light on November 8, 2026. The vulnerabilities affect the N-central Appliance 2026.4.0.31, though it is believed that earlier…
Red Hat OpenShift 5 brings autonomous troubleshooting to hybrid clouds
Red Hat has announced the general availability of OpenShift 5, an update to its hybrid cloud application platform that introduces autonomous troubleshooting and enhanced security features. Designed to operate across data centers, cloud environments, and disconnected or edge deployments, the platform allows IT teams to manage virtual machines, containerized workloads, and artificial…
Microsoft Fixes 1235 Flaws in Another Record Patch Tuesday
Microsoft has released its November security updates, addressing a total of 1,235 vulnerabilities across its product ecosystem. This release marks the fourth time in 2026 that the company has set a new record for the number of patches issued in a single month, following similar milestones in July, September, and October.
Cisco BroadWorks and Openwave Flaws Actively Exploited Despite Available Patches
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two security vulnerabilities affecting Cisco BroadWorks and the Openwave Messaging Webtop Media Transcoder to its Known Exploited Vulnerabilities (KEV) catalog. The agency’s inclusion of these flaws indicates that they are currently being leveraged in active, real-world attacks. Organizations utilizing these platforms…
EU cyber scores look healthy, but 45% of surveyed IT providers take months to patch
The European Union’s cybersecurity landscape presents a significant disconnect between high-level national policy scores and the operational realities of service providers, according to the 2026 assessment released by the European Union Agency for Cybersecurity (ENISA). While the agency’s revised EU Cybersecurity Index reports an average score of 71.53 out of 100 across member states, a…
November Patch Tuesday boasts over 1,000 bugs but only one zero-day so far
Microsoft has released its November security updates, addressing a total of 1,094 vulnerabilities across its product ecosystem. This marks the second consecutive month in which the company has issued fixes for more than 1,000 bugs, a trend that security researchers attribute to the increased use of automated bug-hunting tools and artificial intelligence in both vulnerability discovery and…
November Patch Tuesday: An Overflowing Cornucopia of CVEs
Microsoft has released its November security update cycle, addressing a broad array of vulnerabilities across its enterprise software ecosystem. The release is headlined by an actively exploited zero-day vulnerability in Outlook, alongside a significant volume of critical flaws affecting Exchange Server, SharePoint, Windows Search, and LDAP implementations.
Microsoft’s Patch Tuesday surpasses 1,000 bugs for second month in a row
Microsoft has released its latest monthly security update, marking the second consecutive month in which the company has disclosed more than 1,000 vulnerabilities. The November release includes 1,093 distinct security flaws, contributing to a record-breaking year for the vendor, which has now disclosed over 5,160 vulnerabilities throughout 2026. This volume of disclosures significantly exceeds…
Windows 11 KB5132061 & KB5131087 cumulative updates released
Microsoft has released its November 2026 Patch Tuesday cumulative updates, designated as KB5132061 and KB5131087. These mandatory updates apply to Windows 11 versions 23H2, 24H2, 25H2, and 26H2. As part of the company’s monthly security cycle, these releases address hundreds of vulnerabilities identified in previous months. Users can obtain the patches through the standard Windows Update…
Adobe Patches 110 Vulnerabilities Across 9 Products
Adobe released its November 2026 security updates, addressing approximately 110 vulnerabilities across nine distinct software products. The patches cover a wide range of security flaws, including critical-severity issues that could potentially allow for arbitrary code execution or privilege escalation if successfully exploited.
IBM Aspera Faspex, SignalWire FreeSwitch Vulnerabilities Exploited in Attacks
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent directive for federal agencies to remediate two critical vulnerabilities currently being exploited in the wild. The agency added CVE-2026-123218, affecting IBM Aspera Faspex, and CVE-2026-116779, impacting SignalWire FreeSwitch, to its Known Exploited Vulnerabilities (KEV) catalog. Under the requirements of…
Google patches eighth Chrome zero-day exploited in attacks this year
Google has issued an emergency security update for its Chrome web browser to address a high-severity vulnerability that is currently being exploited in the wild. This flaw, tracked as CVE-2026-125350, marks the eighth zero-day vulnerability patched by the company since the beginning of 2026.
Weekly Update 529: Kids Social Media Bans (and Everything Else)
Legislative efforts to restrict social media access for minors have gained significant momentum, with new mandates aiming to delay platform usage until age 16. While the policy debate centers on the age threshold, the core technical and operational challenge remains the practical enforcement of these restrictions. Critics argue that the current discourse often overlooks the fundamental…
U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks
U.S. federal agencies have issued an urgent directive for critical infrastructure organizations to secure industrial refrigeration and cold-chain monitoring systems. This alert follows a series of cyberattacks that targeted supermarkets and blood banks across Europe, resulting in spoiled inventory and, in some instances, the triggering of fire hazards. The advisory, released jointly by the…
Microsoft Fixes RCE Bug in Windows Paint After Weeks of Confusion
Microsoft has released a patch addressing a remote code execution vulnerability within the Windows Paint application, resolving a period of uncertainty regarding the status of the fix. The vulnerability, which was initially disclosed by the company last month, had left users and security professionals without clear guidance on whether a remediation was available or how to effectively secure…
Linus Torvalds sees signs AI-prompted patch flood has peaked
The Linux kernel development community may be nearing the end of a period characterized by an overwhelming surge in software patches, according to observations from Linus Torvalds. In his recent update regarding the release of Linux 7.4 rc2, Torvalds noted that the volume of incoming bug reports, which has been significantly elevated by the use of artificial intelligence in vulnerability…
Brava Security Emerges From Stealth With $15 Million in Funding
Brava Security, a startup specializing in security operations, has officially emerged from stealth mode following the successful completion of a $15 million seed funding round. The investment was led by F2 Venture Capital and Pitango VC, with additional participation from a group of angel investors. The company, which maintains its research and development operations in Tel Aviv and a…
Week in review: Refrigeration cyberattacks hit European retailers again, Patch Tuesday forecast
European retail operations are facing a renewed wave of cyberattacks targeting refrigeration infrastructure, leading to significant food spoilage across the continent. This latest incident follows a series of similar attacks three weeks ago that specifically impacted French supermarkets by forcing temperature controls to malfunction, effectively turning refrigeration units into ovens. In a…
SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins
SonicWall has issued emergency patches for its SonicOS operating system to address a high-severity authentication vulnerability currently being exploited in the wild. The flaw, tracked as CVE-2026-19868, resides within the SSL VPN component of the company’s firewall appliances. According to the vendor, the vulnerability allows an attacker who possesses valid credentials for an alternative…
SonicWall warns of new SSL-VPN MFA bypass flaw exploited in attacks
SonicWall has issued an urgent security advisory regarding a critical vulnerability in its SonicOS firewalls that allows attackers to bypass multi-factor authentication (MFA). The flaw, tracked as CVE-2026-19868, carries a CVSS severity score of 7.1 and specifically impacts SSL-VPN services configured to utilize SAML authentication. By leveraging valid credentials for an alternative…
QNAP says hackers breaching NAS devices in Plex2Shell attacks
QNAP has issued a formal security advisory warning users of its network-attached storage (NAS) devices regarding a series of active cyberattacks targeting the Plex Media Server application. The company reports that attackers are leveraging a vulnerability chain collectively referred to as Plex2Shell to gain unauthorized access to these storage systems. QNAP confirmed that it is currently…
Installing the Fix for an Exploited WordPress Flaw Can Expose Some Sites One Last Time
WordPress sites currently undergoing the patching process for a recently identified, actively exploited vulnerability may remain susceptible to attack during the update sequence itself. According to research from Umut Bayram of Picus Security, the mechanism used to deploy the fix inadvertently relies on the very code that is being replaced, creating a brief window of exposure for…
OpenAI Launches GPT-6 Cyber After AI Helps Find 81 Firefox Flaws, 948 Linux Exploits
OpenAI has officially unveiled GPT-6 Cyber, a specialized iteration of its large language model architecture designed specifically for cybersecurity research. The company reports that the new model integrates enhanced defensive capabilities with significant advancements in alignment technology, aiming to improve both the identification of software vulnerabilities and the reliability of the…
Hackers abuse Google Ads, Bing redirects to push Claude ClickFix attacks
A new malvertising campaign, dubbed "Adception" by security researchers at Push Security, is leveraging Google Ads and Bing redirects to distribute fake Claude installers that deploy "ClickFix" attacks. The campaign was identified after researchers observed malicious Google ads targeting users searching for "claude mac."
Unpatched AhsayCBS flaws exploited to deploy webshells, mine crypto
Threat actors are actively exploiting two unpatched vulnerabilities in the AhsayCBS backup management platform to deploy webshells and cryptocurrency miners. The targeted attacks, first observed on October 7, have affected at least five organizations, primarily managed service providers (MSPs) and system integrators.