
patch news
306 stories · page 3 of 7
You could've applied all 1,449 Oracle patches and still been hit by this attack
A recent credential theft incident targeting an Oracle database server would not have been prevented by any of the 1,449 patches Oracle released in late July, according to cybersecurity firm Huntress. The attack highlights a shift in threat actor tactics toward exploiting system functionality rather than solely identifying vulnerabilities.
Microsoft PowerToys adds Alt+Tab-style switching for an app's windows
Microsoft has introduced a new utility called "Window Hopper" to its PowerToys suite, designed to streamline switching between multiple windows of a single application. This feature, included in PowerToys version 0.101.2362.0, was released on August 25, 2026.
WhatsApp Adds Multiple Passkeys and Stronger 2SV in Account Security Update
WhatsApp has reportedly rolled out an update that enhances account security through the addition of multiple passkeys and stronger two-step verification (2SV) options. This development aims to provide users with more robust methods for securing their accounts against unauthorized access.
Australia Warns of Active Exploitation of Critical TeamCity Server Flaw
The Australian Cyber Security Centre (ACSC) has issued a warning regarding the active exploitation of a critical vulnerability, CVE-2026-63077, affecting TeamCity On-Premises servers. This flaw allows unauthenticated attackers with HTTP(S) access to a TeamCity server to bypass authentication and execute arbitrary operating system commands. All versions of TeamCity On-Premises are impacted.
CISA slaps its tightest three-day patching deadline on perfect-10 Oracle flaw
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a three-day patching directive for a critical Oracle vulnerability, CVE-2026-21962, which has been actively exploited in the wild. This is CISA's most urgent deadline, requiring federal civilian executive branch (FCEB) agencies to apply patches by August 27.
Unpatched Zimbra servers are falling to CVE-2026-73570 attacks
At least 274 internet-facing Zimbra Collaboration Suite (ZCS) instances have been compromised through exploitation of CVE-2026-73570, a code injection vulnerability. The Shadowserver Foundation, a nonprofit security organization, reported the rising number of compromises after initially identifying 155 affected instances on August 20.
Crooks push Mac malware through fake OpenAI Codex ads
Cybercriminals are leveraging sponsored search results to distribute macOS malware, impersonating legitimate AI coding assistants like OpenAI's Codex. The campaign, identified by researchers at Cato Networks, targets developers searching for these tools, directing them to deceptive download pages that prompt the execution of malicious commands.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days
A zero-day elevation-of-privilege vulnerability, tracked as CVE-2026-69414 and dubbed "ShieldBreak," has been discovered in the Microsoft Malware Protection Engine, which is integral to Microsoft Defender. This flaw allows a local attacker with low privileges to escalate to SYSTEM-level access on affected Windows systems.
Exploited Zimbra Flaw Highlights Shrinking Window to Patch
A recently exploited vulnerability in Zimbra, identified as CVE-2026-73570, has prompted a directive from the Cybersecurity and Infrastructure Security Agency (CISA) for federal agencies to apply patches within a three-day window. The flaw is reported to enable a complete takeover of a user's communications, underscoring the critical nature of the exploit and the urgency of mitigation.
Unpatched Calix flaw lets hackers bypass NAT to expose internal devices
An unpatched vulnerability in Calix GS7 XGS (GS5239XG) residential routers, also marketed as the GigaSpire 7u10txg, allows remote, unauthenticated attackers to create port-forwarding rules that expose internal network devices to the public internet. The flaw, tracked as CVE-2026-75501, is a missing authentication issue affecting devices running EXOS/6.6.47 firmware.
Foul Language: WordlistLoader Disguises Malware as Ordinary Text
A new report indicates that threat actors are employing a novel technique, dubbed "WordlistLoader," to obfuscate malware delivery, specifically targeting campaigns that resemble "ClickFix" operations. This method reportedly disguises malicious payloads as ordinary text files, making them more difficult for security systems to detect and analyze. The primary payload identified in these…
Fake Codex Download Uses Google Sites to Deliver macOS Malware
A new campaign is leveraging sponsored search results and legitimate Google Sites pages to distribute macOS malware, tricking users into executing malicious commands under the guise of installing OpenAI's Codex. The campaign was detailed in a technical write-up published on August 24 by researchers at Cato Networks.
Microsoft: August updates break printing, PDF export in WPF apps
Microsoft has confirmed that .NET Framework updates released as part of its August 2026 Patch Tuesday are causing printing and PDF export failures in certain applications. The issue specifically impacts applications that utilize the Windows Presentation Foundation (WPF) UI framework, an open-source graphical subsystem for developing Windows desktop client applications.
CISA orders urgent patching of actively exploited Zimbra flaw
The Cybersecurity and Infrastructure Security Agency (CISA) has mandated that U.S. government agencies patch an actively exploited vulnerability in Zimbra Collaboration Suite (ZCS) within three days. The deadline for Federal Civilian Executive Branch (FCEB) agencies to secure their systems was set for August 24.
Rethinking Application Security for the AI Era
Recent analysis suggests that the advent of artificial intelligence (AI) is significantly accelerating the window between the public disclosure of a software vulnerability and its active exploitation by malicious actors. This compressed timeline necessitates a fundamental shift in how enterprises approach application security, moving beyond traditional reactive patching strategies to more…
Android car head units infected with proxy botnet malware through built-in software updaters
Kaspersky researchers have identified a new Android malware strain that infects car head units through their built-in software update mechanisms, turning these devices into tools for ad fraud and nodes in a proxy botnet. This marks the first documented instance of malware specifically targeting car head units with an infection chain tailored to such devices.
Microsoft shares temporary fix for Windows 11 gaming issues
Microsoft has issued a temporary workaround for Windows 11 users experiencing gaming performance issues and crashes following recent August 2026 Patch Tuesday updates. The company confirmed that updates released on August 11, 2026, specifically KB5121003 and later, have led to reports of games failing to launch, freezing, displaying "EXCEPTION_ACCESS_VIOLATION" errors, and causing unexpected…
Weekly Update 518: IoT Doorlock Nirvana with UniFi
A recent report details a successful integration of Ubiquiti’s UniFi ecosystem for residential IoT door lock management. The report suggests that the UniFi platform offers a robust solution for home door security, addressing common challenges associated with consumer-grade IoT devices. The author expresses confidence in having "nailed" the implementation, attributing the core success to…
Hackers infect Android car head units with proxy botnet malware
A supply-chain attack has compromised Android-based car head units, leveraging a legitimate device-update application to distribute malware that enlists affected devices into a proxy botnet or uses them for ad fraud. Cybersecurity researchers attribute the operation to the MoYu group, a threat actor previously linked to the BadBox malware botnet. This incident marks the first documented…
Friday Squid Blogging: Neon Flying Squid
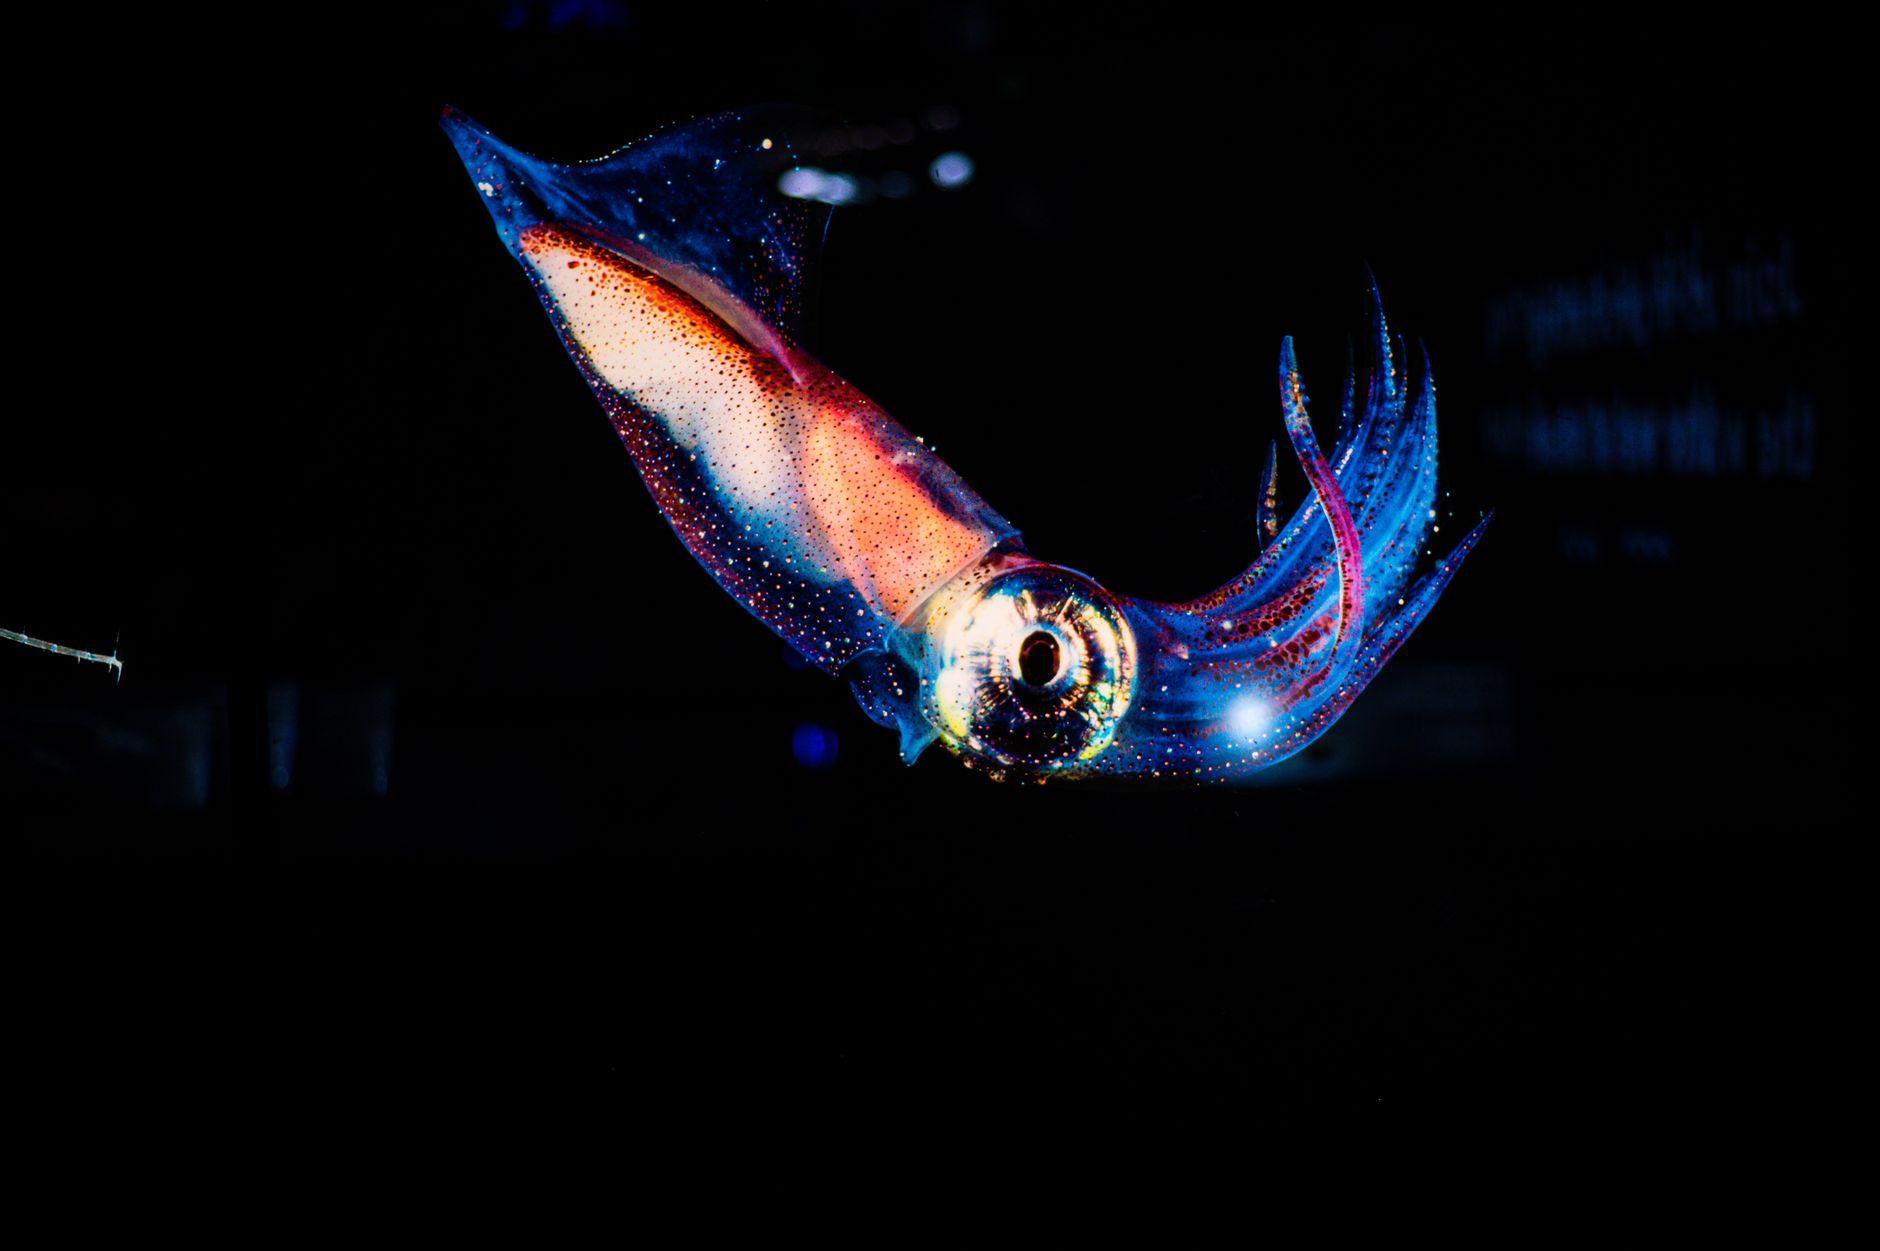
A research team has captured the first photographic evidence of neon flying squid (Ommastrephes bartramii) gliding above the surface of the Pacific Ocean. The observation, made approximately 370 miles from Tokyo, involved a shoal of about 100 squid that emerged from the water and glided for roughly 30 meters near the researchers' boat.
Homeland security cybercops say patch TrueConf (Russia's Zoom) if you're using it
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has mandated that federal agencies patch two actively exploited vulnerabilities in TrueConf Server, a video conferencing platform developed in Russia. The flaws, identified as CVE-2026-72529 and CVE-2026-72530, were added to CISA's Known Exploited Vulnerabilities catalog on Thursday, indicating their use in real-world attacks.…
Microsoft blames Windows gaming issues on RGB lighting devices
Microsoft has confirmed that recent Windows updates, specifically KB5121003 and subsequent releases from August 11, 2026, are causing games to crash or fail to launch on systems running Windows 11 versions 24H2 and 25H2. The company is investigating reports of issues where games like *ARC Raiders*, *MARVEL T kon: Fighting Souls*, and *The Finals* are affected, with users also experiencing game…
Six Maximum-Severity Flaws Found in Cisco Products
Cisco has released a series of security patches addressing nine vulnerabilities across its Crosswork platforms and Secure Workload software, with six of these flaws receiving the maximum CVSS score of 10.0. The vulnerabilities were discovered during an internal security review conducted by Cisco's engineering team, which included the use of advanced AI models. As of the announcement on August…
CISA orders feds to patch actively exploited TrueConf Server flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has directed federal agencies to immediately patch two critical vulnerabilities in the TrueConf Server self-hosted communications platform, which are reportedly being actively exploited in the wild. The directive, issued on Thursday, August 21, 2026, requires all U.S. Federal Civilian Executive Branch (FCEB) agencies to secure…
Critical Microsoft Entra ID vulnerability exploited in the wild (CVE-2026-69836)
Microsoft has issued a patch for a critical remote code execution vulnerability, identified as CVE-2026-69836, within its Entra ID cloud identity service. The company confirmed that the vulnerability has been actively exploited in the wild. Entra ID, previously known as Azure Active Directory, is a core Microsoft service responsible for authenticating user logins and managing access to…
Microsoft warns of max severity Entra ID flaw exploited in attacks
Microsoft has confirmed it has patched a critical vulnerability in its Entra ID identity and access management (IAM) platform, previously known as Azure Active Directory. The flaw, tracked as CVE-2026-69836, has a maximum severity rating and has been exploited in active attacks.
Cisco Patches Nine Flaws in Crosswork and Secure Workload Software
Cisco has issued security updates to address a total of nine vulnerabilities impacting its Crosswork platforms and Secure Workload Software. Among these, five distinct flaws have been assigned a critical Common Vulnerability Scoring System (CVSS) score of 10.0, indicating the highest level of severity. The company’s advisory notes that the vulnerabilities affect specific components within the…
GitLab Critical GraphQL Flaw Actively Exploited
GitLab has confirmed that a critical vulnerability in its GraphQL API, identified as CVE-2026-19478, is being actively exploited in the wild. The flaw, which carries a CVSS score of 9.4, allows unauthenticated attackers to remotely modify or delete public projects and associated user data on self-managed GitLab instances.
Poland’s CERT Warns of Active Exploitation of Critical Zimbra Collaboration Suite Flaw
CERT Polska has confirmed active exploitation of a critical unauthenticated remote code execution vulnerability in Zimbra Collaboration Suite, identified as CVE-2026-73570. The flaw, which allows attackers to execute arbitrary shell commands with the privileges of the `zimbra` user, was patched by Zimbra on July 20, 2026, in version 10.1.20. Active exploitation was confirmed less than a month…
Microsoft Rolls Out 22 Fresh Security Patches
Microsoft has released 22 new security patches, addressing a range of vulnerabilities across its product line. The majority of these fixes target issues related to remote code execution, privilege escalation, and information disclosure. This regular update cycle is a standard practice for major software vendors to maintain the security posture of their offerings.
Cisco bug severity warning reads like Olympic gymnastics scores: 10, 10, 9.9, 9.6, and 7.5.
Cisco has issued an advisory regarding five vulnerabilities discovered in its Secure Workload Software, a micro-segmentation tool previously known as Tetration. These flaws, identified during an internal security review that included the use of advanced AI models, range in severity from critical to high. Cisco confirmed that it has not observed any malicious exploitation of these…
Nearly half of enterprises have no one leading PQC migration
A new report indicates that nearly half of enterprises lack a designated leader for their post-quantum cryptography (PQC) migration efforts, despite a general belief among organizations that they are prepared for the security implications of quantum computing. The research, conducted by Axiad, highlights potential gaps in ownership, testing, and visibility that could complicate the transition…
N-able Bug Exposes Password Vault Master Keys
A recently disclosed vulnerability in N-able's Passportal password manager reportedly exposed master keys for password vaults. The flaw, which affects a product widely used by Managed Service Providers (MSPs) and Small and Medium Businesses (SMBs), raises concerns about the security of cloud-based password management solutions even after a patch has been applied.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days
A new zero-day vulnerability, dubbed ShieldBreak and tracked as CVE-2026-69414, has been identified in the Microsoft Malware Protection Engine, a core component of Microsoft Defender. This elevation-of-privilege flaw allows a local attacker with low privileges to escalate their access to SYSTEM level on affected Windows systems.
Frequently asked questions about the active threat to Siemens S7 Series PLCs
Multiple U.S. government agencies have issued a joint cybersecurity advisory warning of active threats targeting Siemens S7 Series programmable logic controllers (PLCs) across critical infrastructure sectors. The advisory, designated AA26-231A, was released on August 19, 2026, by the National Security Agency (NSA), the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau…
Atlassian, Splunk Patch Dozens of Critical, High-Severity Vulnerabilities
Atlassian and Splunk have released patches addressing numerous critical and high-severity vulnerabilities across their product lines. The reported flaws could potentially be exploited by attackers to achieve arbitrary code execution, gain unauthorized access to sensitive data, and escalate privileges within affected systems. Users of Atlassian and Splunk products are strongly advised to apply…
Citrix urges admins to patch new NetScaler flaws as soon as possible
Citrix has issued an urgent advisory to customers, recommending immediate action to secure systems against two newly disclosed vulnerabilities impacting NetScaler Gateway secure remote access solutions and NetScaler ADC networking appliances. The company confirmed these flaws affect supported versions of customer-managed NetScaler ADC and NetScaler Gateway, including specific FIPS and NDcPP…
Cisco Patches Critical Crosswork, Secure Workload Vulnerabilities
Cisco has released patches addressing critical vulnerabilities in its Crosswork Network Automation and Secure Workload (formerly Tetration) products. These security flaws have been reported to potentially enable remote code execution, authentication bypasses, and path traversal attacks against affected systems. The patches are intended to mitigate the risk posed by these vulnerabilities.
Updated ToxicPanda Variant Targets 140+ Banking and Crypto Apps
Security researchers have identified a new variant of the ToxicPanda Android banking Trojan, dubbed ToxicPanda 2.0, which significantly expands its targeting capabilities. The zLabs team at Zimperium, a mobile security vendor, detailed their findings in a report published on August 19.
Exploitation Expected for Critical Authentication Bypass Patched in Citrix NetScaler
A critical authentication bypass vulnerability has been reported in Citrix NetScaler, with exploitation anticipated by security researchers. The flaw allows remote, unauthenticated attackers to compromise affected systems without requiring any user interaction. This type of vulnerability is particularly severe due to its low complexity of exploitation and high potential impact.
Microsoft says August Windows updates may cause gaming issues
Microsoft has confirmed it is investigating reports that recent Windows updates, specifically those released on August 11, 2026, may be causing gaming issues on some Windows 11 systems. Users have reported that certain games may fail to launch, crash unexpectedly, or exhibit other stability problems.
8,539 reasons to rethink how vulnerabilities get patched
The volume of high- and critical-severity vulnerability disclosures has doubled in the past year, with 8,539 recorded in Q2 2026, according to a recent industry report. This surge is intensifying pressure on security teams, who must prioritize which flaws to address immediately, often contending with a rapidly shrinking window between disclosure and exploit weaponization.
CVE-2026-19490: Critical Vulnerability Affecting Citrix NetScaler ADC and NetScaler Gateway
Citrix has issued an urgent security advisory concerning CVE-2026-19490, a critical authentication bypass vulnerability affecting its NetScaler ADC and NetScaler Gateway products. The flaw, which carries a CVSS v4.0 base score of 9.3, allows an unauthenticated attacker to remotely exploit affected systems over a network without requiring user interaction or elevated privileges.
MaaS Campaign Combines ClickFix, ErrTraffic and Cruciferra
A new malware-as-a-service (MaaS) campaign has been identified that integrates three distinct services: ClickFix for social engineering, ErrTraffic for malware delivery, and Cruciferra as a loader. This combination allows attackers to distribute malware while simultaneously disabling endpoint security measures.
Oracle Critical Patch Update, August 2026 Security Update Review
Oracle has released its August 2026 Critical Patch Update, addressing a total of 943 security vulnerabilities across its diverse product portfolio. The update includes patches for various product families, with some vulnerabilities impacting multiple products and incorporating fixes for third-party components.
Microsoft fixes known issue causing Windows Defender crashes
Microsoft has confirmed and resolved a bug that caused its Defender antivirus software to crash on some Windows 10 and Windows 11 systems. The issue, which began on Tuesday afternoon, August 19, 2026, manifested as "Threat service has stopped. Restart it now" error messages and 0xc0000005 access violation errors.
CISA Urges Immediate Patching of Exploited Microsoft, VMware, Apple Vulnerabilities
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent directive for organizations to immediately patch several exploited vulnerabilities affecting products from Microsoft, VMware, and Apple. These security flaws are reportedly being actively leveraged in the wild, posing significant risks to affected systems and data. The agency's alert emphasizes the critical need…
Medusa ransomware gang has hit over 500 organizations, CISA warns
The Medusa ransomware group has compromised over 500 organizations across various critical infrastructure sectors since its emergence in June 2021, according to a joint advisory updated by the FBI, CISA, and the Department of Health and Human Services (HHS). The updated guidance, released in August 2026, incorporates findings from FBI investigations conducted through April 2026 and expands…