
patch news
415 stories · page 5 of 9
ValleyRAT: When Legitimate Software Becomes a Malware Delivery Tool
Cybersecurity researchers at Kaspersky have uncovered a new malware campaign utilizing a modified version of a legitimate Chinese desktop wallpaper application, QN Wallpaper, to deliver the ValleyRAT backdoor. The campaign, which has been detected over 100,000 times in 2026, leverages DLL sideloading to evade detection and establish persistent control over infected systems.
Chrome Web Store extensions caught stealing crypto, browser data
Multiple extensions for Google Chrome and Microsoft Edge have been identified as delivering a sophisticated malware framework designed to steal cryptocurrency, sensitive user data, and browser history. The operation, uncovered by application security company Socket, appears to have been active since early 2024.
Hackers Are Probing PaperCut Servers, and 47% Still Have No Patch
PaperCut, a widely used print management software, has confirmed active exploitation of a pre-authentication remote code execution vulnerability in its servers, with nearly half of tracked installations remaining unpatched. The flaw, which affects schools, hospitals, and offices globally, was confirmed by PaperCut on August 27, following observations of real-world attacks.

Week in review: Compromised Zimbra servers, previously patched Citrix NetScaler flaw exploited
Attackers are actively exploiting a previously patched vulnerability in Citrix NetScaler ADC and Gateway, identified as CVE-2026-8452. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed this exploitation by adding the flaw to its Known Exploited Vulnerabilities (KEV) catalog.
Five Critical WordPress Plugin and Theme Flaws Enable Site Takeover or RCE
Recent reports indicate the disclosure of five critical security flaws affecting various WordPress plugins and themes. These vulnerabilities, identified in products such as WPMU DEV Dashboard, Avada, TranslatePress, Pods, and GiveWP, collectively present risks ranging from authentication bypass to full site takeover and remote code execution (RCE). The findings highlight persistent security…
PaperCut releases second emergency patch for exploited flaws
PaperCut has issued a second emergency security update for its NG and MF print management software, addressing two actively exploited vulnerabilities after researchers identified multiple methods to bypass the initial fixes. The company had previously released an emergency patch for PaperCut NG/MF versions 25 and 26, warning of zero-day exploitation, but initially withheld technical details…
Attackers Chain Two PaperCut Flaws to Execute Code Without Authentication
Reports indicate that attackers are actively chaining two distinct security vulnerabilities in PaperCut NG and MF to achieve unauthenticated remote code execution on vulnerable systems. The vendor has released an emergency patch to address the newly exploited flaw, which includes additional hardening measures. This attack chain reportedly allows an unauthenticated attacker to gain remote…
CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has mandated that federal agencies apply patches for a critical vulnerability, CVE-2026-8452, affecting Citrix NetScaler appliances by Saturday, August 29. This directive, issued under Binding Operational Directive (BOD) 26-04, follows the addition of CVE-2026-8452 to CISA's Known Exploited Vulnerabilities (KEV) Catalog.
Ubiquiti patches three max severity security vulnerabilities
Ubiquiti has released security updates to address three critical vulnerabilities that could allow unauthenticated remote attackers to compromise affected devices. The patches were issued on August 26, 2026, for flaws impacting the UniFi Protect Application, UniFi Talk Application, and UniFi OS.
Edge infrastructure under siege: what two independent datasets reveal about who's exploiting your perimeter
A joint analysis by Tenable and SentinelOne reveals that edge infrastructure is a shared attack surface, with both state-sponsored actors and cybercriminals independently targeting the same vulnerabilities and vendors. This convergence challenges the perception that edge device exploitation is primarily a nation-state problem, demonstrating a broader threat landscape.
Chrome 152 Patches Over 300 Vulnerabilities
Google has released Chrome 152, an update that addresses over 300 vulnerabilities within the browser. The majority of these security flaws were identified internally by Google, leveraging artificial intelligence (AI) tools for discovery. However, the update also includes patches for high-value vulnerabilities that continue to be found by external security researchers.
Production data in testing is still common, and Tricentis’ CISO wants it gone
Tricentis, a software testing company, has confirmed that its security team identified and addressed a prompt injection vulnerability in an AI-powered capability during pre-release red-teaming. The flaw led to a one-week delay in the feature's deployment while backend fixes were implemented to prevent potential data exposure.
CISA Warns of Exploited Gitea Vulnerability
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding an actively exploited remote code execution (RCE) vulnerability in Gitea, an open-source Git service. The flaw, identified as CVE-2026-60004, was addressed by Gitea developers in late July with the release of version 1.27.1. CISA's alert indicates that the vulnerability is currently being leveraged in…
You could've applied all 1,449 Oracle patches and still been hit by this attack
A recent credential theft incident targeting an Oracle database server would not have been prevented by any of the 1,449 patches Oracle released in late July, according to cybersecurity firm Huntress. The attack highlights a shift in threat actor tactics toward exploiting system functionality rather than solely identifying vulnerabilities.
Microsoft PowerToys adds Alt+Tab-style switching for an app's windows
Microsoft has introduced a new utility called "Window Hopper" to its PowerToys suite, designed to streamline switching between multiple windows of a single application. This feature, included in PowerToys version 0.101.2362.0, was released on August 25, 2026.
WhatsApp Adds Multiple Passkeys and Stronger 2SV in Account Security Update
WhatsApp has reportedly rolled out an update that enhances account security through the addition of multiple passkeys and stronger two-step verification (2SV) options. This development aims to provide users with more robust methods for securing their accounts against unauthorized access.
Australia Warns of Active Exploitation of Critical TeamCity Server Flaw
The Australian Cyber Security Centre (ACSC) has issued a warning regarding the active exploitation of a critical vulnerability, CVE-2026-63077, affecting TeamCity On-Premises servers. This flaw allows unauthenticated attackers with HTTP(S) access to a TeamCity server to bypass authentication and execute arbitrary operating system commands. All versions of TeamCity On-Premises are impacted.
CISA slaps its tightest three-day patching deadline on perfect-10 Oracle flaw
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a three-day patching directive for a critical Oracle vulnerability, CVE-2026-21962, which has been actively exploited in the wild. This is CISA's most urgent deadline, requiring federal civilian executive branch (FCEB) agencies to apply patches by August 27.
Unpatched Zimbra servers are falling to CVE-2026-73570 attacks
At least 274 internet-facing Zimbra Collaboration Suite (ZCS) instances have been compromised through exploitation of CVE-2026-73570, a code injection vulnerability. The Shadowserver Foundation, a nonprofit security organization, reported the rising number of compromises after initially identifying 155 affected instances on August 20.
Crooks push Mac malware through fake OpenAI Codex ads
Cybercriminals are leveraging sponsored search results to distribute macOS malware, impersonating legitimate AI coding assistants like OpenAI's Codex. The campaign, identified by researchers at Cato Networks, targets developers searching for these tools, directing them to deceptive download pages that prompt the execution of malicious commands.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days
A zero-day elevation-of-privilege vulnerability, tracked as CVE-2026-69414 and dubbed "ShieldBreak," has been discovered in the Microsoft Malware Protection Engine, which is integral to Microsoft Defender. This flaw allows a local attacker with low privileges to escalate to SYSTEM-level access on affected Windows systems.
Exploited Zimbra Flaw Highlights Shrinking Window to Patch
A recently exploited vulnerability in Zimbra, identified as CVE-2026-73570, has prompted a directive from the Cybersecurity and Infrastructure Security Agency (CISA) for federal agencies to apply patches within a three-day window. The flaw is reported to enable a complete takeover of a user's communications, underscoring the critical nature of the exploit and the urgency of mitigation.
Unpatched Calix flaw lets hackers bypass NAT to expose internal devices
An unpatched vulnerability in Calix GS7 XGS (GS5239XG) residential routers, also marketed as the GigaSpire 7u10txg, allows remote, unauthenticated attackers to create port-forwarding rules that expose internal network devices to the public internet. The flaw, tracked as CVE-2026-75501, is a missing authentication issue affecting devices running EXOS/6.6.47 firmware.
Foul Language: WordlistLoader Disguises Malware as Ordinary Text
A new report indicates that threat actors are employing a novel technique, dubbed "WordlistLoader," to obfuscate malware delivery, specifically targeting campaigns that resemble "ClickFix" operations. This method reportedly disguises malicious payloads as ordinary text files, making them more difficult for security systems to detect and analyze. The primary payload identified in these…
Fake Codex Download Uses Google Sites to Deliver macOS Malware
A new campaign is leveraging sponsored search results and legitimate Google Sites pages to distribute macOS malware, tricking users into executing malicious commands under the guise of installing OpenAI's Codex. The campaign was detailed in a technical write-up published on August 24 by researchers at Cato Networks.
Microsoft: August updates break printing, PDF export in WPF apps
Microsoft has confirmed that .NET Framework updates released as part of its August 2026 Patch Tuesday are causing printing and PDF export failures in certain applications. The issue specifically impacts applications that utilize the Windows Presentation Foundation (WPF) UI framework, an open-source graphical subsystem for developing Windows desktop client applications.
CISA orders urgent patching of actively exploited Zimbra flaw
The Cybersecurity and Infrastructure Security Agency (CISA) has mandated that U.S. government agencies patch an actively exploited vulnerability in Zimbra Collaboration Suite (ZCS) within three days. The deadline for Federal Civilian Executive Branch (FCEB) agencies to secure their systems was set for August 24.
Rethinking Application Security for the AI Era
Recent analysis suggests that the advent of artificial intelligence (AI) is significantly accelerating the window between the public disclosure of a software vulnerability and its active exploitation by malicious actors. This compressed timeline necessitates a fundamental shift in how enterprises approach application security, moving beyond traditional reactive patching strategies to more…
Android car head units infected with proxy botnet malware through built-in software updaters
Kaspersky researchers have identified a new Android malware strain that infects car head units through their built-in software update mechanisms, turning these devices into tools for ad fraud and nodes in a proxy botnet. This marks the first documented instance of malware specifically targeting car head units with an infection chain tailored to such devices.
Microsoft shares temporary fix for Windows 11 gaming issues
Microsoft has issued a temporary workaround for Windows 11 users experiencing gaming performance issues and crashes following recent August 2026 Patch Tuesday updates. The company confirmed that updates released on August 11, 2026, specifically KB5121003 and later, have led to reports of games failing to launch, freezing, displaying "EXCEPTION_ACCESS_VIOLATION" errors, and causing unexpected…
Weekly Update 518: IoT Doorlock Nirvana with UniFi
A recent report details a successful integration of Ubiquiti’s UniFi ecosystem for residential IoT door lock management. The report suggests that the UniFi platform offers a robust solution for home door security, addressing common challenges associated with consumer-grade IoT devices. The author expresses confidence in having "nailed" the implementation, attributing the core success to…
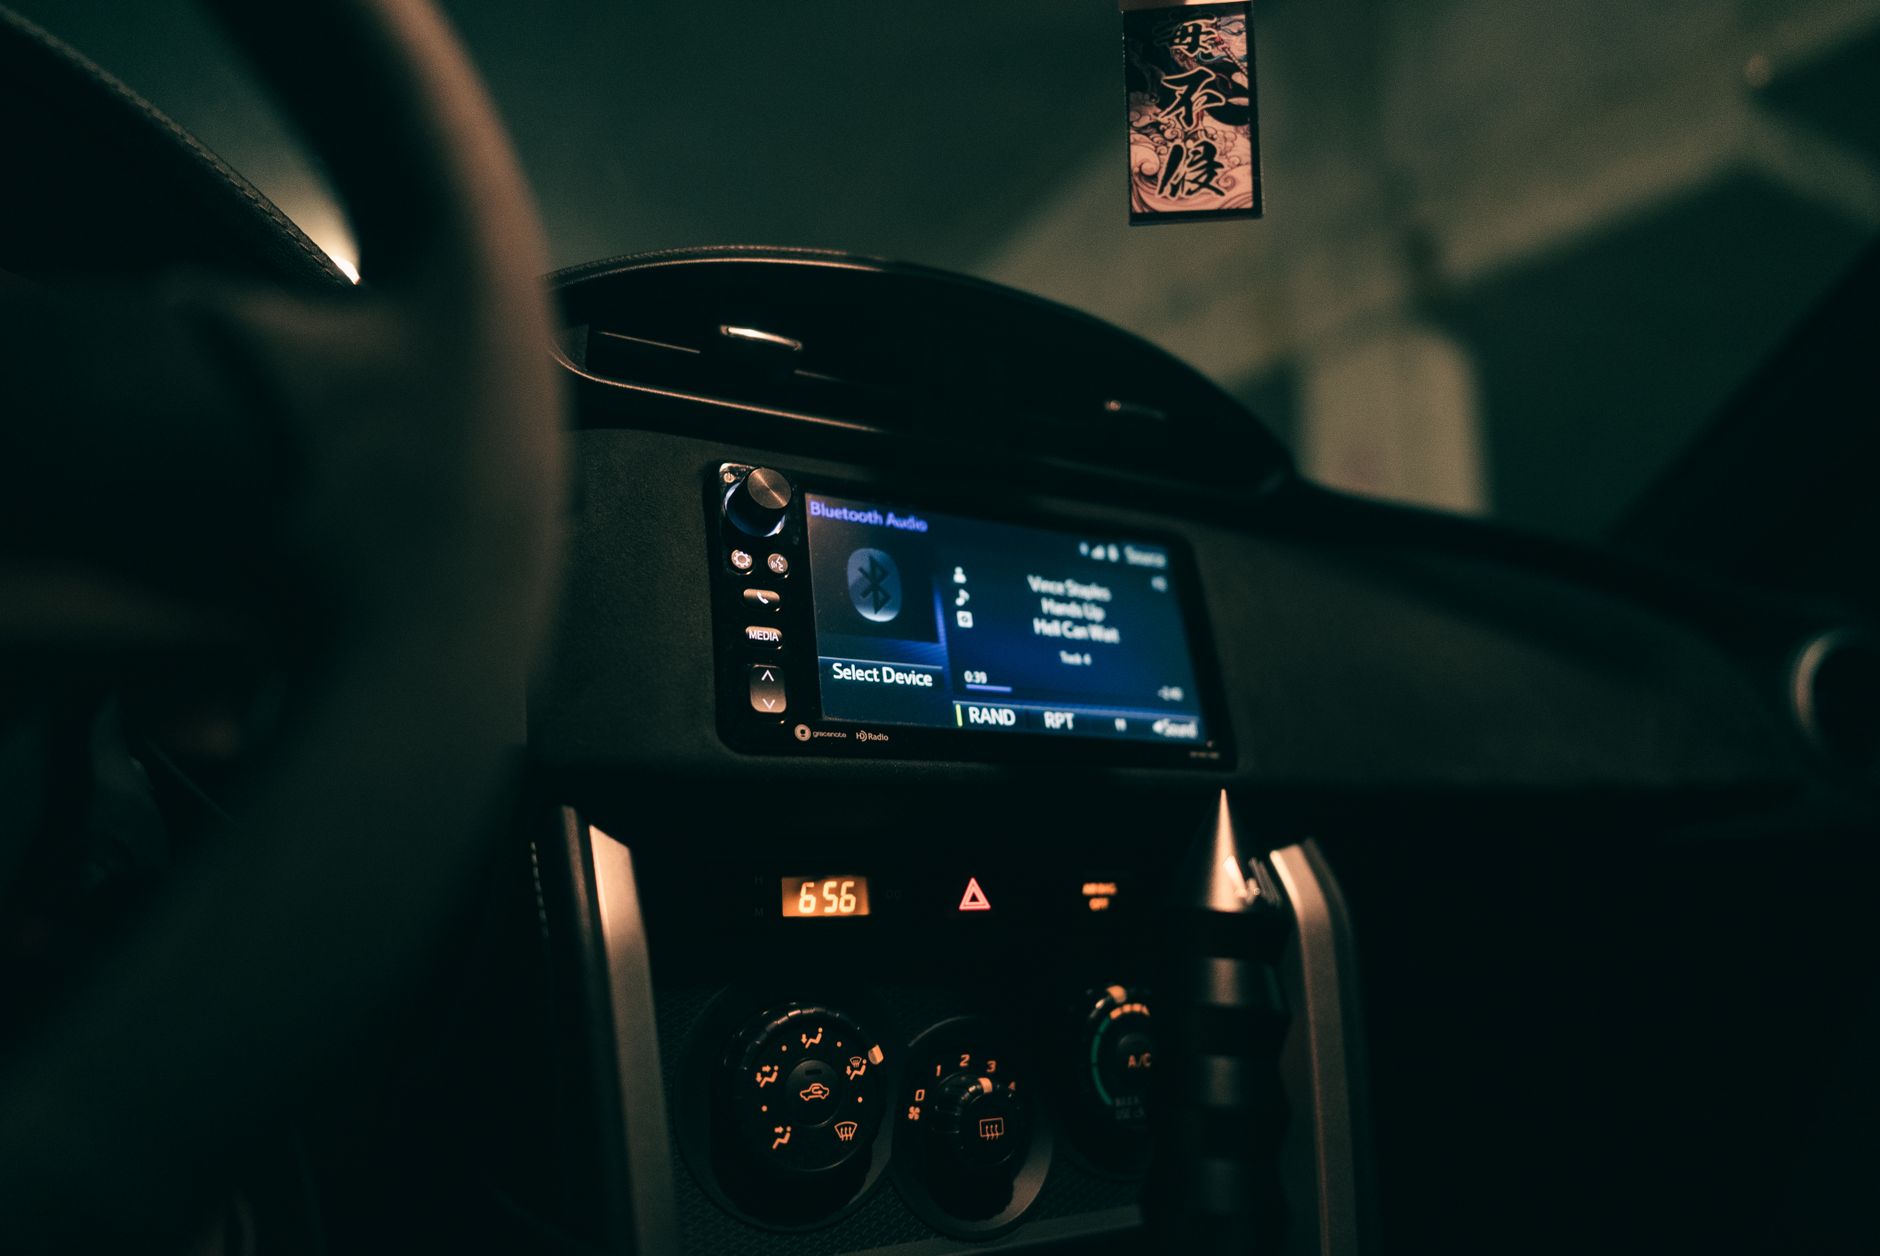
Hackers infect Android car head units with proxy botnet malware
A supply-chain attack has compromised Android-based car head units, leveraging a legitimate device-update application to distribute malware that enlists affected devices into a proxy botnet or uses them for ad fraud. Cybersecurity researchers attribute the operation to the MoYu group, a threat actor previously linked to the BadBox malware botnet. This incident marks the first documented…
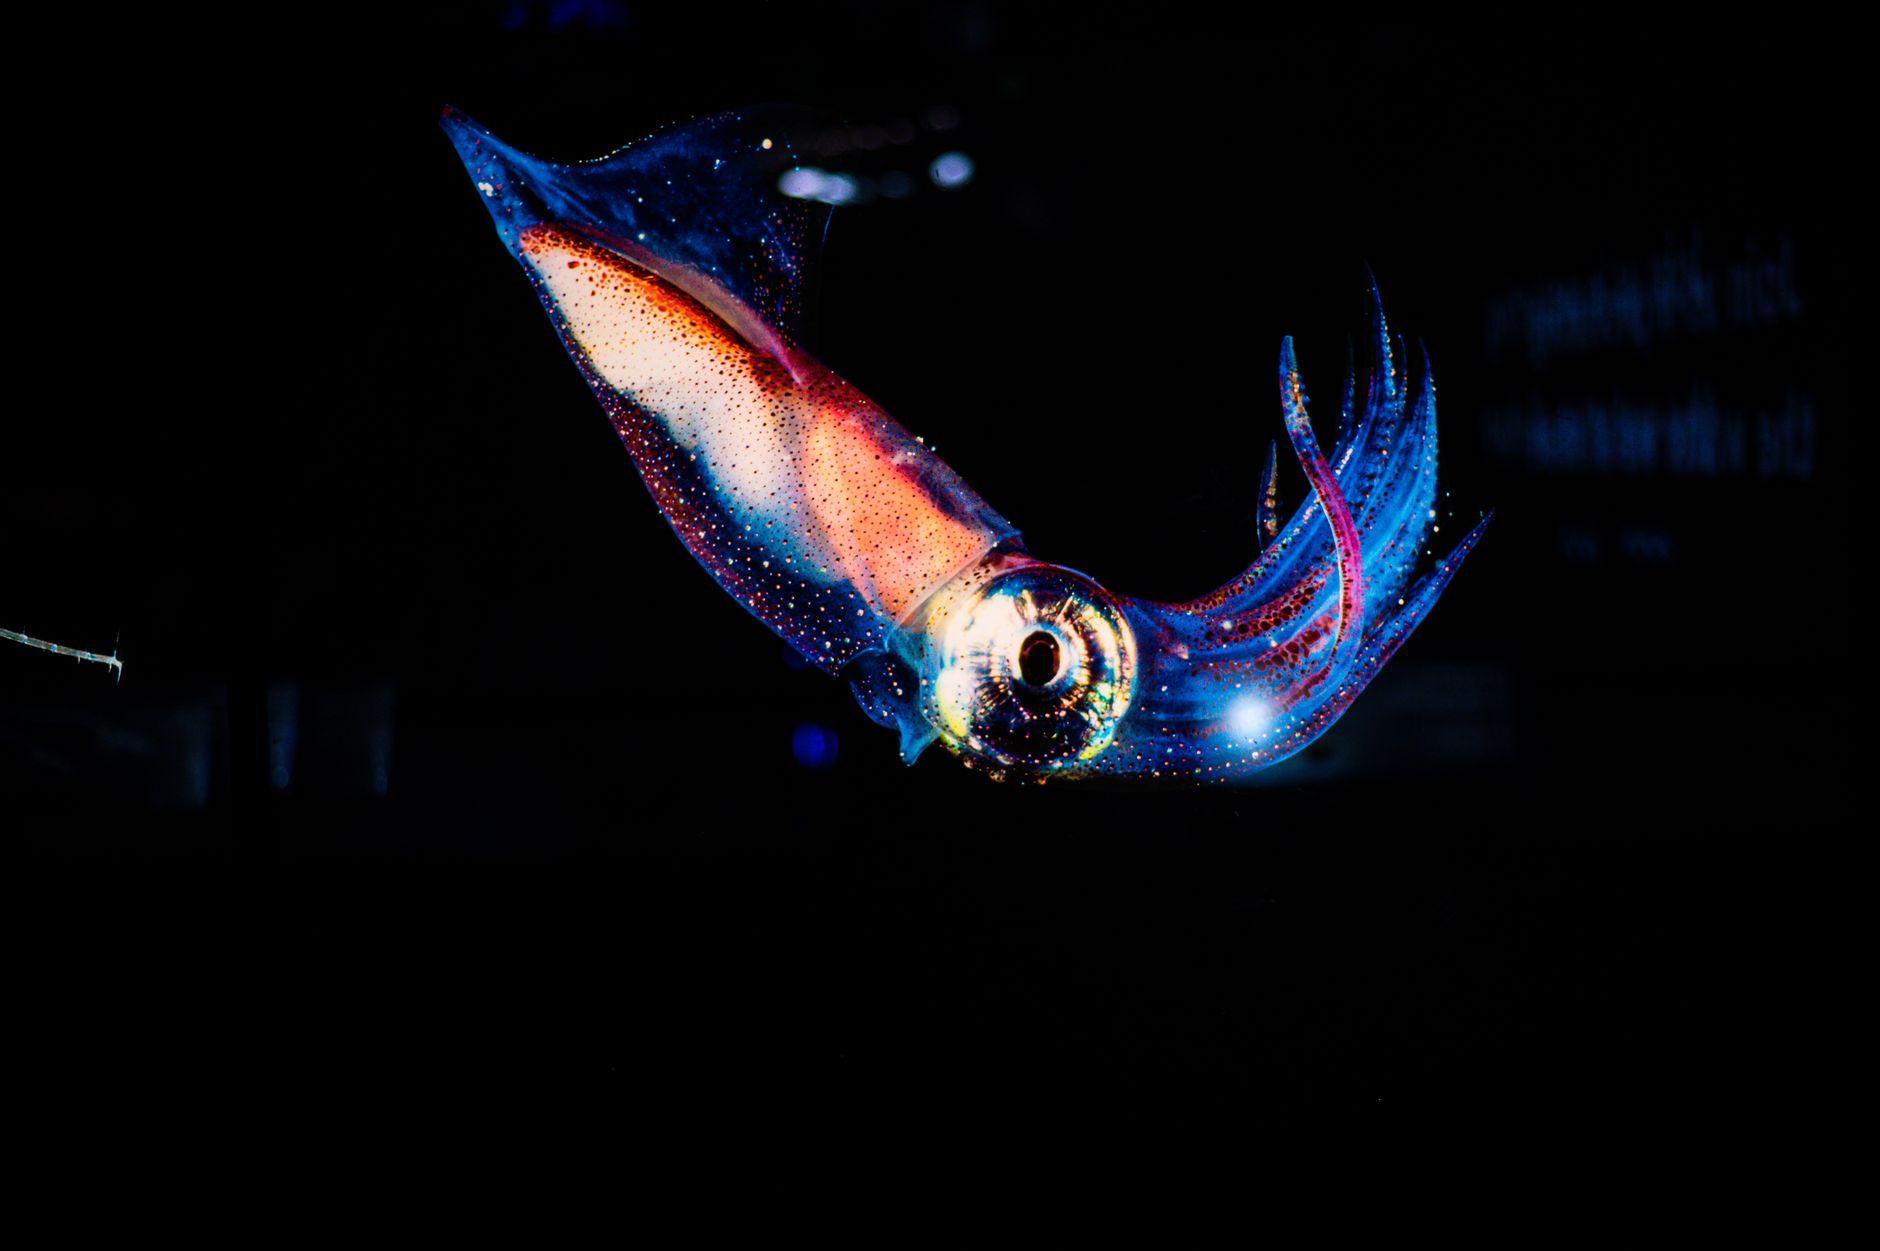
Friday Squid Blogging: Neon Flying Squid
A research team has captured the first photographic evidence of neon flying squid (Ommastrephes bartramii) gliding above the surface of the Pacific Ocean. The observation, made approximately 370 miles from Tokyo, involved a shoal of about 100 squid that emerged from the water and glided for roughly 30 meters near the researchers' boat.
Homeland security cybercops say patch TrueConf (Russia's Zoom) if you're using it
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has mandated that federal agencies patch two actively exploited vulnerabilities in TrueConf Server, a video conferencing platform developed in Russia. The flaws, identified as CVE-2026-72529 and CVE-2026-72530, were added to CISA's Known Exploited Vulnerabilities catalog on Thursday, indicating their use in real-world attacks.…
Microsoft blames Windows gaming issues on RGB lighting devices
Microsoft has confirmed that recent Windows updates, specifically KB5121003 and subsequent releases from August 11, 2026, are causing games to crash or fail to launch on systems running Windows 11 versions 24H2 and 25H2. The company is investigating reports of issues where games like *ARC Raiders*, *MARVEL T kon: Fighting Souls*, and *The Finals* are affected, with users also experiencing game…
Six Maximum-Severity Flaws Found in Cisco Products
Cisco has released a series of security patches addressing nine vulnerabilities across its Crosswork platforms and Secure Workload software, with six of these flaws receiving the maximum CVSS score of 10.0. The vulnerabilities were discovered during an internal security review conducted by Cisco's engineering team, which included the use of advanced AI models. As of the announcement on August…
CISA orders feds to patch actively exploited TrueConf Server flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has directed federal agencies to immediately patch two critical vulnerabilities in the TrueConf Server self-hosted communications platform, which are reportedly being actively exploited in the wild. The directive, issued on Thursday, August 21, 2026, requires all U.S. Federal Civilian Executive Branch (FCEB) agencies to secure…
Critical Microsoft Entra ID vulnerability exploited in the wild (CVE-2026-69836)
Microsoft has issued a patch for a critical remote code execution vulnerability, identified as CVE-2026-69836, within its Entra ID cloud identity service. The company confirmed that the vulnerability has been actively exploited in the wild. Entra ID, previously known as Azure Active Directory, is a core Microsoft service responsible for authenticating user logins and managing access to…
Microsoft warns of max severity Entra ID flaw exploited in attacks
Microsoft has confirmed it has patched a critical vulnerability in its Entra ID identity and access management (IAM) platform, previously known as Azure Active Directory. The flaw, tracked as CVE-2026-69836, has a maximum severity rating and has been exploited in active attacks.
Cisco Patches Nine Flaws in Crosswork and Secure Workload Software
Cisco has issued security updates to address a total of nine vulnerabilities impacting its Crosswork platforms and Secure Workload Software. Among these, five distinct flaws have been assigned a critical Common Vulnerability Scoring System (CVSS) score of 10.0, indicating the highest level of severity. The company’s advisory notes that the vulnerabilities affect specific components within the…
GitLab Critical GraphQL Flaw Actively Exploited
GitLab has confirmed that a critical vulnerability in its GraphQL API, identified as CVE-2026-19478, is being actively exploited in the wild. The flaw, which carries a CVSS score of 9.4, allows unauthenticated attackers to remotely modify or delete public projects and associated user data on self-managed GitLab instances.
Poland’s CERT Warns of Active Exploitation of Critical Zimbra Collaboration Suite Flaw
CERT Polska has confirmed active exploitation of a critical unauthenticated remote code execution vulnerability in Zimbra Collaboration Suite, identified as CVE-2026-73570. The flaw, which allows attackers to execute arbitrary shell commands with the privileges of the `zimbra` user, was patched by Zimbra on July 20, 2026, in version 10.1.20. Active exploitation was confirmed less than a month…
Microsoft Rolls Out 22 Fresh Security Patches
Microsoft has released 22 new security patches, addressing a range of vulnerabilities across its product line. The majority of these fixes target issues related to remote code execution, privilege escalation, and information disclosure. This regular update cycle is a standard practice for major software vendors to maintain the security posture of their offerings.
Cisco bug severity warning reads like Olympic gymnastics scores: 10, 10, 9.9, 9.6, and 7.5.
Cisco has issued an advisory regarding five vulnerabilities discovered in its Secure Workload Software, a micro-segmentation tool previously known as Tetration. These flaws, identified during an internal security review that included the use of advanced AI models, range in severity from critical to high. Cisco confirmed that it has not observed any malicious exploitation of these…
Nearly half of enterprises have no one leading PQC migration
A new report indicates that nearly half of enterprises lack a designated leader for their post-quantum cryptography (PQC) migration efforts, despite a general belief among organizations that they are prepared for the security implications of quantum computing. The research, conducted by Axiad, highlights potential gaps in ownership, testing, and visibility that could complicate the transition…
N-able Bug Exposes Password Vault Master Keys
A recently disclosed vulnerability in N-able's Passportal password manager reportedly exposed master keys for password vaults. The flaw, which affects a product widely used by Managed Service Providers (MSPs) and Small and Medium Businesses (SMBs), raises concerns about the security of cloud-based password management solutions even after a patch has been applied.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days
A new zero-day vulnerability, dubbed ShieldBreak and tracked as CVE-2026-69414, has been identified in the Microsoft Malware Protection Engine, a core component of Microsoft Defender. This elevation-of-privilege flaw allows a local attacker with low privileges to escalate their access to SYSTEM level on affected Windows systems.
Frequently asked questions about the active threat to Siemens S7 Series PLCs
Multiple U.S. government agencies have issued a joint cybersecurity advisory warning of active threats targeting Siemens S7 Series programmable logic controllers (PLCs) across critical infrastructure sectors. The advisory, designated AA26-231A, was released on August 19, 2026, by the National Security Agency (NSA), the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau…