
breach news
295 stories · page 7 of 7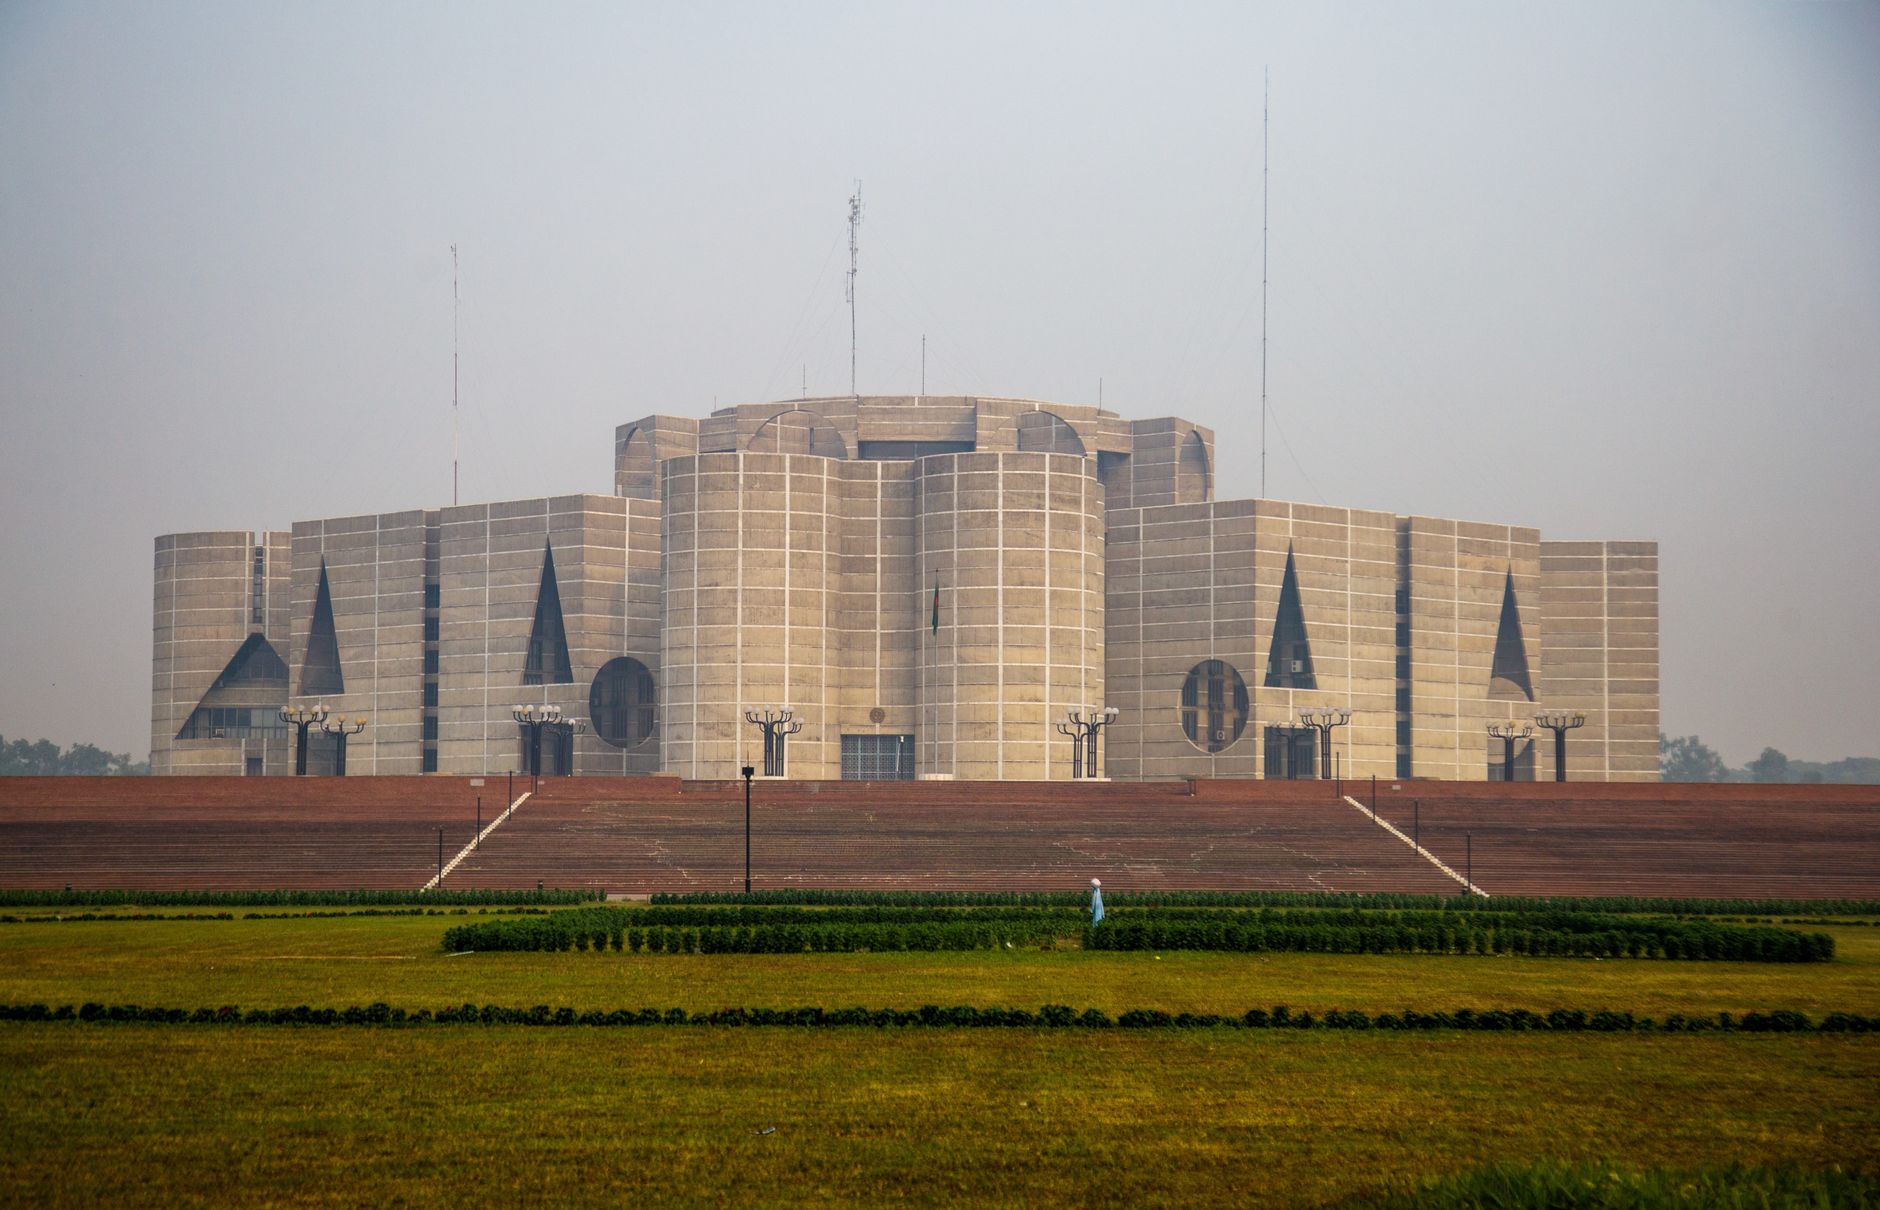
Welcoming the Bangladesh Government to Have I Been Pwned
The government of Bangladesh has joined a growing list of nations utilizing the Have I Been Pwned (HIBP) service to enhance its cybersecurity posture. The BGD e-GOV CIRT department has been granted full access to HIBP's free government service, enabling them to monitor their official domains against data breaches.
Weekly Update 503
Instructure, the company behind the Canvas learning management system, has not yet publicly addressed a potential data breach, despite a deadline set by a ransomware group known as ShinyHunters. The group had threatened to leak data allegedly stolen from Instructure by November 20th.
A Deep Dive into the GetProcessHandleFromHwnd API
The GetProcessHandleFromHwnd API, a Windows function that allows an application to obtain a handle to the process owning a specific window handle (HWND), has undergone significant changes since its introduction, with its original documentation containing several inaccuracies. Initially believed to be a convenience function relying on window hooks, its implementation and security properties…
Bypassing Administrator Protection by Abusing UI Access
A security researcher has detailed multiple vulnerabilities in Windows' User Account Control (UAC) system, specifically concerning the "UI Access" feature, which were present even before the introduction of Administrator Protection. These bypasses, totaling nine discovered by James Forshaw, have since been addressed by Microsoft. This article focuses on five of these issues, stemming from the…
Breaking the Sound Barrier, Part II: Exploiting CVE-2024-54529
A type confusion vulnerability in Apple's CoreAudio framework, identified as CVE-2024-54529, has been successfully exploited by a Google security engineer. The vulnerability resides within the `coreaudiod` system daemon, specifically in the `com.apple.audio.audiohald` Mach service. Researchers discovered that certain message handlers within this service would retrieve an object from an…
A 0-click exploit chain for the Pixel 9 Part 2: Cracking the Sandbox with a Big Wave
A security researcher has identified a critical vulnerability in the Linux kernel used by Google Pixel devices, specifically affecting the BigWave hardware accelerator. This flaw, if exploited, could allow an attacker to escape the restricted "mediacodec" sandbox and gain arbitrary read and write capabilities within the kernel. The vulnerability was discovered by Seth Jenkins, who detailed his…
A 0-click exploit chain for the Pixel 9 Part 1: Decoding Dolby
Google's Pixel 9 devices are susceptible to a zero-click exploit chain that targets the Dolby Unified Decoder (UDC), a component responsible for processing Dolby Digital and Dolby Digital Plus audio formats. This vulnerability allows for arbitrary code execution within the mediacodec context of the device, forming the first stage of a more complex attack. The exploit chain was developed by…