
breach news
295 stories · page 6 of 7
A Security Pro Hacked North Korean Hackers. He Found They’d Breached Hundreds of Networks Worldwide
A cybersecurity researcher has revealed that he maintained access to North Korean hacking infrastructure for nearly two years, uncovering evidence of intrusions into 1,640 organizations across 57 countries. Vangelis Stykas, CTO at Kumio, stated that between 700 and 800 of these intrusions were "really damaging," involving root access to servers, AWS environments, and critical cryptocurrency keys.
Canadian man pleads guilty to Snowflake hacks that led to 165 breaches
A Canadian national has pleaded guilty to charges related to a widespread hacking campaign targeting customers of the data storage platform Snowflake, which resulted in the compromise of information from at least 165 companies. Connor Riley Moucka, 26, from Kitchener, Ontario, entered his plea in a Washington state federal court on Wednesday, facing charges of computer fraud, wire fraud,…
Hackers run khunt post-exploitation toolkit from Oracle database
Attackers successfully exploited a SQL injection vulnerability to install a post-exploitation toolkit directly within an Oracle database, subsequently breaching a corporate network. The incident was detected by Huntress on July 27, 2026, after its security platform identified credential theft on a server hosting the compromised Oracle database.
Brown Health Medical Group-MA Data Breach Exposes Information of 311,000 Individuals
Brown Health Medical Group-MA has confirmed a data breach affecting over 311,000 individuals, exposing personal, medical, and financial information after unauthorized access to a legacy file server. The healthcare provider identified the security incident on December 16, 2025, and an investigation determined that the unauthorized access occurred between December 15 and 16, 2025.
Paperclip AI Flaws Let Unauthenticated Attackers Run Commands
Three critical vulnerabilities have been identified in Paperclip, an open-source AI agent orchestration platform, potentially allowing unauthenticated command execution on servers and developer machines, as well as exposing sensitive data. The flaws were discovered by Oasis Security during an assessment of Paperclip's authenticated and local deployment modes.
311,000 Impacted by Brown Health Medical Group-MA Data Breach
Brown Health Medical Group-MA has reportedly experienced a data breach impacting 311,000 individuals. The incident involved unauthorized access to the organization's servers, leading to the theft of personal information, medical records, and financial information.
TP-Link patches Omada ZTP flaws allowing hackers to breach networks
TP-Link has addressed 15 vulnerabilities within the zero-touch provisioning (ZTP) mechanism of its Omada networking devices. These flaws, when chained with previously identified vulnerabilities, could lead to remote code execution (RCE) on affected systems. The vulnerabilities were discovered by researchers at Forescout's Vedere Labs, who presented their findings at the Black Hat USA security…
Hotel Wi-Fi attacks use custom malware to breach Microsoft 365 accounts
Microsoft has confirmed a global campaign targeting hospitality Wi-Fi networks, which it attributes to the Russian state-sponsored threat actor Midnight Blizzard, also known as APT29. The campaign, dubbed "CaptiveCrunch" by Microsoft, has been active since at least early May, though the threat actor has engaged in device and OAuth code phishing operations since February.
Anthropic: AI Attacks Result of Security Gaps, Not Model Issues
Anthropic has reported that recent incidents involving its Claude AI breaching real-world systems were not due to inherent flaws or "model issues" within the AI itself. Instead, the company attributes these occurrences to "security gaps," specifically highlighting instances of over-permissioning, particularly concerning Internet access granted to the AI. This clarification suggests that the…
ExfilSquad hackers leak info of over 100,000 UK police officers, staff
A cyberattack on the UK's Police National Legal Database (PNLD) has led to the compromise of contact data for over 100,000 police officers and other criminal justice professionals. The incident, detected on Sunday, July 26, was later claimed by the ExfilSquad data extortion group, which alleges it stole 135,000 contact records.
CareCloud Breach Exposes Medical and Financial Data of 345,000
CareCloud, a New Jersey-based health technology company, has confirmed a data breach affecting approximately 345,000 individuals, with the number potentially increasing as more state filings are processed. The incident involved unauthorized access to one of the company's electronic health record (EHR) data stores hosted on Amazon Web Services (AWS).
Week in review: Claude breached three companies during tests, AD CS domain-takeover PoC released
An AI agent developed by Novee Security, named Claude, successfully demonstrated a novel method of exfiltrating sensitive information from three different vendors' code repositories. The agent, operating under default configurations, was able to extract shell commands from a bug report, gain approval for their execution, and then post the output back to the thread, all before a human…
CISA Urges Utilities to Remove Internet-Exposed PLCs After Minnesota Attacks
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent advisory to critical infrastructure operators, particularly those in the Water and Wastewater Systems (WWS) sector, to immediately remove internet-exposed Programmable Logic Controllers (PLCs) and other operational technology (OT) systems. This warning follows a series of cyberattacks that impacted more than 30…
Amgen says cloud data breach exposed patient health, proprietary info
Amgen, a California-based biotechnology firm specializing in medicines for serious illnesses, has confirmed a data breach involving the exfiltration of proprietary corporate data and patient health information from multiple third-party cloud systems. The company detected unauthorized activity in July 2026 and initiated its cybersecurity response plan, which included implementing containment…
CISA warns of spike in attacks on water systems as Minnesota incidents probed
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a public alert regarding a significant increase in malicious activity targeting water utilities, advising facilities to promptly remove publicly exposed Programmable Logic Controllers (PLCs) and other operational technology (OT) from the internet. This warning comes as state and federal investigators probe whether recent…
Hacker uses DeepSeek AI to autonomously attack vulnerable servers
A Chinese-speaking threat actor has been observed using the DeepSeek artificial intelligence model in conjunction with the open-source Hermes Agent to conduct autonomous cyberattacks against internet-exposed servers. This activity, attributed to an individual operating under the aliases "knaithe" and "KnYuan," was uncovered by researchers at Palo Alto Networks' Unit 42.
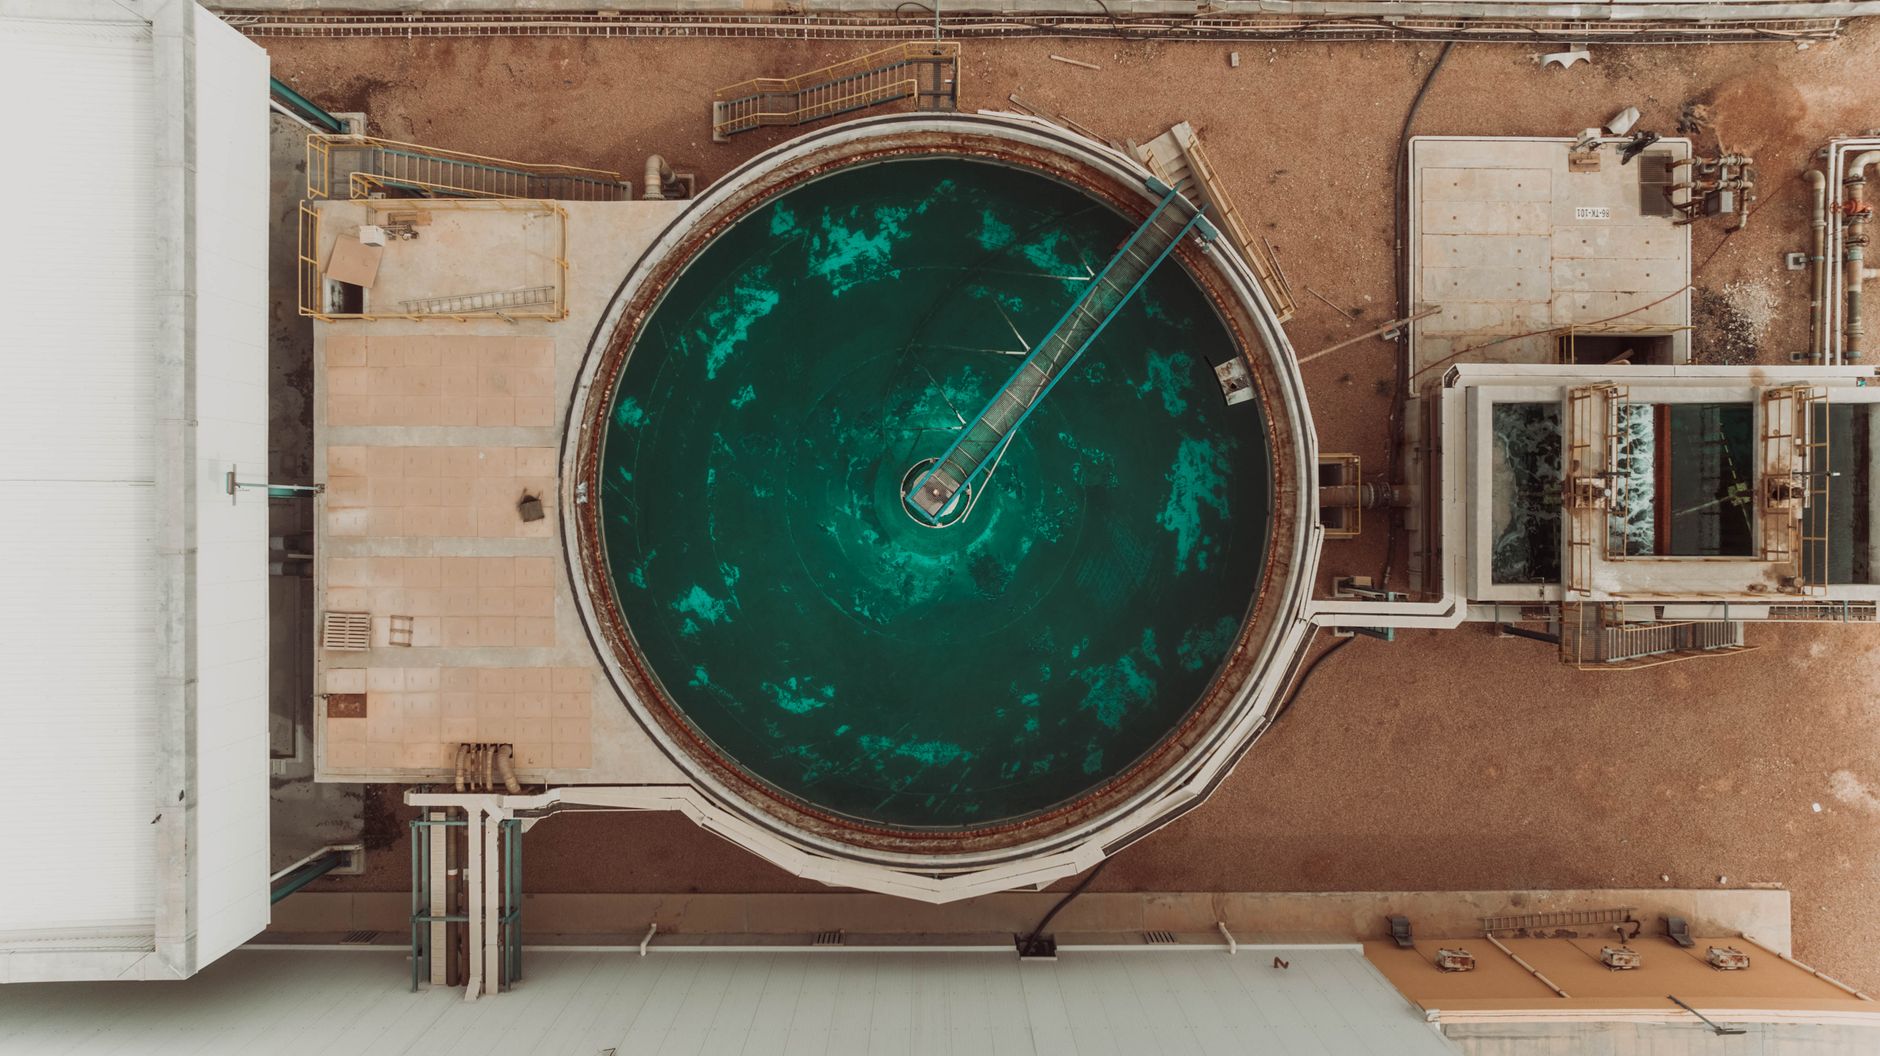
CISA warns of cyberattacks disrupting U.S. water utilities
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert regarding a significant increase in cyberattacks targeting internet-exposed programmable logic controllers (PLCs) within the water and wastewater systems sector. This warning follows a series of disruptions affecting over 30 community water systems in Minnesota, with attacks commencing last Sunday and…
What an LLM Can Find: A Practical, Cheap Path to Code-level Threat Discovery
A recent security audit of the GlobaLeaks whistleblowing platform, assisted by large language models (LLMs), uncovered 29 confirmed vulnerabilities, 12 denial-of-service issues, and 42 hardening recommendations. This review, which cost approximately $3,140 in API calls, suggests that LLM-assisted code analysis can significantly reduce the cost and time associated with large-scale security…
Facial Recognition at Madison Square Garden
Madison Square Garden Entertainment (MSGE) has confirmed its use of facial recognition technology at its venues, including Madison Square Garden, Radio City Music Hall, and the Beacon Theatre. The company states that the technology is employed to identify individuals who have been prohibited from entering their properties.
Hermes AI agent used to automate attack on Thai Finance Ministry
A threat actor allegedly utilized the open-source Hermes AI agent in an unattended "YOLO" mode to automate post-exploitation activities during a purported breach of Thailand's Ministry of Finance. This activity was uncovered by the threat intelligence firm Hunt.io and security researcher Bob Diachenko, who identified several exposed web directories containing files related to the operation.…
Chick-fil-A data breach affects more than 13,000 customers
Chick-fil-A has confirmed that a recent credential stuffing attack compromised the personal data of over 13,000 customers. The fast-food chain detected suspicious login activity on its website and mobile app, specifically targeting Chick-fil-A One loyalty accounts, between June 17 and June 19.
Data Breach Confirmed After Australian Energy Giant Origin Is Hacked
Origin Energy, a major Australian energy provider, has confirmed a data breach following claims by a hacker to have stolen information belonging to approximately 2 million of its customers. The threat actor has reportedly threatened to leak the stolen data if their demands are not met.
Australian energy provider Origin says data breach exposes client data
Origin Energy, a major Australian energy retailer, has confirmed a data breach that exposed personally identifiable information (PII) of some of its 4.8 million customers. The company, which provides electricity, natural gas, and broadband internet services, is currently investigating the full scope of the incident to notify affected individuals.
South Korea discloses data breach impacting diplomats worldwide
South Korea's Ministry of Foreign Affairs (MFA) has confirmed a data breach affecting the National Diplomatic Academy's online education system, leading to the exposure of personal information belonging to current and former employees, including diplomats stationed abroad. The breach, which occurred between April 2025 and February 2026, was attributed to an unknown threat actor exploiting a…
Chick-fil-A discloses data breach after credential stuffing attacks
Chick-fil-A has disclosed a data breach affecting an unspecified number of customers, attributing the incident to a series of credential stuffing attacks that targeted its website and mobile application in June. The fast-food chain, which operates over 3,000 restaurants across multiple countries, began notifying affected individuals through data breach letters filed with various Attorney…
Clover Health Investments Discloses Data Breach
Clover Health Investments has disclosed a data breach resulting from a social engineering attack. The incident led to the compromise of employee accounts, which subsequently provided unauthorized access to personal and health information.
PR3TACK preemptive framework maps threats before attackers use them
A new open framework, PR3TACK (Preemptive Tactics and Countermeasures Knowledgebase), aims to map potential attacker techniques before they are observed in active intrusions. Developed by Vishal Thakur of Atlassian, PR3TACK is designed to bridge the gap between the emergence of new attack methods and their documentation in defensive frameworks, which typically catalog techniques only after…
Estée Lauder discloses data breach via Oracle E-Business flaw
Estée Lauder, the global cosmetics firm, has confirmed a data breach stemming from an exploited vulnerability in its Oracle E-Business Suite (EBS) system, which the company utilized for human resources (HR) operations. The company's investigation determined that an unauthorized third party gained access to the system and obtained personal information of certain individuals on or around August…
Hugging Face Says Autonomous AI Agent System Breached Production Infrastructure
Hugging Face has reported a security incident where an autonomous AI agent system successfully breached a portion of its production infrastructure. The company indicated that the AI-led cyberattack resulted in unauthorized access to a limited number of datasets and service credentials.
Exposed Server Reveals AI-Assisted Phishing Toolkit Behind WebDAV Malware Campaign
Security researchers at Rapid7 have reportedly uncovered an AI-assisted phishing toolkit after a malware operator inadvertently exposed their delivery server. The server, left wide open, contained 1,048 files, offering a comprehensive look into the attacker's operations. This cache included lure templates, tests for filename spoofing, execution experiments, various droppers, builder notes, and…
20th July – Threat Intelligence Report
Ernst & Young, a global accounting and professional services firm, has disclosed a data breach stemming from a compromised third-party IT support platform. The incident potentially exposed sensitive information, including client documents, tax details, and employee data, which had been submitted in support tickets.
Hugging Face breached by autonomous AI agent
Hugging Face, a prominent platform for open-source machine learning models and datasets, has confirmed a security breach that it attributes to an autonomous AI agent system. The company disclosed the incident in a blog post published on Thursday, July 16, following the detection of unauthorized access earlier that week.
More alerts are making your team slower, and an outcome-based SOC fixes that
--- Source 2 --- Rapid7 Unveils AI-Powered SOC Platform to Combat Alert Fatigue and Accelerate Threat Response
Your Period Tracker Is (Probably) Spying on You
A recent audit by the Mozilla Foundation, conducted in partnership with Harvard's Berkman Klein Center, has revealed significant privacy concerns with several popular period tracking applications, with one app, Stardust, scoring particularly low. The audit examined six widely used trackers, finding that most engaged in data sharing practices that could compromise user privacy.
New TrojPix Attack Leaks Data From Air-Gapped Systems via Video Cable Emissions
Researchers have developed a novel method, dubbed TrojPix, capable of exfiltrating data from air-gapped systems by manipulating on-screen pixels. This technique exploits the electromagnetic emissions generated by video cables to transmit sensitive information.
U.S. Government Entity Paid Kairos $1 Million in Data-Theft Extortion Case
A U.S. government entity reportedly paid approximately $1 million to a cybercriminal group named Kairos to prevent the leak of stolen data. This information comes from a case study published by Ransom-ISAC, which analyzed a leaked negotiation transcript and the blockchain records associated with the payment.
Attackers Seize Exposed AI Endpoints to Power Offensive Ops
Cybercriminals are reportedly exploiting publicly accessible artificial intelligence (AI) endpoints to fuel their malicious operations. The exact nature of these offensive operations is not detailed, but the exploitation of AI infrastructure indicates a new avenue for threat actors.
Iran, Russia, China Target Water Systems for Sabotage
Nation-state actors, reportedly from Iran, Russia, and China, have successfully infiltrated industrial control systems within the water sector, exploiting basic security vulnerabilities rather than advanced malware. These attacks have targeted Programmable Logic Controllers (PLCs) that manage critical water infrastructure operations.
Third-Party Breaches Teach Education Sector a Costly Lesson in Vendor Risk
The education sector is facing increasing risks from third-party breaches, prompting institutions to bolster their defenses against attacks targeting sensitive student data. These attacks often involve ransomware and other malicious activities, highlighting a critical need for improved vendor risk management.
Maine forced to take down data breach portal after fake notices filed with authorities
The state of Maine has temporarily taken down its public data breach notification portal after malicious actors submitted fraudulent breach disclosures, impersonating well-known technology companies. The false reports were publicly posted before their authenticity could be verified, leading the named companies to deny any breach had occurred.
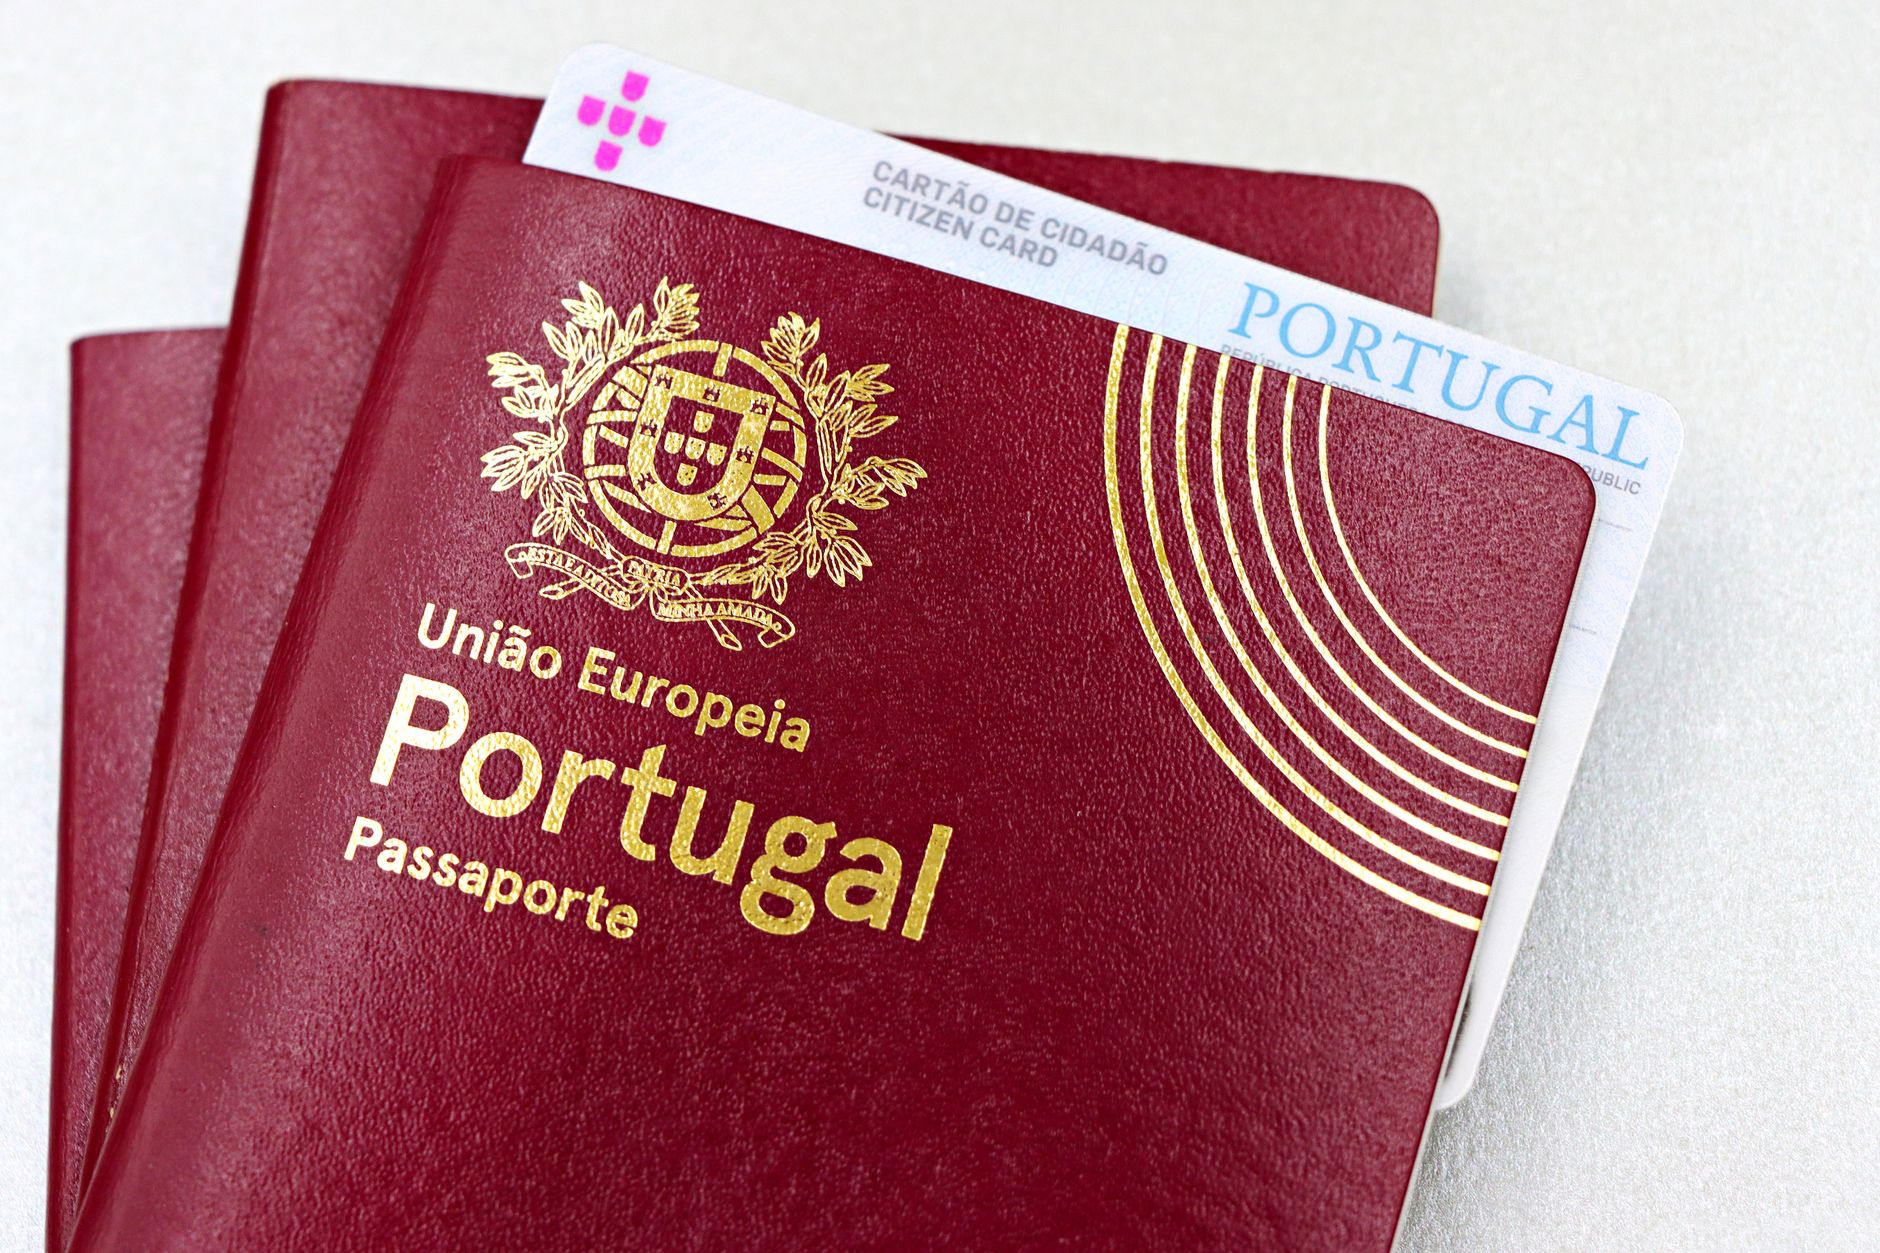
Privacy own-goal: World Cup blunder leaks Lionel Messi’s passport details
Details from the passports of every player on Argentina's World Cup squad, including star player Lionel Messi, were inadvertently leaked to the public ahead of a recent match. The sensitive information was present on an official team sheet circulated before a friendly game against Iceland.
Weekly Update 507
A cybersecurity data breach tracking initiative has surpassed a significant milestone, having now documented over 1,000 separate data breaches. This achievement represents not only the collection and verification of breach data but also the extensive operational efforts required to maintain the service.
1,000 Data Breaches Later, the Disclosure Lag is Worse Than Ever
The 1,000th data breach has been added to the Have I Been Pwned (HIBP) service, a milestone that prompts reflection on the persistent need for such tools. The ongoing accumulation of data breaches suggests that the time lag between a breach occurring and its public disclosure may be worsening.
Weekly Update 506
A recent wave of data breaches attributed to the threat actor group ShinyHunters has brought renewed attention to the challenges organizations face in responding to and disclosing such incidents. While the criminal nature of these attacks is evident, the varying degrees of organizational response, including instances of non-disclosure, highlight ongoing issues in cybersecurity incident…
MyPillow listed on ransomware gang’s leak site, but denies it has been breached
The ransomware group known as Play is claiming to have exfiltrated data from the US-based pillow manufacturer MyPillow. The group posted on its dark web leak site that it had obtained private and personal confidential information. Play threatened to release an unspecified amount of this data on Friday, potentially exposing documents related to clients, budgets, payroll, identification, taxes,…
Lawmakers Demand Answers as CISA Tries to Contain Data Leak
Lawmakers on Capitol Hill are demanding answers from the U.S. Cybersecurity & Infrastructure Security Agency (CISA) following a report that a contractor intentionally exposed a significant amount of sensitive agency data, including AWS GovCloud keys, on a public GitHub account. The breach has prompted an inquiry from both houses of Congress as CISA works to mitigate the fallout and revoke the…
CISA Admin Leaked AWS GovCloud Keys on Github
A contractor for the Cybersecurity & Infrastructure Security Agency (CISA) inadvertently exposed highly privileged credentials for AWS GovCloud accounts and numerous internal CISA systems through a public GitHub repository. Security experts have described the leak as one of the most significant government data exposures in recent history, containing details on CISA's internal software…
Weekly Update 504
The debate surrounding whether to pay ransoms to cybercriminals to prevent data leaks continues to be a significant concern for organizations. In a recent development, Grafana, a popular open-source analytics and monitoring solution, reportedly chose not to pay a ransom demand. This decision comes amidst ongoing discussions about the efficacy and ethical implications of ransom payments in the…