
vulnerability news
725 stories · page 4 of 16
SonicWall warns of new SSL-VPN MFA bypass flaw exploited in attacks
SonicWall has issued an urgent security advisory regarding a critical vulnerability in its SonicOS firewalls that allows attackers to bypass multi-factor authentication (MFA). The flaw, tracked as CVE-2026-19868, carries a CVSS severity score of 7.1 and specifically impacts SSL-VPN services configured to utilize SAML authentication. By leveraging valid credentials for an alternative…
Turning Up the Heat: Inside the Attacks on Europe’s Refrigeration System
A series of coordinated cyberattacks targeting industrial refrigeration systems across Europe has caused significant operational disruptions, leading to widespread food spoilage and safety concerns. The campaign, which began in mid-October 2026, has expanded from an initial focus on French supermarkets to affect at least 10 other European countries. While the primary impact has been on the…
OpenAI's new GPT-6 Cyber AI finds 81 Firefox flaws, 948 Linux bugs
OpenAI has unveiled GPT-6 Cyber, a specialized artificial intelligence model designed for vulnerability research and exploit development. According to the company, this model represents a significant leap in capability over its predecessor, GPT-5.6 Cyber, achieving a 48.5% success rate in the ExploitGym benchmark compared to the 32.1% rate recorded by the previous version. OpenAI has formally…
WP Wham Checkout Files Upload for WooCommerce Flaw Exploited on Disclosure Day
The WP Wham Checkout Files Upload for WooCommerce plugin vulnerability CVE-2026-103688 was identified as exploited on the same day it was published.
Cisco Secure Firewall ASA and FTD Software Flaw Exploited Upon Disclosure
Cisco Secure Firewall ASA and FTD software are vulnerable to a NULL pointer dereference, with exploitation confirmed on the same day as the CVE publication.
Pie Register Premium Unrestricted File Upload Flaw Exploited Before Disclosure
The Pie Register Premium plugin vulnerability CVE-2026-84999 was identified as exploited one day before its official CVE publication, leaving users with no patch window.
GFI KerioConnect Vulnerability Exploited Same Day As Disclosure
The GFI KerioConnect vulnerability CVE-2026-112353 was identified as exploited on the same day it was published, leaving organizations with no time to patch before active exploitation.
Spesmilo Electrum Improper Cryptographic Signature Verification Exploited Upon Disclosure
The vulnerability CVE-2026-117601 in Spesmilo Electrum was identified as exploited on the same day it was published, leaving no window for remediation.
Certificate authority DigiCert reports data breach involving business customer info
DigiCert, a prominent certificate authority, has disclosed a data breach involving an internal business system that was inadvertently exposed to the public internet. The incident, which the company detailed in a post-mortem report submitted to Mozilla’s Bugzilla platform, stemmed from a configuration error during a network migration. While the company has confirmed the unauthorized access, it…
7 Best Vulnerability Scanning Tools for Lean Security Teams in 2026
A recent industry analysis has identified seven vulnerability scanning tools specifically optimized for lean security teams operating in the 2026 threat landscape. These solutions are designed to address the resource constraints faced by smaller organizations, focusing on streamlined deployment and automated workflows. The evaluation criteria for these selections centered on ease of setup, the…
QNAP says hackers breaching NAS devices in Plex2Shell attacks
QNAP has issued a formal security advisory warning users of its network-attached storage (NAS) devices regarding a series of active cyberattacks targeting the Plex Media Server application. The company reports that attackers are leveraging a vulnerability chain collectively referred to as Plex2Shell to gain unauthorized access to these storage systems. QNAP confirmed that it is currently…
Installing the Fix for an Exploited WordPress Flaw Can Expose Some Sites One Last Time
WordPress sites currently undergoing the patching process for a recently identified, actively exploited vulnerability may remain susceptible to attack during the update sequence itself. According to research from Umut Bayram of Picus Security, the mechanism used to deploy the fix inadvertently relies on the very code that is being replaced, creating a brief window of exposure for…
Hackers Target OpenSSH SSHole Flaw Within Hours of Disclosure, Gain Root on Honeypot
Threat actors have begun actively exploiting a recently disclosed security vulnerability in OpenSSH, identified as CVE-2026-123158 and codenamed SSHole, within hours of its public disclosure. According to reports from Previdian, the flaw allows unauthorized individuals to gain root access to affected systems by signing into accounts that do not have a password configured. Researchers confirmed…
OpenAI Launches GPT-6 Cyber After AI Helps Find 81 Firefox Flaws, 948 Linux Exploits
OpenAI has officially unveiled GPT-6 Cyber, a specialized iteration of its large language model architecture designed specifically for cybersecurity research. The company reports that the new model integrates enhanced defensive capabilities with significant advancements in alignment technology, aiming to improve both the identification of software vulnerabilities and the reliability of the…
Unpatched AhsayCBS flaws exploited to deploy webshells, mine crypto
Threat actors are actively exploiting two unpatched vulnerabilities in the AhsayCBS backup management platform to deploy webshells and cryptocurrency miners. The targeted attacks, first observed on October 7, have affected at least five organizations, primarily managed service providers (MSPs) and system integrators.
Citrix warns admins to patch new NetScaler RCE flaw immediately
Citrix has issued an urgent advisory to administrators regarding a new critical vulnerability, tracked as CVE-2026-107406, affecting its NetScaler ADC networking appliances and NetScaler Gateway secure remote access solutions. The company is urging immediate patching to mitigate the risk of remote code execution (RCE) or denial-of-service (DoS) attacks.
Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security
Anthropic has reportedly initiated a program to fast-track AI-generated vulnerability reports to open-source software (OSS) maintainers. This new system, dubbed "OSS Scanner," is designed to automatically generate and dispatch bug reports. The reports are sent directly to maintainers who have opted into the program, raising questions about the review process for these AI-generated findings.
Hackers get $1,262,000 for 98 zero-days at Pwn2Own Ireland
The Pwn2Own Ireland 2026 hacking competition concluded with security researchers earning a total of $1,262,000 for demonstrating 98 unique zero-day vulnerabilities across various products. The three-day event, organized by Trend Micro's Zero Day Initiative (ZDI), saw 29 research teams targeting devices in seven categories, including mobile phones, AI infrastructure, and smart home devices.
'AgentCorruption' Puts AWS Environments At Risk With Single Prompt
A recently disclosed vulnerability, dubbed 'AgentCorruption,' reportedly allowed attackers to compromise AWS environments through a single prompt directed at an AI chatbot. The flaw, now patched, was identified within AWS Bedrock AgentCore and could have enabled an attacker to gain control over an organization's entire fleet of AI agents.
Cisco Patches a Dozen Critical Vulnerabilities
Cisco has released patches addressing a dozen critical vulnerabilities across its product line. These security defects reportedly encompass a range of potential impacts, including unauthorized access, information leaks, privilege escalation, denial-of-service (DoS) attacks, and remote code execution (RCE). The widespread nature of these reported flaws suggests a significant security update…
Cisco warns of critical flaws allowing Nexus switch takeover
Cisco has issued a warning regarding five critical vulnerabilities identified in its NX-OS data center network operating system, which could enable attackers to execute arbitrary code with root privileges on Nexus switches. In scenarios where remote code execution is not achievable, exploitation of these flaws could lead to process crashes and device reloads, resulting in denial-of-service…
Chasing AMMYY at Splunk .conf
A recent report detailed the detection of Flawed AMMYY RAT traffic at the Splunk .conf event, an incident uncovered through the combined capabilities of Cisco's Encrypted Visibility Engine (EVE) and Endace PCAP. The key takeaway from this discovery was the ability to identify this malicious activity without the need to decrypt TLS-encrypted communications, highlighting advancements in network…

Four Compliance Frameworks, One Security Team. How Universities Can Stop Drowning in Regulatory Risk
Universities face a uniquely complex regulatory landscape, often requiring compliance with four distinct federal frameworks simultaneously, each with its own security requirements, reporting timelines, and potential penalties. This challenge is compounded in multi-campus systems where IT environments, tools, staff, and data governance practices may vary by institution. The scale of the threat…
Microsoft, Adobe, Apple, and Foxit vulnerabilities
Cisco Talos's Vulnerability Discovery & Research team has recently disclosed a series of vulnerabilities affecting products from Microsoft, Adobe, Apple, and Foxit. All identified vulnerabilities have reportedly been patched by their respective vendors, aligning with Cisco's responsible disclosure policies. The issues range from privilege escalation and information disclosure to remote code…
Exploitation attempts against critical Atlassian flaw have begun (CVE-2026-21589)
Exploitation attempts have begun against a critical arbitrary file access vulnerability, CVE-2026-21589, affecting multiple self-managed Atlassian Data Center products. The attempts were observed by threat intelligence vendor Previdian on Tuesday, just one day after Atlassian released patches and hours after security researchers published a technical analysis of the flaw.
Gremlin Foresight AI finds system weaknesses and verifies the fixes
Gremlin has announced the general availability of Gremlin Foresight AI, a new platform designed to identify and address reliability risks in production systems. The company states that the AI-powered tool can proactively detect potential weaknesses, recommend and deliver specific fixes, and then validate those fixes by re-running the original tests.
Android’s October 2026 Updates Patch 25 Vulnerabilities
Android’s October 2026 security updates have addressed a total of 25 vulnerabilities across the platform. Among these, a critical flaw within Android’s System component has been highlighted, which could potentially allow for privilege escalation on affected devices. The updates are designed to enhance the overall security posture of Android devices by resolving these identified weaknesses.
Atlassian Patches Critical Vulnerability Affecting 8 Products
Atlassian has released patches for a critical vulnerability impacting eight of its products. The flaw, if exploited, could allow unauthenticated attackers to gain access to specific files located within the web application's root directory. This type of access could potentially expose sensitive configuration or application data, depending on the contents of the accessible files.
OpenSSH 10.6 enables a post-quantum signature algorithm, so experimental keys need replacing
The OpenSSH project released version 10.6 on October 6, introducing a new hybrid post-quantum signature algorithm and addressing several security vulnerabilities. The maintainers indicated that future releases may occur more frequently to expedite bug fixes, noting a rise in security reports, many identified with the assistance of AI models.
Automation, AI agents or people? Sorting out who handles each security finding
A recent survey of 200 senior security and technology leaders reveals significant concerns about the escalating complexity of software security programs, particularly in the wake of increased AI adoption. Over half of the respondents, primarily from companies with 10,000 or more employees, anticipate struggles in simplifying their security operations if current practices persist.
Check your X.Org server version because a dozen vulnerabilities have been patched
X.Org has released patches for a dozen security vulnerabilities affecting its X server and Xwayland components, with updates available in versions xorg-server 21.1.25 and xwayland-24.1.14. Nine of these flaws are critical, potentially allowing for arbitrary code execution, while the remaining three could lead to server crashes or information disclosure.
Ninja Forms plugin flaw exploited to hack WordPress sites
Cybersecurity researchers have identified an active exploitation campaign targeting two WordPress plugins, Ninja Forms and WPC Product Bundles for WooCommerce, leveraging stored cross-site scripting (XSS) vulnerabilities to compromise websites. The attacks, first observed on October 4 against WPC Product Bundles for WooCommerce users and then on October 5 against Ninja Forms users, involve the…
Google's PageBreak AI Agent Finds 500 Flaws in Its Web Apps
Google has reportedly developed an artificial intelligence agent, named PageBreak, which has identified approximately 500 flaws within Google's own web applications. This development highlights an emerging trend in the cybersecurity industry: the application of AI and deterministic validation methods to automate the discovery of vulnerabilities, assess their exploitability, and provide a…
Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access
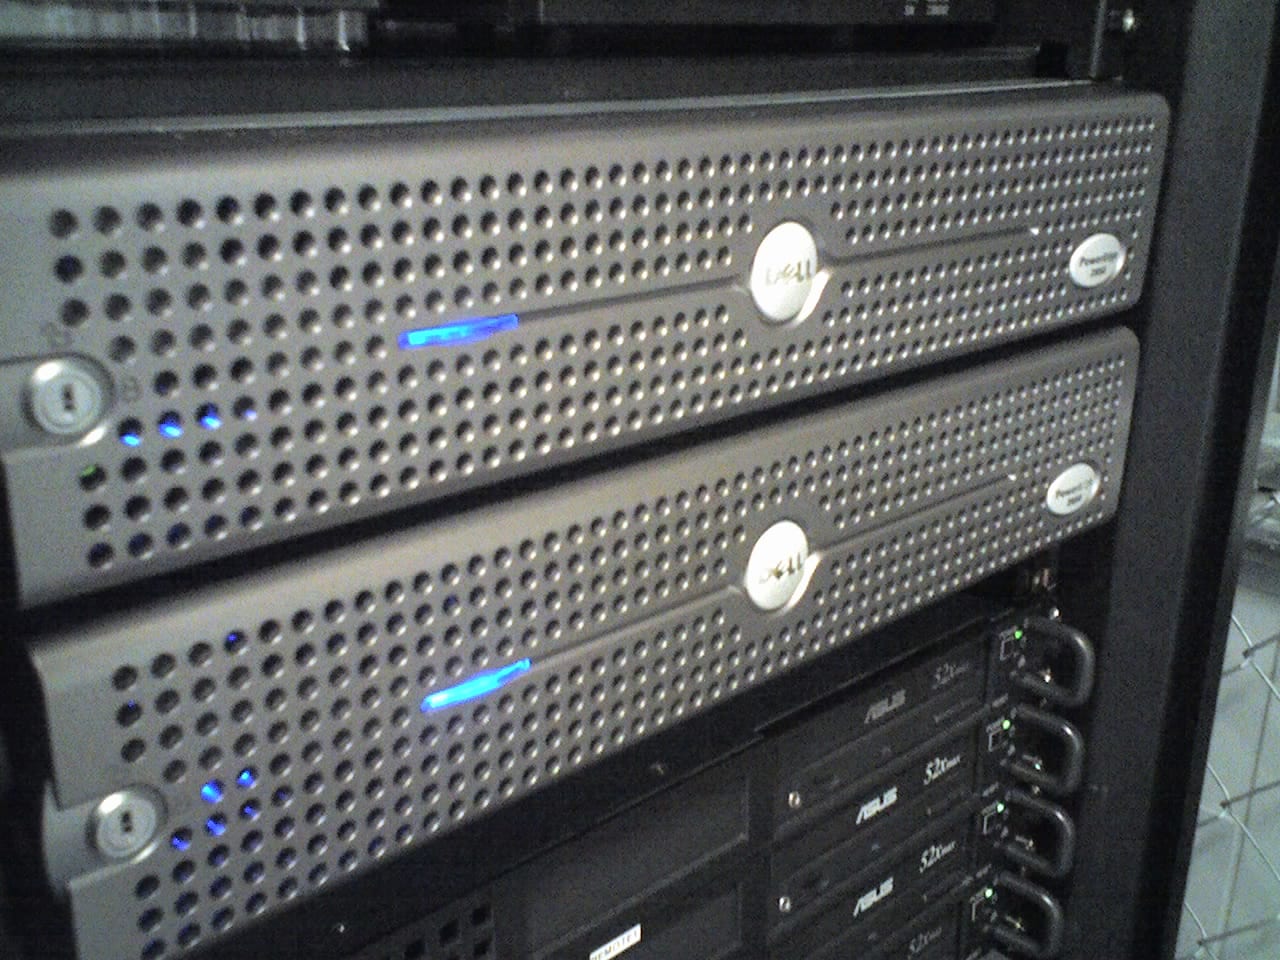
Dell has issued an urgent advisory to customers, recommending they patch a critical vulnerability in its System Update (DSU) tool that could allow attackers to gain root access on affected PowerEdge servers. The flaw, identified as CVE-2026-86360, carries a CVSS score of 9.6, indicating its severe potential impact.
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products
A critical vulnerability has been reported in eight Atlassian Data Center products, enabling unauthenticated attackers to read known files within the web application root directory. The flaw, identified as CVE-2026-21589, was disclosed by Atlassian on October 5th and carries a CVSS rating of 9.3 out of 10, indicating its severe impact and ease of exploitation.
Citrix NetScaler Hit by Third Actively Exploited Zero-Day
Citrix has disclosed a third actively exploited zero-day vulnerability affecting its NetScaler products, identified as CVE-2026-88779. This latest flaw, a denial-of-service vulnerability, specifically impacts NetScaler instances where Security Assertion Markup Language (SAML) is enabled. While inconvenient, security researchers generally consider its impact to be lower compared to the two…
Citrix NetScaler security snafus get even worse amid more 0-day reports
Citrix has confirmed a new zero-day vulnerability, CVE-2026-88779, affecting its NetScaler ADC and Gateway appliances, which is already being actively exploited in the wild. The flaw is a memory overflow bug that can lead to denial of service attacks.
Rejetto HFS servers now actively scanned for critical RCE flaw
Rejetto HFS servers are currently experiencing active scanning for a critical remote code execution (RCE) vulnerability, identified as CVE-2026-61500. This flaw, which allows for session forgery and account takeover, was first disclosed on July 13, 2026, and details of a proof-of-concept (PoC) exploit were publicly released on September 30, 2026.
Google halts open-source bug bounty program amid AI spam surge
Google has temporarily suspended submissions for product vulnerabilities to its Open Source Software Vulnerability Rewards Program (OSS VRP), effective October 1, 2026. The company cited a significant increase in automated submissions, most of which were deemed invalid, as the reason for the pause.
AI slop submissions force Google to freeze its open-source bug bounty
Google has temporarily halted its Open Source Software Vulnerability Reward Program (OSS VRP) for new product vulnerability submissions, effective October 1, 2026. The company cited a substantial increase in automated, AI-generated reports, most of which were invalid, as the reason for the pause. This influx of low-quality submissions overwhelmed the engineers and open-source maintainers…
Exploitation of Citrix NetScaler Zero-Day Hits Appliances Patched Days Earlier
Citrix has confirmed the active exploitation of a new zero-day vulnerability, identified as CVE-2026-88779, affecting its NetScaler appliances. This new flaw reportedly emerged and was exploited just days after the company released patches for two other previously exploited vulnerabilities in the same product line.
Citrix NetScaler Flaw Exploited Before CVE Publication
The CVE-2026-88779 vulnerability in Citrix NetScaler was exploited before its official publication date. A second independent catalogue now confirms exploitation.
Citrix patches NetScaler SAML zero-day exploited in attacks
Citrix has issued urgent security updates for a new zero-day vulnerability, identified as CVE-2026-88779, affecting its NetScaler ADC and NetScaler Gateway appliances. The flaw, described as a memory buffer issue, has been actively exploited in targeted attacks, primarily leading to denial-of-service conditions.
NetScaler CVE-2026-88779 Exploited Before Publication
NetScaler's CVE-2026-88779 was exploited before its official publication date, leaving no patch window. The European Union's EUVD catalogue lists it as exploited.
dompdf_project dompdf XSS flaw added to VulnCheck KEV
CVE-2022-28368, a cross-site scripting vulnerability in dompdf, was added to the VulnCheck Known Exploited Vulnerabilities catalogue. The flaw has a high EPSS score but is not listed by CISA or ENISA.
Week in review: Researcher breaks into Microsoft analytics service, NetScaler RCE 0-day exploited
A 16-year-old security researcher has identified a vulnerability in Microsoft's internal analytics service, Titan, which could have exposed employee records and Bing search analytics. The flaw reportedly provided access to 17 trillion rows of data. Microsoft has not yet issued a public statement confirming the details of the vulnerability or its remediation.
Warlock Ransomware Still Exploits Year-Old SharePoint Flaws to Hit Critical Infrastructure
The Warlock ransomware group, tracked by Symantec as Longlegs and also known as Storm-2603, continues to exploit unpatched vulnerabilities in Microsoft SharePoint, more than a year after these flaws were initially publicized. The group, which has historical ties to China-nexus clusters CL-CRI-1040, CamoFei, and ChamelGang, has recently targeted critical infrastructure, including water…
Zyxel GS1900 Switch Flaw Exploited, Now in EU Catalogue
A stack-based buffer overflow in Zyxel GS1900-48HPv2 switches is now listed in the EU's common vulnerabilities exploited catalogue, following its inclusion in the US federal list.