
vulnerability news
725 stories · page 3 of 16
Meow Apps AI Engine Vulnerability Exploited On Day Of Disclosure
The Meow Apps AI Engine plugin was identified as exploited on the same day its vulnerability was published, leaving users with no patch window.
N-able Takes N-central Platform Offline After Discovery of 33 Flaws
N-able has taken its N-central remote monitoring and management (RMM) platform offline following the discovery of 33 security vulnerabilities. The company initiated this service interruption to address the flaws, which reportedly include zero-day vulnerabilities that could allow an unauthorized attacker to achieve full system takeover.
Git fixes six vulnerabilities, including code execution during recursive clones
The Git project has released a series of security updates addressing six distinct vulnerabilities that could allow for unauthorized code execution, memory corruption, or arbitrary file manipulation. These flaws are triggered when the software processes malicious repositories or specially crafted inputs. The patches are included in Git version 2.56.1, with backported fixes available for the…
N-able releases security hotfixes for zero-day vulnerabilities
N-able has released security hotfixes for its N-central remote monitoring and management platform following the public disclosure of several critical zero-day vulnerabilities. The company issued version 2026.4 HF2 to address these flaws, which were initially brought to light on November 8, 2026. The vulnerabilities affect the N-central Appliance 2026.4.0.31, though it is believed that earlier…
Microsoft Fixes 1235 Flaws in Another Record Patch Tuesday
Microsoft has released its November security updates, addressing a total of 1,235 vulnerabilities across its product ecosystem. This release marks the fourth time in 2026 that the company has set a new record for the number of patches issued in a single month, following similar milestones in July, September, and October.
Cisco BroadWorks and Openwave Flaws Actively Exploited Despite Available Patches
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two security vulnerabilities affecting Cisco BroadWorks and the Openwave Messaging Webtop Media Transcoder to its Known Exploited Vulnerabilities (KEV) catalog. The agency’s inclusion of these flaws indicates that they are currently being leveraged in active, real-world attacks. Organizations utilizing these platforms…
EU cyber scores look healthy, but 45% of surveyed IT providers take months to patch
The European Union’s cybersecurity landscape presents a significant disconnect between high-level national policy scores and the operational realities of service providers, according to the 2026 assessment released by the European Union Agency for Cybersecurity (ENISA). While the agency’s revised EU Cybersecurity Index reports an average score of 71.53 out of 100 across member states, a…
Nearly half of big firms shelve or close vulnerability findings they haven’t confirmed
Large enterprises are increasingly struggling to manage their vulnerability backlogs, with nearly half of organizations employing 5,000 or more staff members admitting to closing or deprioritizing security findings without conducting a full verification process. According to data from ProjectDiscovery, the primary driver for this behavior is a lack of time, as security teams find themselves…
An Instagram ad was all it took: Leaked exploit kits are hitting employees’ iPhones
Criminals are increasingly leveraging leaked exploit kits to compromise iPhones, creating significant security risks for corporate environments where employees use personal devices for work. According to the 2026 Advanced Mobile Threat Report from iVerify, two specific toolkits, DarkSword and Coruna, are being deployed through malicious advertisements and compromised websites to target iOS…
SliceWP Affiliate Program Suite SQL Injection Exploited Before Disclosure
The SliceWP affiliate_program_suite plugin was identified as exploited one day before its official CVE publication, leaving users with no patch window.
CLavaque s2Member Improper Control of Generation of Code Flaw Exploited Upon Disclosure
The CLavaque s2Member plugin vulnerability CVE-2026-86596 was identified as exploited on the same day it was published, leaving no time for a patch window.
Microsoft Office Outlook Vulnerability Exploited Same Day as Disclosure
Microsoft Office Outlook vulnerability CVE-2026-124194 was identified as exploited on the same day it was published, leaving no window for remediation before active attacks.
Rocklobster Contact Form 7 Flaw Exploited Same Day as Disclosure
The rocklobster Contact Form 7 plugin vulnerability CVE-2026-114432 was identified as exploited on the same day it was published, leaving no window for remediation.
Revmakx WP Duplicate Flaw Exploited Before CVE Publication
The Revmakx WP Duplicate plugin vulnerability CVE-2026-123751 was identified as exploited two days before its official CVE publication date.
November Patch Tuesday boasts over 1,000 bugs but only one zero-day so far
Microsoft has released its November security updates, addressing a total of 1,094 vulnerabilities across its product ecosystem. This marks the second consecutive month in which the company has issued fixes for more than 1,000 bugs, a trend that security researchers attribute to the increased use of automated bug-hunting tools and artificial intelligence in both vulnerability discovery and…
November Patch Tuesday: An Overflowing Cornucopia of CVEs
Microsoft has released its November security update cycle, addressing a broad array of vulnerabilities across its enterprise software ecosystem. The release is headlined by an actively exploited zero-day vulnerability in Outlook, alongside a significant volume of critical flaws affecting Exchange Server, SharePoint, Windows Search, and LDAP implementations.
Microsoft’s Patch Tuesday surpasses 1,000 bugs for second month in a row
Microsoft has released its latest monthly security update, marking the second consecutive month in which the company has disclosed more than 1,000 vulnerabilities. The November release includes 1,093 distinct security flaws, contributing to a record-breaking year for the vendor, which has now disclosed over 5,160 vulnerabilities throughout 2026. This volume of disclosures significantly exceeds…
Windows 11 KB5132061 & KB5131087 cumulative updates released
Microsoft has released its November 2026 Patch Tuesday cumulative updates, designated as KB5132061 and KB5131087. These mandatory updates apply to Windows 11 versions 23H2, 24H2, 25H2, and 26H2. As part of the company’s monthly security cycle, these releases address hundreds of vulnerabilities identified in previous months. Users can obtain the patches through the standard Windows Update…
Adobe Patches 110 Vulnerabilities Across 9 Products
Adobe released its November 2026 security updates, addressing approximately 110 vulnerabilities across nine distinct software products. The patches cover a wide range of security flaws, including critical-severity issues that could potentially allow for arbitrary code execution or privilege escalation if successfully exploited.
Anthropic Rolls Out Mythos 5.2 With Improved Bug Hunting, Fewer Sandbox Escapes
Anthropic has officially released Claude Mythos 5.2 and Claude Fable 5.2, the latest iterations of its AI models designed for specialized security and general-purpose tasks. While both models share the same underlying architecture, they differ significantly in their operational guardrails. Mythos 5.2 is an access-restricted model intended for vetted organizations participating in Anthropic’s…
IBM Aspera Faspex, SignalWire FreeSwitch Vulnerabilities Exploited in Attacks
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent directive for federal agencies to remediate two critical vulnerabilities currently being exploited in the wild. The agency added CVE-2026-123218, affecting IBM Aspera Faspex, and CVE-2026-116779, impacting SignalWire FreeSwitch, to its Known Exploited Vulnerabilities (KEV) catalog. Under the requirements of…
Google patches eighth Chrome zero-day exploited in attacks this year
Google has issued an emergency security update for its Chrome web browser to address a high-severity vulnerability that is currently being exploited in the wild. This flaw, tracked as CVE-2026-125350, marks the eighth zero-day vulnerability patched by the company since the beginning of 2026.
Anthropic's super bug-finding Mythos model is going into Cisco and IBM products
Anthropic has announced a strategic expansion of its Mythos AI model, integrating the specialized bug-finding technology into enterprise security platforms managed by Cisco and IBM. This move marks a shift in how the company distributes its high-capability models, moving away from exclusive, vetted programs toward broader commercial availability within established security suites. Under these…
U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks
U.S. federal agencies have issued an urgent directive for critical infrastructure organizations to secure industrial refrigeration and cold-chain monitoring systems. This alert follows a series of cyberattacks that targeted supermarkets and blood banks across Europe, resulting in spoiled inventory and, in some instances, the triggering of fire hazards. The advisory, released jointly by the…
N-able takes cloud platform offline after 30+ "zero-days" published
N-able has initiated a global shutdown of its hosted N-central environments and issued an urgent directive for on-premises customers to take their servers offline following the public disclosure of over 30 alleged zero-day vulnerabilities. The flaws were published on November 8 by security researcher Sean Bales, who released a GitHub repository titled Able2Shell containing proof-of-concept…
Microsoft Fixes RCE Bug in Windows Paint After Weeks of Confusion
Microsoft has released a patch addressing a remote code execution vulnerability within the Windows Paint application, resolving a period of uncertainty regarding the status of the fix. The vulnerability, which was initially disclosed by the company last month, had left users and security professionals without clear guidance on whether a remediation was available or how to effectively secure…
Attackers Crash Claude's 'Office Party' Flaw to Run Malicious Code on Linux
Researchers have identified a security vulnerability in Anthropic’s Claude AI assistant that allows for the execution of malicious code on Linux-based systems. The flaw, dubbed "Office Party," centers on the document-processing tool used by the assistant, which can be manipulated to interact with the underlying host environment in unintended ways.
CISA Flags SonicWall SonicOS MFA Bypass Flaw Amid Reports of Possible Exploitation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has officially added a high-severity vulnerability affecting SonicWall SonicOS to its Known Exploited Vulnerabilities (KEV) catalog. The agency’s decision follows reports suggesting that the flaw, identified as CVE-2026-19868, may have already been leveraged in real-world exploitation attempts.
Linus Torvalds sees signs AI-prompted patch flood has peaked
The Linux kernel development community may be nearing the end of a period characterized by an overwhelming surge in software patches, according to observations from Linus Torvalds. In his recent update regarding the release of Linux 7.4 rc2, Torvalds noted that the volume of incoming bug reports, which has been significantly elevated by the use of artificial intelligence in vulnerability…
BTCPay Server Insufficiently Protected Credentials Flaw Exploited Upon Disclosure
The vulnerability CVE-2026-119757 in BTCPay Server was identified as exploited on the same day it was published, leaving no window for remediation.
LatePoint Improper Authentication Vulnerability Exploited Upon Disclosure
The LatePoint plugin for WordPress faces an authentication bypass vulnerability that was identified as exploited on the same day it was officially published.
ACF Extended Advanced Custom Fields PRO Flaw Exploited Upon Disclosure
The ACF Extended Advanced Custom Fields PRO plugin contains a critical file upload vulnerability that was identified as exploited on the same day it was published.
Elementor Website Builder Flaw Exploited Same Day As Disclosure
The Elementor Website Builder vulnerability CVE-2026-109884 was identified as exploited on the same day it was published, leaving no patch window for administrators.
SonicWall SonicOS SSLVPN Vulnerability Exploited On Day Of Disclosure
CVE-2026-19868 was added to major exploitation catalogues on the same day it was published, leaving no time for a patch window.
Scans for Sshole Vulnerability (CVE-2026-123158), (Sun, Nov 8th)
Security researchers operating honeypot infrastructure have reported a marked increase in exploitation attempts targeting the recently disclosed Sshole vulnerability, tracked as CVE-2026-123158. Observations gathered through Cowrie honeypots indicate that threat actors are actively scanning for systems susceptible to this flaw, which affects the Secure Shell (SSH) protocol implementation.
Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon Disclosure
The Wpmet wp_social_login_and_register_social_counter plugin vulnerability CVE-2026-103898 was identified as exploited on the same day it was published.
weDevs wp_project_manager Flaw Exploited Before CVE Publication
The weDevs wp_project_manager plugin was identified as under exploitation one day before the CVE was officially published, leaving users with no patch window.
Uncanny Toolkit for LearnDash Improper Authentication Exploited on Disclosure
The Uncanny Toolkit for LearnDash plugin was identified as exploited on the same day its CVE was published, leaving no window for remediation.
WordPress Core Time-of-Check Time-of-Use Vulnerability Exploited Before Disclosure
The WordPress Core TOCTOU race condition, CVE-2026-119977, was identified as exploited one day before its official publication, leaving no patch window for administrators.
Ivanti Connect Secure Vulnerability Exploited Before CVE Publication
The Ivanti Connect Secure missing authentication vulnerability was identified as exploited two days before its official CVE publication, leaving no patch window for administrators.
DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of Disclosure
The DedeCMS vulnerability CVE-2010-20125 was identified as exploited on the same day it was published, leaving no window for remediation.
Netsweeper Improper Neutralization Flaw Exploited Upon Disclosure
CVE-2015-20130 was identified as exploited on the same day it was published, leaving no patch window for administrators.
Dahua Intelligent Connection Center Flaw Exploited on Day of Disclosure
The Dahua Intelligent Connection Center vulnerability CVE-2025-31704 was identified as exploited on the same day it was published, leaving no window for remediation.
Gravity Forms Deserialization Flaw Exploited Upon Disclosure
The Gravity Forms plugin faces an active deserialization vulnerability that was identified as exploited on the same day it was published.
Drupal Commerce Core Access Bypass Exploited Before CVE Publication
The Drupal Commerce Core module vulnerability CVE-2026-118539 was identified as exploited two days before its official CVE publication date.
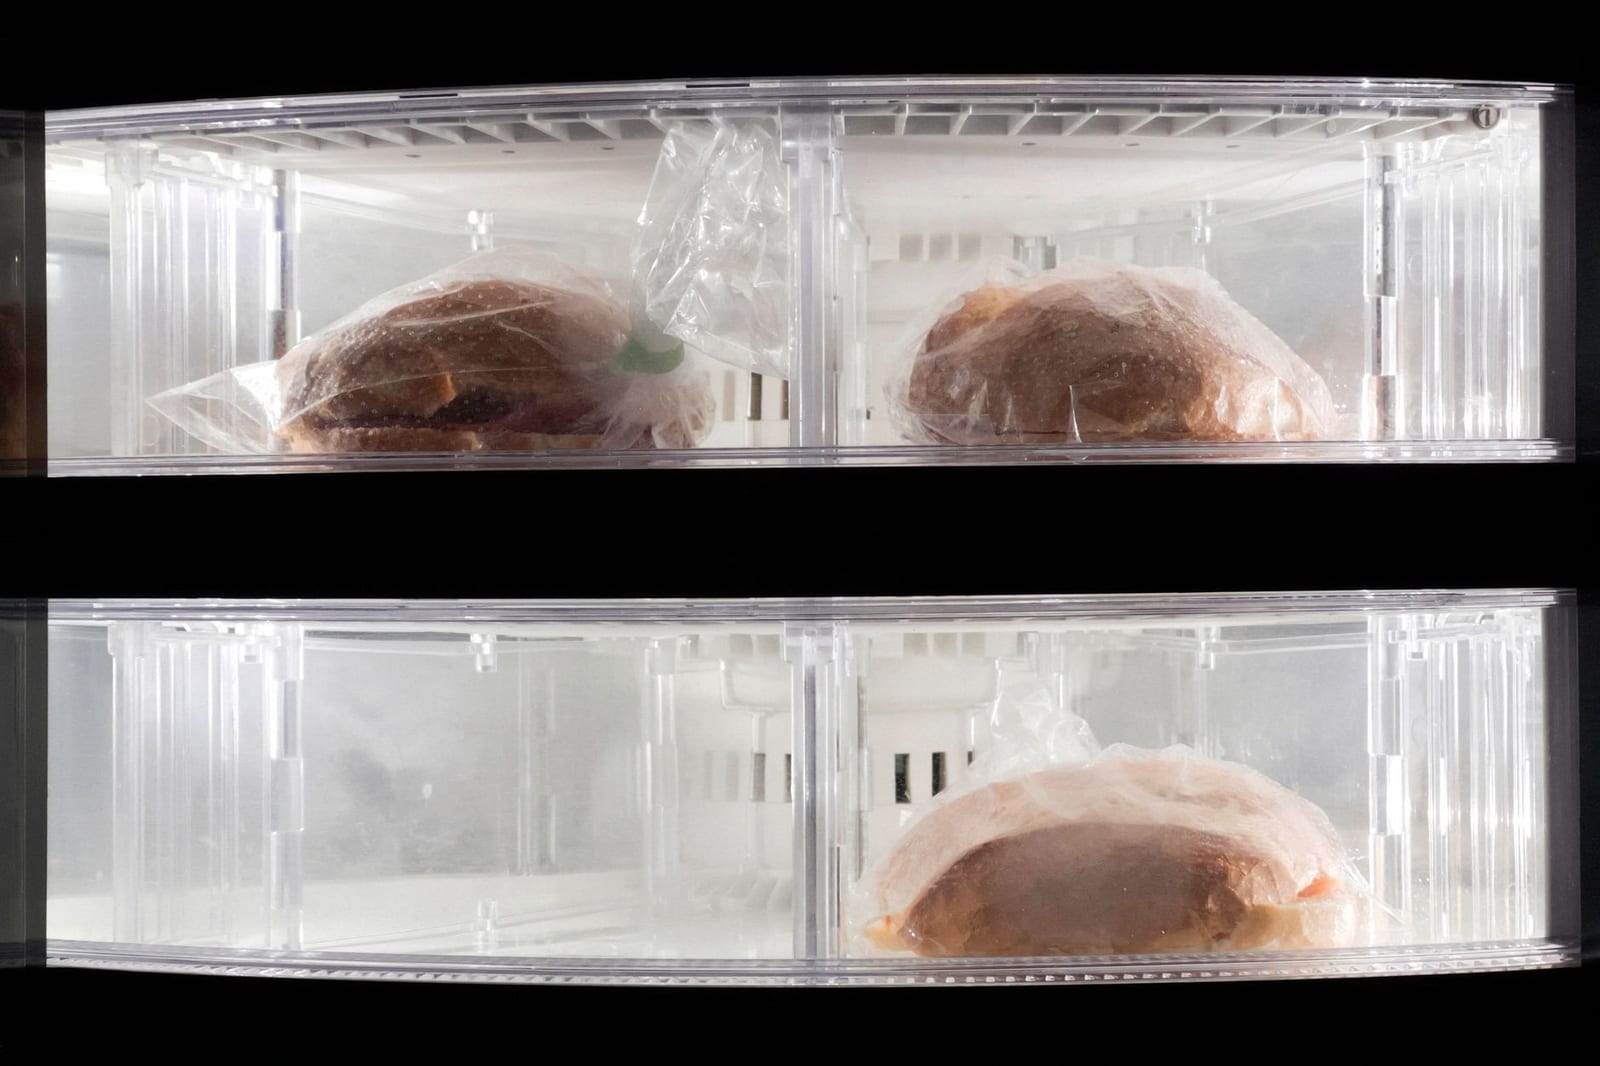
The Fridge-Hacking Spree Is an Internet-of-Things Wake-Up Call
A series of cyberattacks targeting internet-connected refrigeration systems has impacted critical infrastructure across Europe and the United States, raising concerns about the security of the global cold chain. The incidents, which involve unauthorized access to temperature controllers, have resulted in the spoilage of significant quantities of food and the disruption of sensitive medical…
SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins
SonicWall has issued emergency patches for its SonicOS operating system to address a high-severity authentication vulnerability currently being exploited in the wild. The flaw, tracked as CVE-2026-19868, resides within the SSL VPN component of the company’s firewall appliances. According to the vendor, the vulnerability allows an attacker who possesses valid credentials for an alternative…
U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has officially added a critical vulnerability affecting SonicWall SonicOS SSLVPN to its Known Exploited Vulnerabilities (KEV) catalog. The flaw, identified as CVE-2026-19868, carries a CVSS score of 7.5 and pertains to an authentication enforcement issue within the SSL VPN service.